 TrackMedia
 TrackRev
 Qodo
 Qodana
 CodeScene
 Code Climate
 Mend
 Black Duck
 GitGuardian
 Codecov
 Coveralls
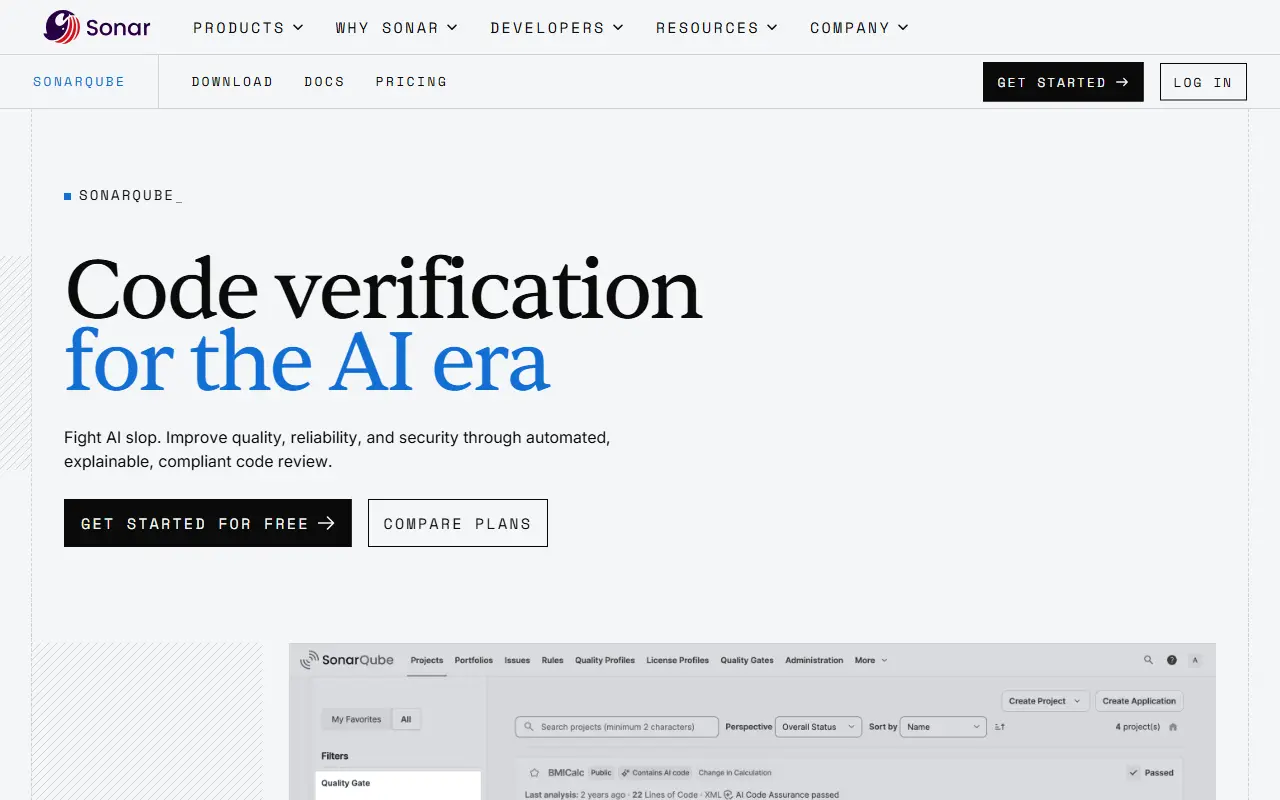
About SonarQube
SonarQube is a code quality and security platform. Its static analysis uses techniques such as symbolic execution and data and control flow analysis to inspect source code, find bugs and vulnerabilities, and explain what to fix and why. Results appear in the IDE, in pull requests and in CI pipelines.
This repository holds the source of the SonarQube Community Build, the free, open-source edition that shares the analysis used across the product line. It reports reliability bugs, security vulnerabilities and security hotspots, maintainability and structural issues, and coverage on new code. More than 40 programming languages and frameworks are covered, and the same code always produces the same findings.
The project positions itself as a verification step for code written by people or by AI agents before it merges. SonarQube is written in Java and licensed under LGPL-3.0. Commercial editions from SonarSource add further features, while the Community Build can be run on your own servers.
Key features
- Static analysis for bugs and vulnerabilities
- Security hotspot review guidance
- Maintainability and structural issue detection
- Coverage tracking on new code
- Support for 40+ languages and frameworks
- Feedback in IDE, pull requests and CI
Good fit for
- Gating pull requests on code quality
- Auditing codebases for security issues
SonarQube: questions and answers
- What is SonarQube used for?
- SonarQube is a static code analysis platform that finds bugs, vulnerabilities and maintainability problems in code, in IDEs, pull requests and CI. It is a good fit for gating pull requests on code quality and auditing codebases for security issues.
- Is SonarQube open source?
- Yes. SonarQube is open source under the LGPL-3.0 licence. Its source code is on GitHub at SonarSource/sonarqube and is written mainly in Java.
- Is SonarQube free?
- Yes. SonarQube is open source, so the software itself is free to use. Paid plans are also available, starting at $34 per month.
- Can I self-host SonarQube?
- Yes. SonarQube can be self-hosted on your own server or infrastructure.
- What is SonarQube an alternative to?
- SonarQube is an open-source alternative to Codacy, DeepSource, Checkmarx and Veracode. Other open-source alternatives to Codacy include Semgrep and ESLint.
- Is SonarQube actively maintained?
- Yes. The most recent commit to SonarQube was on 11 November 2026, and the latest release is 26.11.0.134175, published on 4 November 2026. The project has 11k stars on GitHub, with 115 added in the last 30 days.
Open-source alternatives to SonarQube
See all
Semgrep
Security
Lightweight static analysis for many languages. Find bug variants with patterns that look
LGPL-2.1vs Snyk★ 18k
Trivy
Security
Find vulnerabilities, misconfigurations, secrets, SBOM in containers, Kubernetes, code rep
Apache-2.0vs Snyk★ 39k
ESLint
Open source
Find and fix problems in your JavaScript code.
MITvs SonarQube Cloud★ 28k
Horusec
Security
Horusec is an open source tool that improves identification of vulnerabilities in your pro
Apache-2.0vs Checkmarx★ 1.3k
Dependency-Track
Security
Dependency-Track is an intelligent Component Analysis platform that allows organizations t
Apache-2.0vs Snyk★ 4.4k
GitLab Community Edition
CI/CD & DevOps
Open-core GitLab edition you install yourself, with Git hosting, CI/CD and issue tracking
MITvs GitHub★ 25k
SaaS alternatives to SonarQube
See all
Codacy
Developer Tools
Automated code quality and security analysis for pull requests
SaaS
DeepSource
Developer Tools
Static analysis and code health platform with auto-fix suggestions
SaaS
Checkmarx
Security
Application security testing platform with SAST, SCA and API security
SaaS
Veracode
Security
Application security testing platform covering static, dynamic and software composition
SaaS
SonarQube Cloud
Developer Tools
Hosted code quality and security analysis for pull requests, from Sonar
SaaS
Aikido Security
Security
All-in-one application security platform for code, cloud and runtime scanning
SaaS