 TrackMedia
 TrackRev
 Qualys
 Netsparker
About Checkmarx
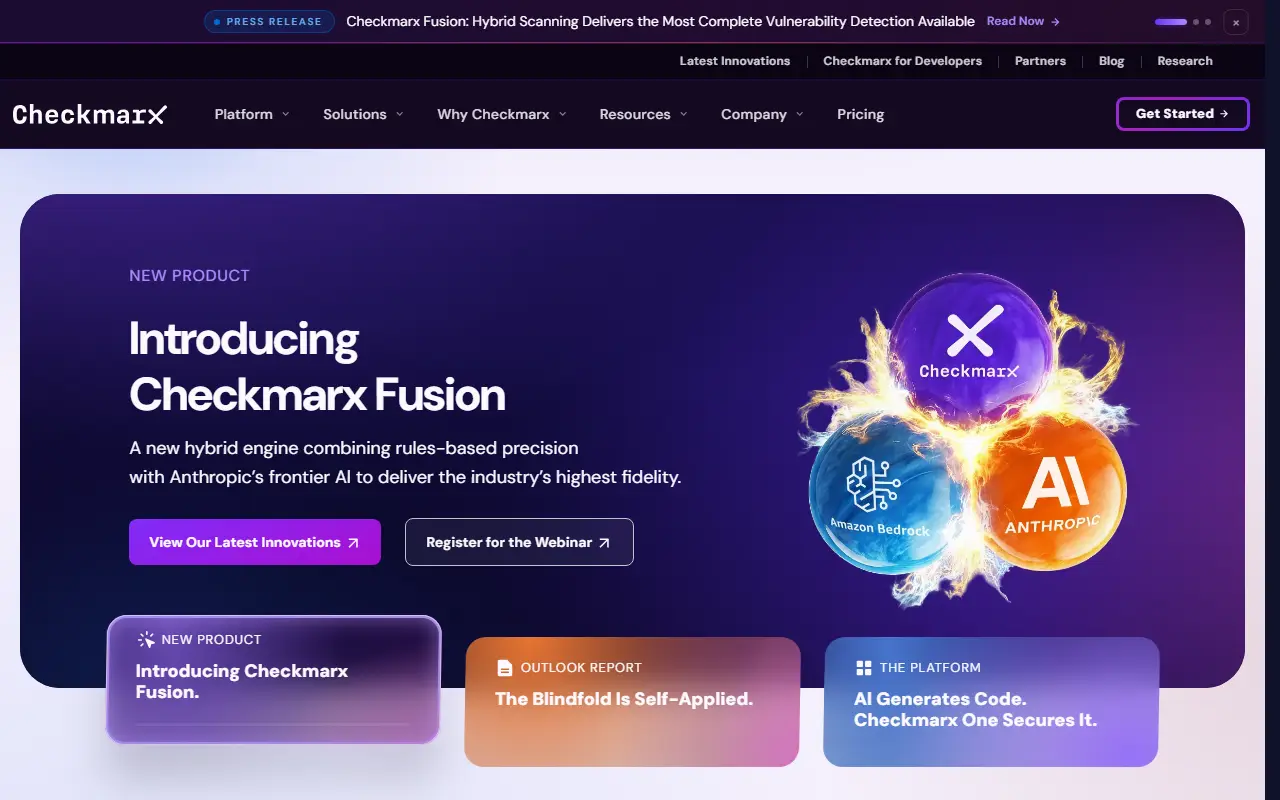
Checkmarx is a commercial application security vendor whose Checkmarx One platform brings multiple testing engines under a single view of risk. It targets organizations in sectors such as financial services, healthcare, insurance and the public sector that need to scan the software they build and the open source they use.
The platform covers code security with static analysis, secrets detection, infrastructure as code scanning and API security, plus supply chain features like software composition analysis, malicious package protection, container security and repository health. Newer pieces address AI supply chain security, an AI bill of materials, LLM scanning and DAST for AI. The hybrid scanning engine Fusion and AI agents for developers and triage sit on top.
Checkmarx is proprietary and delivered as a hosted platform, with an MCP server for connecting AI coding tools. It also publishes a pricing page and offers integrations and partner programs; customers should check the vendor for current packaging.
Key features
- Static application security testing
- Software composition analysis for dependencies
- API security scanning
- Malicious package protection
- AI supply chain and LLM scanning
- AI agents for developer assistance and triage
Good fit for
- Unifying application security tooling
- Securing AI-assisted software development
Checkmarx: questions and answers
- What is Checkmarx used for?
- Checkmarx is an application security testing platform combining SAST, SCA, API security and AI-assisted triage in a unified platform for development and security teams. It is a good fit for unifying application security tooling and securing AI-assisted software development.
- How much does Checkmarx cost?
- Checkmarx doesn't publish fixed prices; pricing is quoted on request.
- Is Checkmarx open source?
- No. Checkmarx is proprietary (closed-source) software. Open-source alternatives to Checkmarx include DefectDojo, Semgrep and Horusec.
- What are some alternatives to Checkmarx?
- Checkmarx competes with Veracode, Snyk and Aikido Security. For open-source options, see Enlisted's ranked list of open-source Checkmarx alternatives.
Open-source alternatives to Checkmarx
See all
DefectDojo
Security
Open-Source Unified Vulnerability Management, DevSecOps & ASPM
BSD-3-Clausevs Tenable★ 5.2k
Semgrep
Security
Lightweight static analysis for many languages. Find bug variants with patterns that look
LGPL-2.1vs Snyk★ 18k
Horusec
Security
Horusec is an open source tool that improves identification of vulnerabilities in your pro
Apache-2.0vs Checkmarx★ 1.3k
Dependency-Track
Security
Dependency-Track is an intelligent Component Analysis platform that allows organizations t
Apache-2.0vs Snyk★ 4.4k
Trivy
Security
Find vulnerabilities, misconfigurations, secrets, SBOM in containers, Kubernetes, code rep
Apache-2.0vs Snyk★ 39k
Nuclei
Security
Nuclei is a fast, customizable vulnerability scanner powered by the global security commun
MITvs Checkmarx★ 33k
SaaS alternatives to Checkmarx
See all
Veracode
Security
Application security testing platform covering static, dynamic and software composition
SaaS
Snyk
Security
Developer security platform that scans code, dependencies, containers and IaC
SaaS
Aikido Security
Security
All-in-one application security platform for code, cloud and runtime scanning
SaaS
Socket
Security
Supply chain security that detects risky open source packages before install
SaaS
Perforce Helix Core
Developer Tools
Centralized version control for large codebases and binary-heavy assets
SaaS
Rapid7
Security
Vulnerability management, SIEM and managed detection tools for security teams
SaaS