 Aikido Security
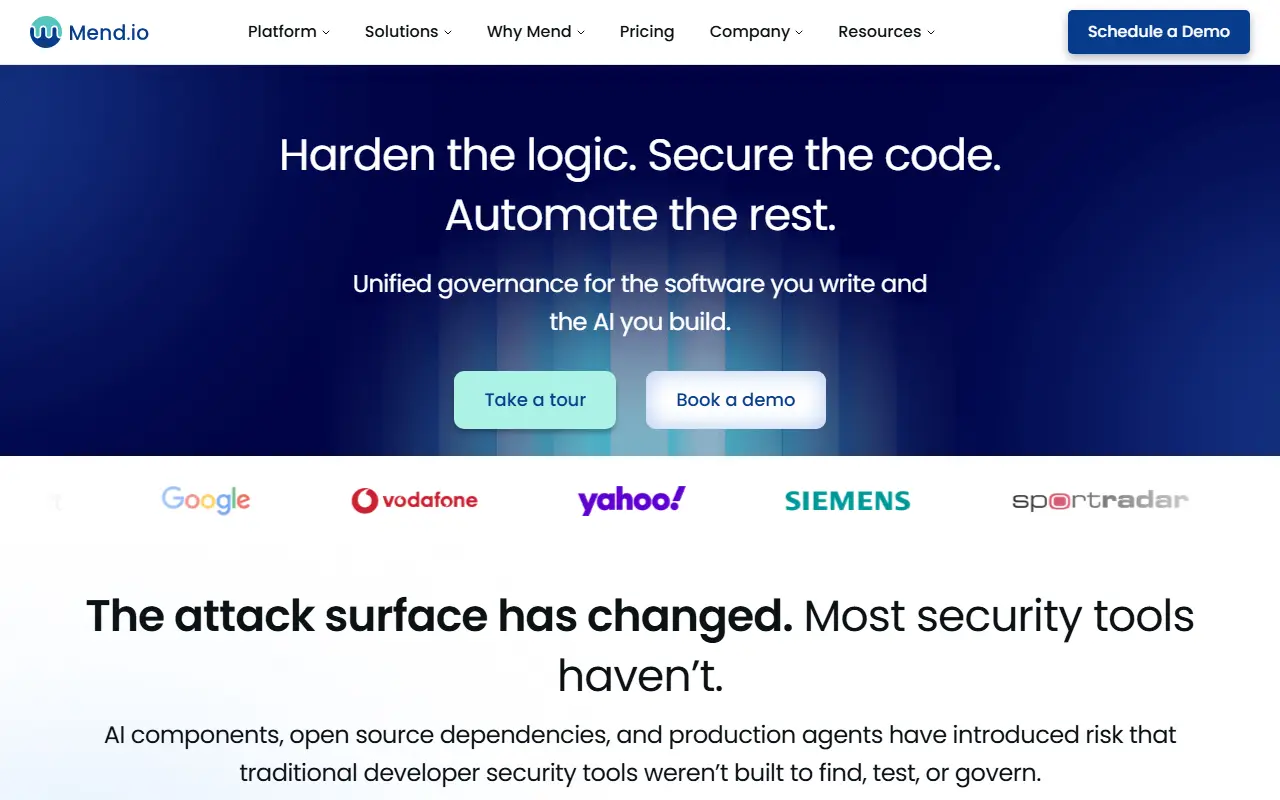
About Mend
Mend, also known as Mend.io, is an application security vendor that combines traditional AppSec tooling with security for AI applications. The goal is to reduce real application risk rather than add noise, using reachability analysis to prioritize vulnerabilities that can actually be exploited.
Mend AppSec includes software composition analysis for open source dependencies and container images, static application security testing, reachability prioritization using EPSS and CVSS scoring, and native integration with GitHub, GitLab, Bitbucket and Azure repositories. Extensions cover dynamic testing, API security and security patches for end-of-life packages. Mend AI adds AI red teaming, runtime guardrails, system prompt hardening and policy governance.
Mend Renovate provides automated dependency updates and is used across a large number of repositories. Mend is a commercial platform with a pricing page and a product tour, and it is meant for development and security teams working together.
Key features
- Software composition analysis for dependencies
- Static application security testing
- Reachability-based vulnerability prioritization
- Automated dependency updates with Renovate
- AI red teaming and runtime guardrails
- Dynamic testing and API security
- Security patches for end-of-life packages
Good fit for
- →Development teams keeping dependencies updated and secure
- →Security teams prioritizing exploitable vulnerabilities
- →Organizations testing conversational AI for jailbreaks
- Tags
- sca
- sast
- application-security
- dependency-management
- renovate
- ai-security
- devsecops
Mend: questions and answers
- What is Mend used for?
- Mend is an application security platform covering software composition analysis, code scanning, dependency updates and AI security. It is a good fit for development teams keeping dependencies updated and secure, security teams prioritizing exploitable vulnerabilities, and organizations testing conversational AI for jailbreaks.
- How much does Mend cost?
- Paid plans for Mend start at $250 per seat per year, and there is no free plan.
- Is Mend open source?
- No. Mend is proprietary (closed-source) software. Open-source alternatives to Mend include Semgrep, Horusec and Dependency-Track.
- What are some alternatives to Mend?
- Mend competes with Snyk, Veracode and Sonatype. For open-source options, see Enlisted's ranked list of open-source Mend alternatives.
Open-source alternatives to Mend
See all
Semgrep
Security
Lightweight static analysis for many languages. Find bug variants with patterns that look
LGPL-2.1vs Snyk★ 17k
Horusec
Security
Horusec is an open source tool that improves identification of vulnerabilities in your pro
Apache-2.0vs Checkmarx★ 1.3k
Dependency-Track
Security
Dependency-Track is an intelligent Component Analysis platform that allows organizations t
Apache-2.0vs Snyk★ 4.3k
Trivy
Security
Find vulnerabilities, misconfigurations, secrets, SBOM in containers, Kubernetes, code rep
Apache-2.0vs Snyk★ 38k
Grype
Security
A vulnerability scanner for container images and filesystems
Apache-2.0vs Snyk★ 13k
SonarQube
Developer Tools
Continuous Inspection
LGPL-3.0vs Codacy★ 11k
SaaS alternatives to Mend
See all
Snyk
Security
Developer security platform that scans code, dependencies, containers and IaC
SaaSVeracode
Security
Application security testing platform covering static, dynamic and software composition
SaaS
Sonatype
Security
Software supply chain security platform with Lifecycle and Firewall products
SaaS
Black Duck
Security
Software composition analysis and application security testing products
SaaS
Checkmarx
Security
Application security testing platform with SAST, SCA and API security
SaaS
Socket
Security
Supply chain security that detects risky open source packages before install
SaaS