 TrackMedia
 TrackRev

About Aikido Security
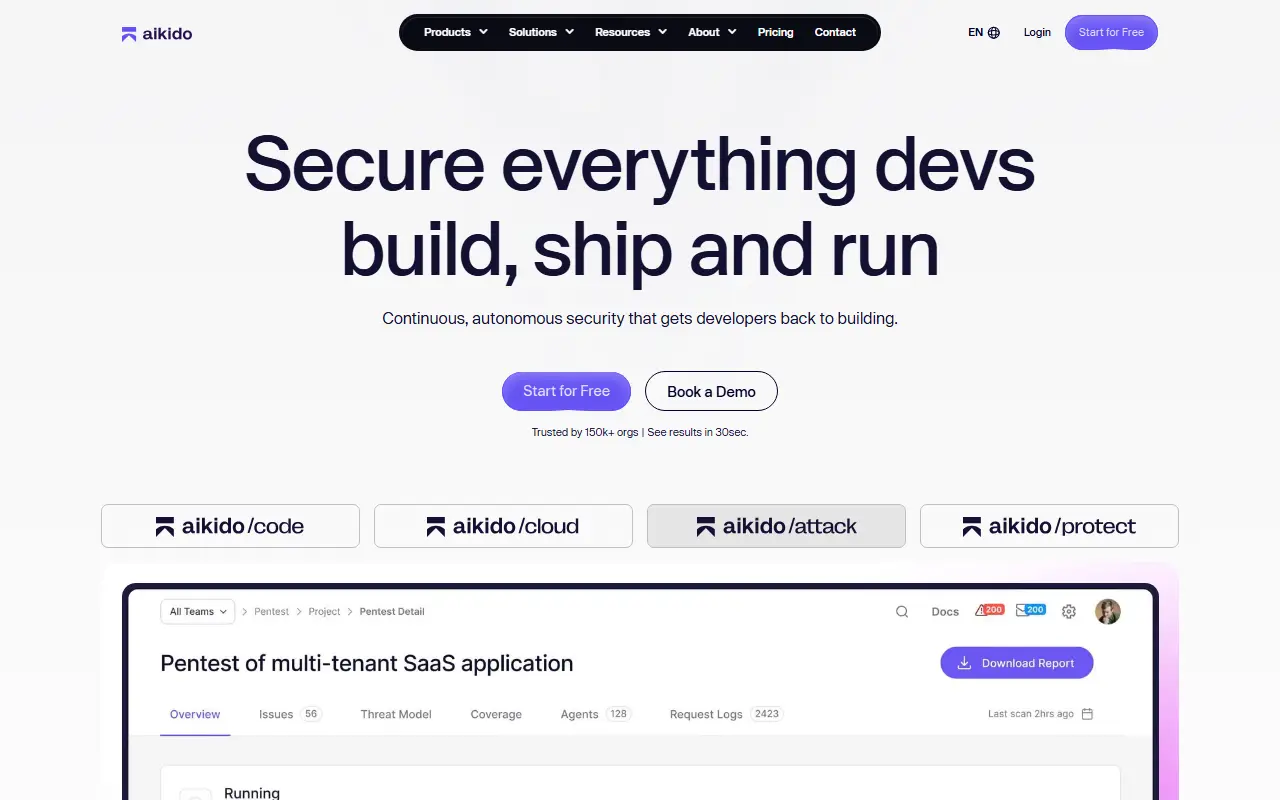
Aikido Security is a commercial application security platform that gathers many scanners behind one interface so that small and growing teams do not need to assemble separate tools. It aims to keep developers focused on building by running continuous, automated checks across code, cloud infrastructure and running applications, and by proposing fixes.
On the code side it covers dependency scanning, supply chain malware detection, static analysis including an AI-based variant, secrets, licenses and SBOMs, outdated software and a pull request reviewer. Cloud tooling includes misconfiguration detection, virtual machine and Kubernetes scanning, container images, data security posture and attack path analysis, while offensive features include DAST, API scanning, attack surface monitoring and continuous pentests. Runtime protection is also offered.
Aikido is proprietary and sold as a hosted subscription with a published pricing page. Its site highlights AI AutoFix, CI/CD and IDE integrations, compliance automation for frameworks such as SOC 2 and ISO, and an on-premises scanning option for teams with stricter requirements.
Key features
- Dependency and supply chain malware scanning
- Static analysis including AI-based SAST
- Cloud misconfiguration and Kubernetes scanning
- Continuous automated pentests
- Runtime protection and bot defense
- AI AutoFix suggestions for vulnerabilities
Good fit for
- Startups building an application security program
- Automating SOC 2 and ISO evidence gathering
Aikido Security: questions and answers
- What is Aikido Security used for?
- Aikido Security is an all-in-one application security platform that combines code scanning, cloud posture checks, pentesting and runtime protection for development teams. It is a good fit for startups building an application security program, and automating SOC 2 and ISO evidence gathering.
- Is Aikido Security free?
- Yes. Aikido Security has a free plan. Free forever Developer plan for 2 users. Paid Basic, Pro and Advanced plans are priced per month for 10 users, and Enterprise and pentests are quoted; currency and billing for the paid tiers are unclear on the page.
- Is Aikido Security open source?
- No. Aikido Security is proprietary (closed-source) software. Open-source alternatives to Aikido Security include Semgrep, Horusec and Gitleaks.
- What are some alternatives to Aikido Security?
- Aikido Security competes with Snyk, Socket and Checkmarx. For open-source options, see Enlisted's ranked list of open-source Aikido Security alternatives.
Open-source alternatives to Aikido Security
See all
Semgrep
Security
Lightweight static analysis for many languages. Find bug variants with patterns that look
LGPL-2.1vs Snyk★ 18k
Horusec
Security
Horusec is an open source tool that improves identification of vulnerabilities in your pro
Apache-2.0vs Checkmarx★ 1.3k
Gitleaks
Security
Find secrets with Gitleaks 🔑
MITvs GitGuardian★ 31k
TruffleHog
Security
Find, verify, and analyze leaked credentials
AGPL-3.0vs GitGuardian★ 29k
Kubescape
Security
Kubescape is an open-source Kubernetes security platform for your IDE, CI/CD pipelines, an
Apache-2.0vs Wiz★ 12k
tfsec
Security
Tfsec is now part of Trivy
MITvs Aikido Security★ 7.1k
SaaS alternatives to Aikido Security
See all
Snyk
Security
Developer security platform that scans code, dependencies, containers and IaC
SaaS
Socket
Security
Supply chain security that detects risky open source packages before install
SaaS
Checkmarx
Security
Application security testing platform with SAST, SCA and API security
SaaS
Wiz
Security
Agentless cloud security platform mapping risk across code, cloud and runtime
SaaS
Veracode
Security
Application security testing platform covering static, dynamic and software composition
SaaS
Mend
Security
Application security platform for software composition analysis and code scanning
SaaS