
About TruffleHog
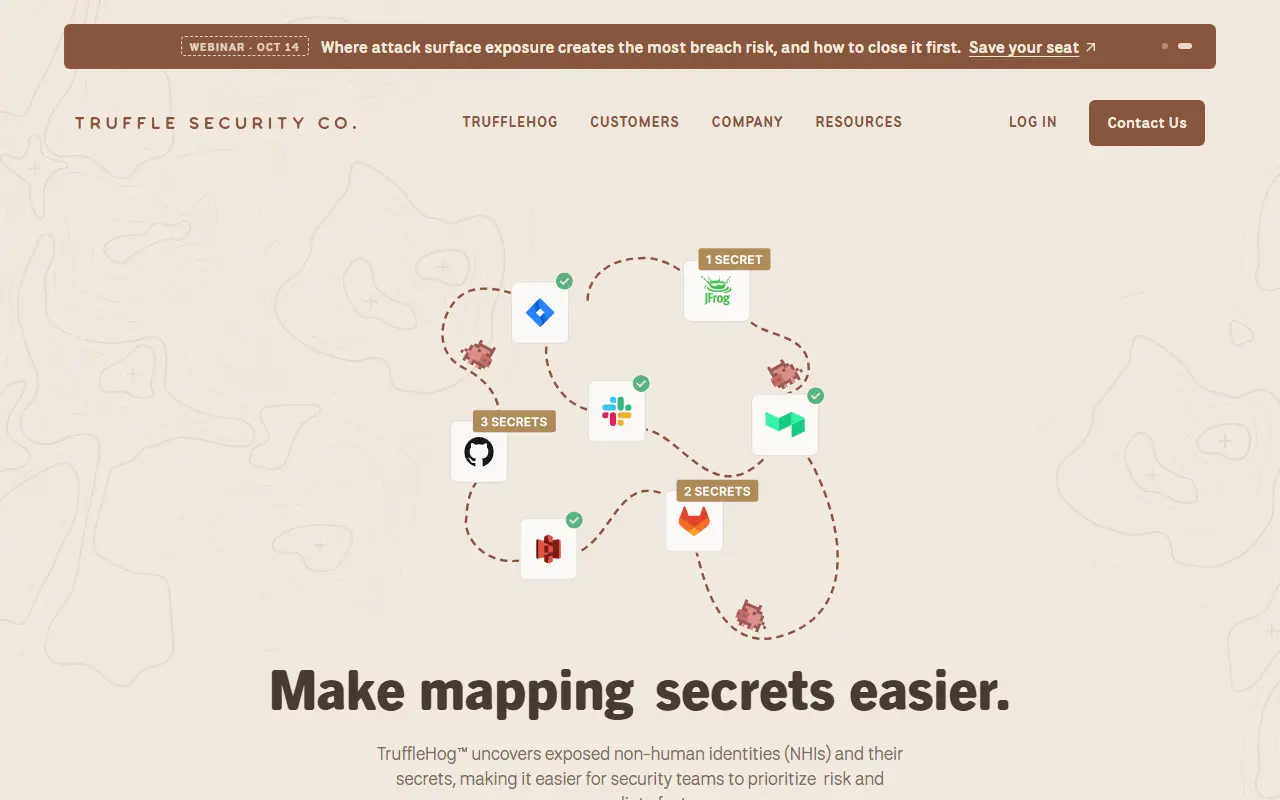
TruffleHog is a tool for discovering, classifying, validating and analyzing secrets, meaning credentials a machine uses to authenticate to another machine, such as API keys, database passwords and private keys. It is written in Go and released under the AGPL-3.0 license. It can be used from the command line and in pre-commit and CI scans as part of DevSecOps work.
Discovery reaches into Git repositories, chat tools, wikis, log files, API testing platforms, object stores and filesystems. Classification identifies more than 800 secret types and maps each to the identity it belongs to. Validation attempts to log in with the found secret to confirm whether it is still live, and analysis for roughly twenty common credential types sends further requests to learn who created the secret and what it can access. Truffle Security also sells an enterprise product that monitors systems such as Git, Jira, Slack and Confluence.
Key features
- Scans Git, chats, wikis, logs and filesystems
- Classifies over 800 secret types
- Validates whether a found secret is live
- Analyzes permissions of common credential types
- Runs from the CLI and in pre-commit checks
- Enterprise monitoring product available separately
Good fit for
- →Finding leaked keys in git history
- →Prioritizing exposed secrets that are still active
- Built with
- Go
- Tags
- secret-scanning
- security
- credentials
- devsecops
- git
- pre-commit
- golang
- verification
TruffleHog: questions and answers
- What is TruffleHog used for?
- TruffleHog finds, classifies and verifies leaked credentials across Git, chats, wikis, logs, filesystems and cloud storage. It is a good fit for finding leaked keys in git history and prioritizing exposed secrets that are still active.
- Is TruffleHog open source?
- Yes. TruffleHog is open source under the AGPL-3.0 licence. Its source code is on GitHub at trufflesecurity/trufflehog and is written mainly in Go.
- Is TruffleHog free?
- Yes. TruffleHog is open source, so the software itself is free to use.
- What is TruffleHog an alternative to?
- TruffleHog is an open-source alternative to GitGuardian and Aikido Security. Other open-source alternatives to GitGuardian include Gitleaks and Trivy.
- Is TruffleHog actively maintained?
- Yes. The most recent commit to TruffleHog was on 2 October 2026, and the latest release is v3.97.9, published on 24 September 2026. The project has 28k stars on GitHub.
Open-source alternatives to TruffleHog
See all
Gitleaks
Security
Find secrets with Gitleaks 🔑
MITvs GitGuardian★ 30k
Trivy
Security
Find vulnerabilities, misconfigurations, secrets, SBOM in containers, Kubernetes, code rep
Apache-2.0vs Snyk★ 38k
Semgrep
Security
Lightweight static analysis for many languages. Find bug variants with patterns that look
LGPL-2.1vs Snyk★ 17k
Grype
Security
A vulnerability scanner for container images and filesystems
Apache-2.0vs Snyk★ 13k
Kubescape
Security
Kubescape is an open-source Kubernetes security platform for your IDE, CI/CD pipelines, an
Apache-2.0vs Wiz★ 12k
Horusec
Security
Horusec is an open source tool that improves identification of vulnerabilities in your pro
Apache-2.0vs Checkmarx★ 1.3k
SaaS alternatives to TruffleHog
See all
GitGuardian
Security
Detects leaked secrets and credentials in code repositories and developer tools
SaaS
Aikido Security
Security
All-in-one application security platform for code, cloud and runtime scanning
SaaS
Snyk
Security
Developer security platform that scans code, dependencies, containers and IaC
SaaS
AuditYourApp
Security
Scans Supabase projects, websites and mobile apps for exposed RLS rules, open RPCs and leaked API keys
SaaSBeesecure
Security
Security scanning platform that finds vulnerabilities in codebases for developers and indie hackers
SaaS
Checkmarx
Security
Application security testing platform with SAST, SCA and API security
SaaS