 TrackMedia
 TrackRev
About Beesecure
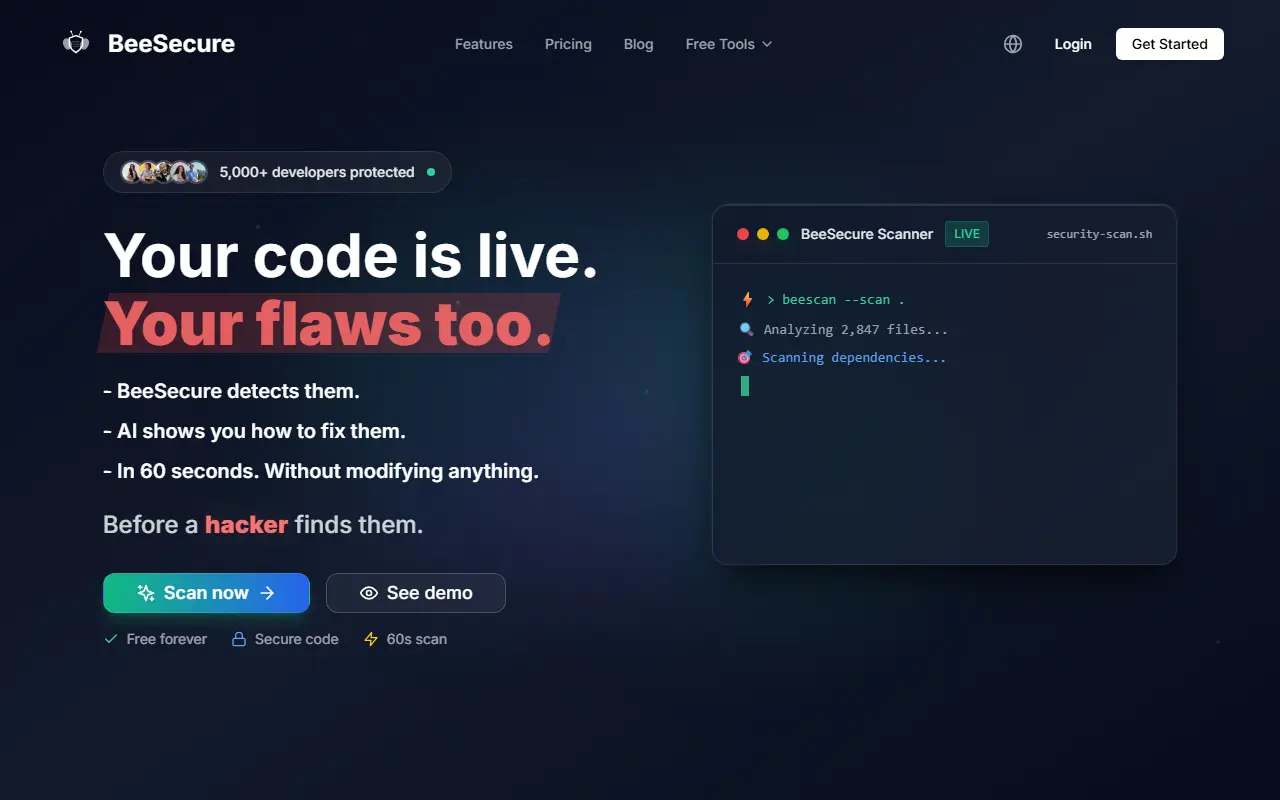
BeeSecure scans a codebase and its dependencies for vulnerabilities and shows how to fix them. You connect a repository through GitHub OAuth2, it detects the stack, and a scan is described as taking about 60 seconds without modifying anything.
The listed process runs through connection, Semgrep, a specialized AI step and a report. There is also a route that needs no code access: paste a URL and get a vulnerability report in 30 seconds. The homepage lists Next.js, Bolt.new, Prisma, Vercel, Supabase and Tailwind as stacks its users work with.
Plans are Free at 0€, Solo at 9€ per month and Startup at 29€ per month, differing in scans, repositories, seats and lines of code covered.
Key features
- Connect a repo and AI suggests fixes
- URL-only report without code access
- Patches, monitoring and alerts
- Solo plan with unlimited scans and multi-branch analysis
- Startup plan adds CI/CD, Slack alerts and roles
Good fit for
- Scanning a GitHub repo for vulnerabilities
- Checking a site by URL
- Adding security checks to CI/CD
Beesecure: questions and answers
- What is Beesecure used for?
- Beesecure is a security scanner that connects to a GitHub repository, flags vulnerabilities, and uses AI to explain fixes without changing your code. It is a good fit for scanning a GitHub repo for vulnerabilities, checking a site by URL and adding security checks to CI/CD.
- Is Beesecure open source?
- No. Beesecure is proprietary (closed-source) software. In the Security category, open-source options include Legitify, Gitleaks and TruffleHog.
- What are some alternatives to Beesecure?
- Beesecure competes with Snyk, Aikido Security and Socket.
Open-source alternatives to Beesecure
See all
Legitify
Security
Detect and remediate misconfigurations and security risks across all your GitHub and GitLa
Apache-2.0★ 896
Gitleaks
Security
Find secrets with Gitleaks 🔑
MITvs GitGuardian★ 31k
TruffleHog
Security
Find, verify, and analyze leaked credentials
AGPL-3.0vs GitGuardian★ 29k
Semgrep
Security
Lightweight static analysis for many languages. Find bug variants with patterns that look
LGPL-2.1vs Snyk★ 18k
DefectDojo
Security
Open-Source Unified Vulnerability Management, DevSecOps & ASPM
BSD-3-Clausevs Tenable★ 5.2k
Kubescape
Security
Kubescape is an open-source Kubernetes security platform for your IDE, CI/CD pipelines, an
Apache-2.0vs Wiz★ 12k
SaaS alternatives to Beesecure
See all
Snyk
Security
Developer security platform that scans code, dependencies, containers and IaC
SaaS
Aikido Security
Security
All-in-one application security platform for code, cloud and runtime scanning
SaaS
Socket
Security
Supply chain security that detects risky open source packages before install
SaaS
GitGuardian
Security
Detects leaked secrets and credentials in code repositories and developer tools
SaaS
Mend
Security
Application security platform for software composition analysis and code scanning
SaaS
Checkmarx
Security
Application security testing platform with SAST, SCA and API security
SaaS