SonarQube
Static code analysis platform that finds bugs, vulnerabilities and maintainability problems in code, in IDEs, pull requests and CI.
- GitHub stars
- 11k
- Last commit
- yesterday
- Latest release
- 26.9.0.129388
- Licence
- LGPL-3.0
- Self-hosted
- Yes
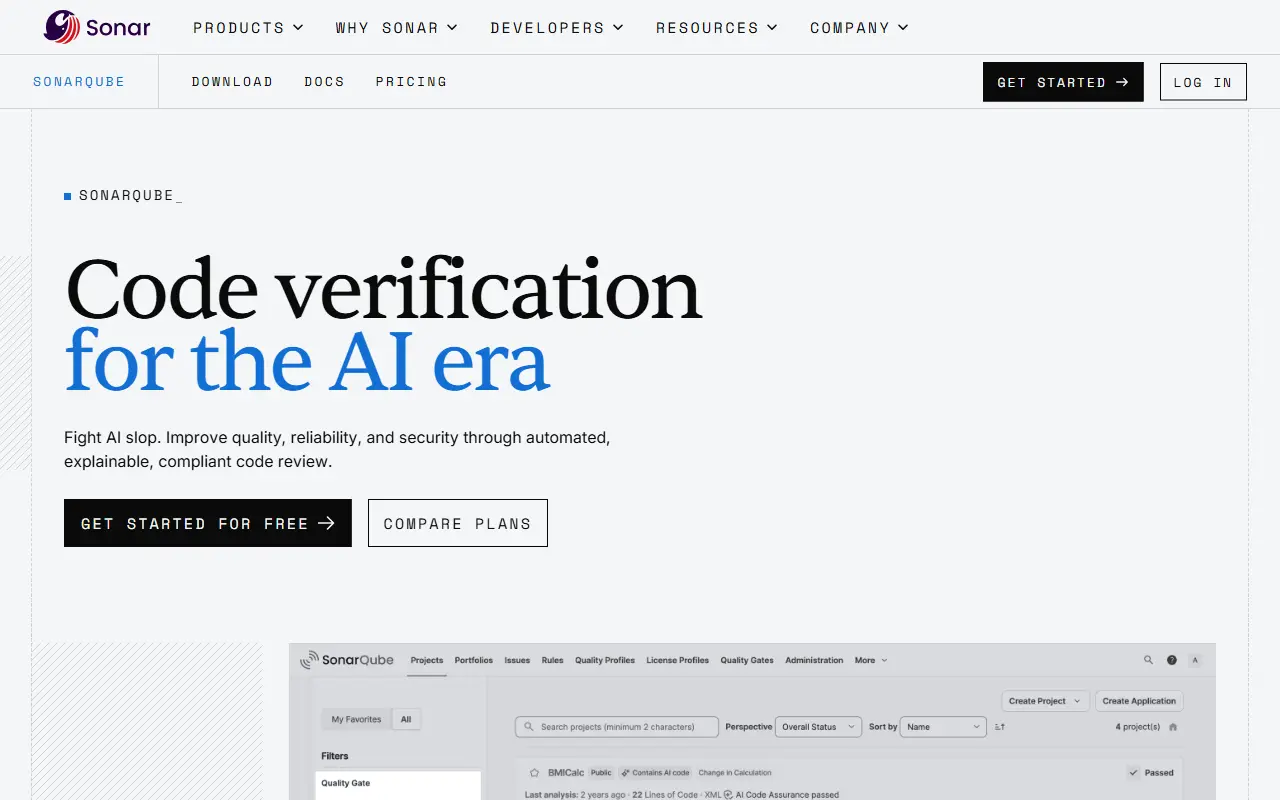
SonarQube is a code quality and security platform. Its static analysis uses techniques such as symbolic execution and data and control flow analysis to inspect source code, find bugs and vulnerabilities, and explain what to fix and why. Results appear in the IDE, in pull requests and in CI pipelines.
This repository holds the source of the SonarQube Community Build, the free, open-source edition that shares the analysis used across the product line. It reports reliability bugs, security vulnerabilities and security hotspots, maintainability and structural issues, and coverage on new code. More than 40 programming languages and frameworks are covered, and the same code always produces the same findings.
The project positions itself as a verification step for code written by people or by AI agents before it merges. SonarQube is written in Java and licensed under LGPL-3.0. Commercial editions from SonarSource add further features, while the Community Build can be run on your own servers.
Key features
- Static analysis for bugs and vulnerabilities
- Security hotspot review guidance
- Maintainability and structural issue detection
- Coverage tracking on new code
- Support for 40+ languages and frameworks
- Feedback in IDE, pull requests and CI
Pricing: A free tier covers private projects up to 50k lines of code and an open-source Community Build is available. The Team plan starts at $34 a month for up to 100k lines of code; Enterprise is quoted.





