 TrackMedia
 TrackRev
 Polyrouter
About Qodana
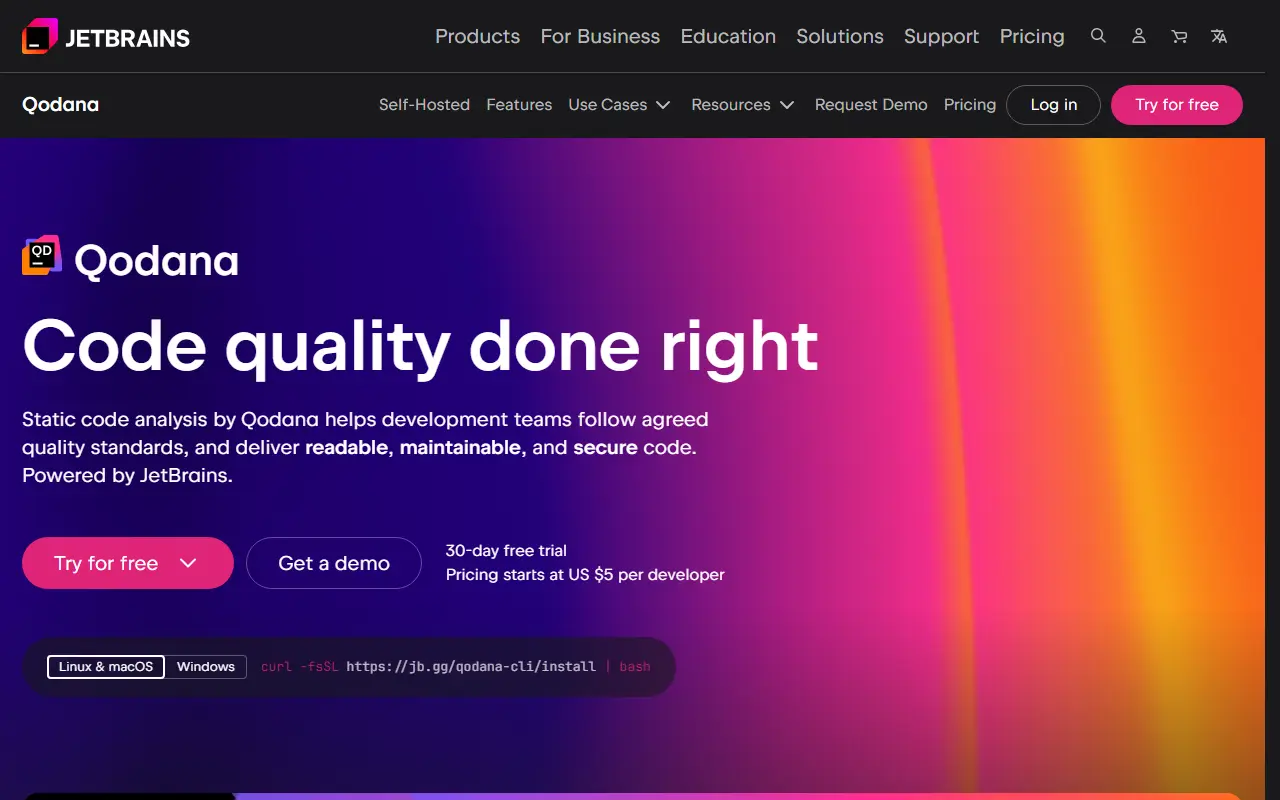
Qodana is a static code analysis product from JetBrains. It takes the inspections that JetBrains has built into its IDEs and runs them on the CI side, so a team can hold to agreed quality standards and catch problems before they reach production, using the same engine in the editor and in the pipeline.
It reports performance issues, probable bugs, unused declarations, naming and style violations and security problems in dependencies, and it can propose quick-fixes, including by opening pull requests with the fix applied. A baseline lets a team accept existing issues and only block new ones, so older code does not stall adoption.
Further checks cover third-party license compatibility and code coverage, with quality gates that can fail a build when coverage falls under a chosen percentage. Pricing is per active contributor rather than per line of code. A 30-day free trial is offered, and open-source projects use it free.
Key features
- More than 2,500 code inspections
- Third-party license compatibility audit
- Vulnerable dependency and API detection
- Coverage reporting with quality gates
- Baseline for existing technical debt
- Automatic pull requests with quick-fixes
Good fit for
- CI quality gates
- Dependency vulnerability checks
- License compliance audits
- Gradual cleanup of legacy code
Qodana: questions and answers
- What is Qodana used for?
- Qodana is a JetBrains static code analysis for CI pipelines, built on the inspections of its IDEs, with quality gates, license audit and coverage. It is a good fit for CI quality gates, dependency vulnerability checks and license compliance audits.
- Is Qodana free?
- Yes. Qodana has a free plan. Pricing starts at US $5 per developer, with a 30-day free trial. Taxes may be added, and prices shown are approximate.
- Is Qodana open source?
- No. Qodana is proprietary (closed-source) software. Open-source alternatives to Qodana include SonarQube, ESLint and Semgrep.
- What are some alternatives to Qodana?
- Qodana competes with SonarQube Cloud, Codacy and DeepSource. For open-source options, see Enlisted's ranked list of open-source Qodana alternatives.
Open-source alternatives to Qodana
See all
SonarQube
Developer Tools
Continuous Inspection
LGPL-3.0vs Codacy★ 11k
ESLint
Open source
Find and fix problems in your JavaScript code.
MITvs SonarQube Cloud★ 28k
Semgrep
Security
Lightweight static analysis for many languages. Find bug variants with patterns that look
LGPL-2.1vs Snyk★ 18k
golangci-lint
Developer Tools
Fast linters runner for Go
GPL-3.0vs SonarQube Cloud★ 20k
Revive
Developer Tools
🔥 Fast, strict, configurable, extensible, and beautiful linter for Go
MITvs DeepSource★ 5.6k
Tach
Developer Tools
A Python tool to visualize + enforce dependencies, using modular architecture 🌎 Open sour
MIT★ 2.9k
SaaS alternatives to Qodana
See all
SonarQube Cloud
Developer Tools
Hosted code quality and security analysis for pull requests, from Sonar
SaaS
Codacy
Developer Tools
Automated code quality and security analysis for pull requests
SaaS
DeepSource
Developer Tools
Static analysis and code health platform with auto-fix suggestions
SaaS
Code Climate
Developer Tools
Automated code review and engineering analytics tools
SaaS
CodeScene
Developer Tools
Code analysis tool that finds technical debt and code health risks from version history
SaaS
Snyk
Security
Developer security platform that scans code, dependencies, containers and IaC
SaaS