4 open-source alternatives ranked by real activity

Open-source CodeScene alternatives

A curated, ranked list of the 4 best open-source alternatives to CodeScene.

The best open-source alternative to CodeScene is Semgrep. If that doesn't suit you, other good options are ESLint, SonarQube and Reviewboard.

Commercial alternatives to CodeScene include Code Climate, Qodana, SonarQube Cloud and Codacy. See all 19.

CodeScene alternatives are mainly developer tools, but some are also security tools. 4 of them shipped code in the last 30 days, 4 can be self-hosted, and 2 use a permissive licence.

Last updated November 12, 2026 · ranked by GitHub stars, growth and recent commits

Semgrep

Semgrep is a fast, open-source static analysis tool that finds bugs and enforces security and coding standards across 30+ languages.

GitHub stars
18k
Last commit
2 days ago
Latest release
v1.185.0
Licence
LGPL-2.1
Self-hosted
Yes
Hosted version
Available
semgrep.devSemgrep homepage screenshot

Semgrep is a lightweight static analysis tool that searches code, finds bugs and enforces secure guardrails and coding standards. It supports more than 30 languages and can run in an IDE, as a pre-commit check or inside CI/CD workflows. The core engine is released under the LGPL-2.1 license.

It works like a semantic grep for code. Rules are written to look like the source code developers already write, so matching a pattern does not require abstract syntax trees, regular expressions or a separate query language, and a search for a value can match code that computes it. The aim is to find variants of a known bug quickly.

The Community Edition analyzes code within a single function or file, which the maintainers note means it will miss many true positives for security work. For SAST, software composition analysis and secrets scanning they recommend the commercial Semgrep AppSec Platform, which adds cross-file and data-flow analysis, AI-assisted triage and managed rule sets.

Key features

  • Pattern-based code search that looks like code
  • Support for 30+ programming languages
  • Runs in IDEs, pre-commit hooks and CI/CD
  • Custom rules without ASTs or regex
  • SAST, SCA and secrets scanning via AppSec Platform

Pricing: Free for up to 10 contributors. Teams starts at $30 per contributor per month (Secrets $15); Enterprise is custom.
Read more about SemgrepWebsiteGitHub#1 CodeScene alternative

ESLint

ESLint is an open source linter for JavaScript and JSX that finds problems in code and can fix many of them automatically.

GitHub stars
28k
Last commit
yesterday
Latest release
v10.14.0
Licence
MIT
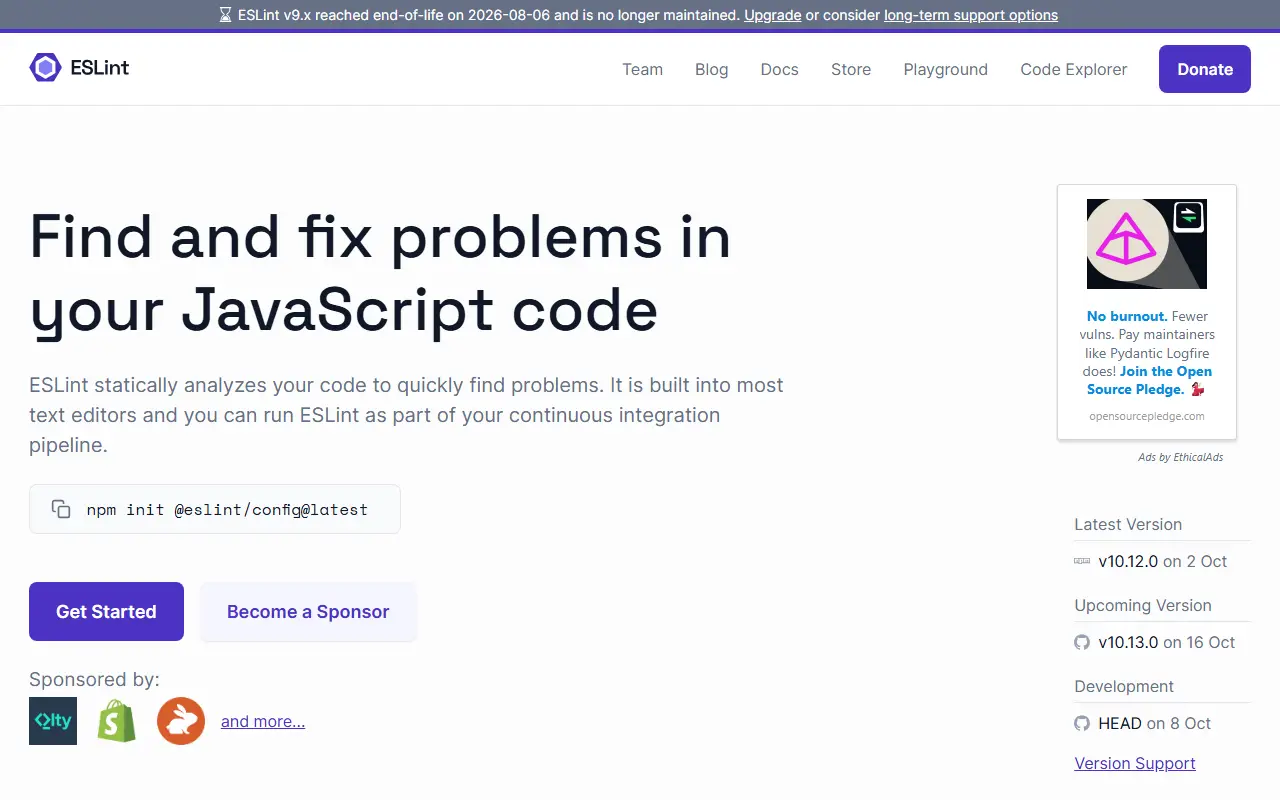
eslint.orgESLint homepage screenshot

ESLint is an open source linting utility for JavaScript and JSX. It reads your code without running it, reports problems, and works for code written for the browser or the server, with or without a framework.

Many of the problems it reports can be fixed automatically, and the fixes take the syntax into account rather than doing plain find-and-replace. It is built into most text editors, and you can also run it as a step in a continuous integration pipeline.

Behaviour is configurable. You can preprocess code, plug in custom parsers and write your own rules next to the built-in ones. The project is MIT-licensed and funded through sponsors and donations; the site also lists a playground, a code explorer and a blog with release notes.

Key features

  • Static analysis that finds problems in JavaScript
  • Runs inside a continuous integration pipeline
  • Syntax-aware automatic fixes
  • Custom parsers, preprocessing and your own rules
  • Works for browser and server code, with or without a framework
Read more about ESLintWebsiteGitHub#2 CodeScene alternative

SonarQube

Static code analysis platform that finds bugs, vulnerabilities and maintainability problems in code, in IDEs, pull requests and CI.

GitHub stars
11k
Last commit
yesterday
Latest release
26.11.0.134175
Licence
LGPL-3.0
Self-hosted
Yes
sonarqube.orgSonarQube homepage screenshot

SonarQube is a code quality and security platform. Its static analysis uses techniques such as symbolic execution and data and control flow analysis to inspect source code, find bugs and vulnerabilities, and explain what to fix and why. Results appear in the IDE, in pull requests and in CI pipelines.

This repository holds the source of the SonarQube Community Build, the free, open-source edition that shares the analysis used across the product line. It reports reliability bugs, security vulnerabilities and security hotspots, maintainability and structural issues, and coverage on new code. More than 40 programming languages and frameworks are covered, and the same code always produces the same findings.

The project positions itself as a verification step for code written by people or by AI agents before it merges. SonarQube is written in Java and licensed under LGPL-3.0. Commercial editions from SonarSource add further features, while the Community Build can be run on your own servers.

Key features

  • Static analysis for bugs and vulnerabilities
  • Security hotspot review guidance
  • Maintainability and structural issue detection
  • Coverage tracking on new code
  • Support for 40+ languages and frameworks
  • Feedback in IDE, pull requests and CI

Pricing: A free tier covers private projects up to 50k lines of code and an open-source Community Build is available. The Team plan starts at $34 a month for up to 100k lines of code; Enterprise is quoted.

Reviewboard

Review Board is a code review, image review, and document review tool that supports on-prem and cloud hosting.

GitHub stars
1.7k
Last commit
yesterday
Latest release
release-8.0
Licence
MIT
Self-hosted
Yes
Hosted version
Available
reviewboard.orgReviewboard homepage screenshot

Review Board is a code review, image review, and document review tool for teams. It supports Git, Jujutsu, Perforce, Subversion, Mercurial, ClearCase, Azure DevOps, CVS, and Breezy. The tool offers flexible workflows, approval control, and an audit trail of every review and decision.

Review Board can be deployed on-premises or used as a cloud-hosted service. It provides installers and Docker containers for on-prem setup. The tool also offers enterprise integrations, reports, and enhanced document review through a Power Pack add-on.

Key features

  • Code review, image review, and document review
  • Flexible workflows and approval control
  • Automation-ready with automated reviews, CI jobs, webhooks, and extensions
  • Full audit trail of every review and decision
  • Supports Git, Jujutsu, Perforce, Subversion, Mercurial, ClearCase, Azure DevOps, CVS, and Breezy
  • On-prem and cloud hosting options

Commercial CodeScene alternatives

Hosted, closed-source products that compete with CodeScene. Showing 12 of 19.

See every CodeScene alternative on its tool page

CodeScene alternatives: questions

What is the best open-source alternative to CodeScene?
Semgrep is the top-ranked open-source alternative to CodeScene on Enlisted: Semgrep is a fast, open-source static analysis tool that finds bugs and enforces security and coding standards across 30+ languages. Other strong options are ESLint, SonarQube and Reviewboard.
What are the best commercial alternatives to CodeScene?
Code Climate, Qodana, SonarQube Cloud, Codacy and Debtdrone are among the hosted, closed-source alternatives to CodeScene listed on Enlisted, which lists 19 in total. Compare their pricing and features on each tool page.
Are these CodeScene alternatives free?
All 4 are open source, so the code is free to use under its licence, and all of them can be self-hosted on your own server or computer. 2 also offer a paid or managed cloud version if you'd rather not host it yourself.
How is this list of CodeScene alternatives ranked?
By a score built from GitHub stars, star growth over the last 30 days and how recently the code changed. 4 of these projects shipped code in the last 30 days. Data is refreshed daily, and nobody can pay to move up.

People also look for alternatives to…

View all