Semgrep
Semgrep is a fast, open-source static analysis tool that finds bugs and enforces security and coding standards across 30+ languages.
- GitHub stars
- 17k
- Last commit
- yesterday
- Latest release
- v1.179.0
- Licence
- LGPL-2.1
- Self-hosted
- Yes
- Hosted version
- Available
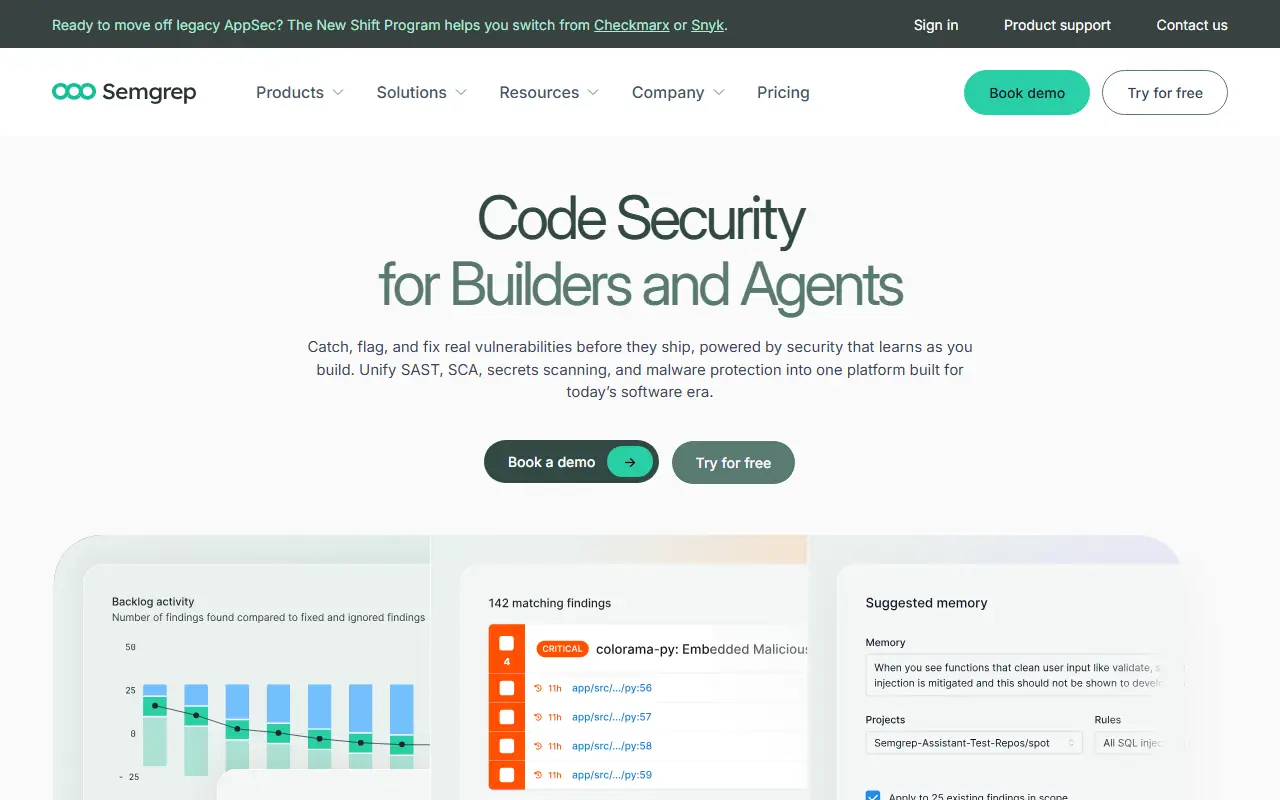
Semgrep is a lightweight static analysis tool that searches code, finds bugs and enforces secure guardrails and coding standards. It supports more than 30 languages and can run in an IDE, as a pre-commit check or inside CI/CD workflows. The core engine is released under the LGPL-2.1 license.
It works like a semantic grep for code. Rules are written to look like the source code developers already write, so matching a pattern does not require abstract syntax trees, regular expressions or a separate query language, and a search for a value can match code that computes it. The aim is to find variants of a known bug quickly.
The Community Edition analyzes code within a single function or file, which the maintainers note means it will miss many true positives for security work. For SAST, software composition analysis and secrets scanning they recommend the commercial Semgrep AppSec Platform, which adds cross-file and data-flow analysis, AI-assisted triage and managed rule sets.
Key features
- Pattern-based code search that looks like code
- Support for 30+ programming languages
- Runs in IDEs, pre-commit hooks and CI/CD
- Custom rules without ASTs or regex
- SAST, SCA and secrets scanning via AppSec Platform
Pricing: Free for up to 10 contributors. Teams starts at $30 per contributor per month (Secrets $15); Enterprise is custom.