
 ESET
 Sophos
 Trend Micro
 Tenable
 Qualys
 Arctic Wolf
 Huntress
 Trellix
 Microsoft Sentinel
 IBM QRadar
 Exabeam
 Google Security Operations
 Tanium
 Amazon GuardDuty
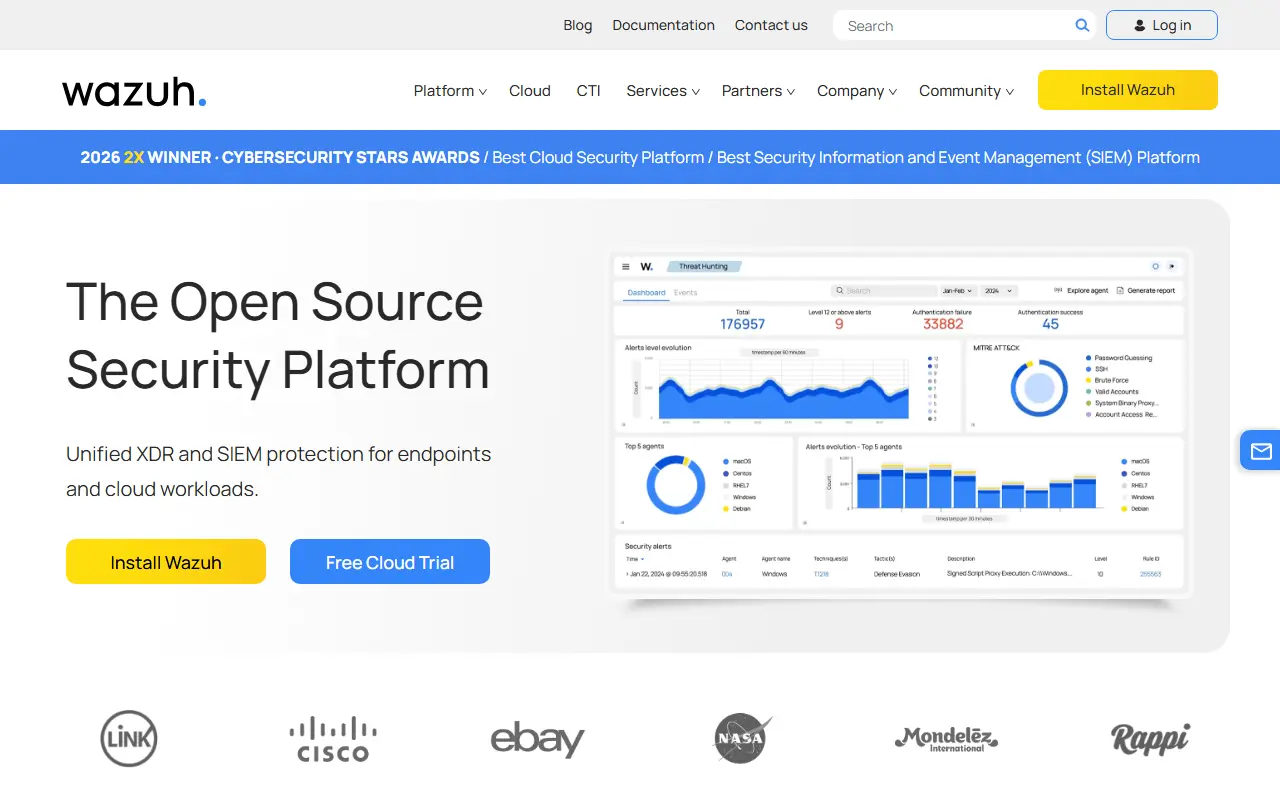
About Wazuh
Wazuh is a free and open-source platform for threat prevention, detection and response. It protects workloads across on-premises, virtualized, containerized and cloud environments and combines XDR and SIEM functions in one product. The code is written mainly in C++.
The solution consists of an endpoint security agent installed on monitored systems and a management server that collects and analyzes the agents' data. It is integrated with the Wazuh Indexer, which offers a search engine and visualization for navigating security alerts. Agents scan for malware, rootkits and suspicious anomalies, read system and application logs, and monitor files for changes to content, permissions, ownership and attributes.
Rule-based analysis of collected logs, including data received from network devices through syslog, helps surface misconfigurations, policy violations and attempted or successful attacks. Repository topics also cover vulnerability detection, configuration assessment, incident response and compliance such as PCI DSS. The repository lists its license as 'Other', so review the license files for the exact terms.
Key features
- Endpoint agents with a central management server
- Intrusion and malware detection
- Log data analysis with rule-based alerts
- File integrity monitoring
- Vulnerability detection and configuration assessment
- Cloud and container workload coverage
Good fit for
- →Security monitoring across servers and endpoints
- →Supporting compliance audits such as PCI DSS
- Built with
- C++
- Tags
- siem
- xdr
- security
- intrusion-detection
- log-analysis
- compliance
- file-integrity-monitoring
- incident-response
Wazuh: questions and answers
- What is Wazuh used for?
- Wazuh is a free, open-source security platform combining XDR and SIEM capabilities for endpoints, servers and cloud workloads. It is a good fit for security monitoring across servers and endpoints, and supporting compliance audits such as PCI DSS.
- Is Wazuh open source?
- Yes. Wazuh is open source under a custom licence. Its source code is on GitHub at wazuh/wazuh and is written mainly in C++.
- Is Wazuh free?
- Yes. Wazuh is open source, so the software itself is free to use under the terms of its own licence.
- Can I self-host Wazuh?
- Yes. Wazuh can be self-hosted on your own server or infrastructure.
- What is Wazuh an alternative to?
- Wazuh is an open-source alternative to Splunk, CrowdStrike, SentinelOne and Rapid7. Other open-source alternatives to Splunk include Security Onion and Graylog.
- Is Wazuh actively maintained?
- Yes. The most recent commit to Wazuh was on 2 October 2026, and the latest release is v4.14.8, published on 25 September 2026. The project has 17k stars on GitHub.
Open-source alternatives to Wazuh
See all
Security Onion
Security
Security Onion is a free and open platform for threat hunting, enterprise security monitor
OSSvs Splunk★ 4.9k
OSSEC
Security
OSSEC is an Open Source Host-based Intrusion Detection System that performs log analysis,
GPL-2.0vs CrowdStrike★ 5.1k
ClamAV
Security
ClamAV - Documentation is here: https://docs.clamav.net
GPL-2.0vs Avast★ 7.3k
Graylog
Monitoring & Observability
Free and open log management
OSSvs Splunk★ 8.2k
Falco
Security
Cloud Native Runtime Security
Apache-2.0vs Wiz★ 9.4k
DefectDojo
Security
Open-Source Unified Vulnerability Management, DevSecOps & ASPM
BSD-3-Clausevs Tenable★ 5k
SaaS alternatives to Wazuh
See all
Splunk
Monitoring & Observability
Splunk is a data platform for security and observability that collects, searches and analyzes machine data to detect threats and prevent downtime.
SaaS
CrowdStrike
Security
Cloud-native endpoint protection, threat detection and response platform
SaaS
SentinelOne
Security
AI-driven endpoint, cloud and identity security platform with automated response
SaaSRapid7
Security
Vulnerability management, SIEM and managed detection tools for security teams
SaaS
Microsoft Defender
Security
Microsoft endpoint, identity and cloud threat protection suite
SaaS
Bitdefender
Security
Antivirus and endpoint protection for consumers and businesses
SaaS