 Aqua Security
 Sysdig
 Prisma Cloud
 Amazon GuardDuty
About Falco
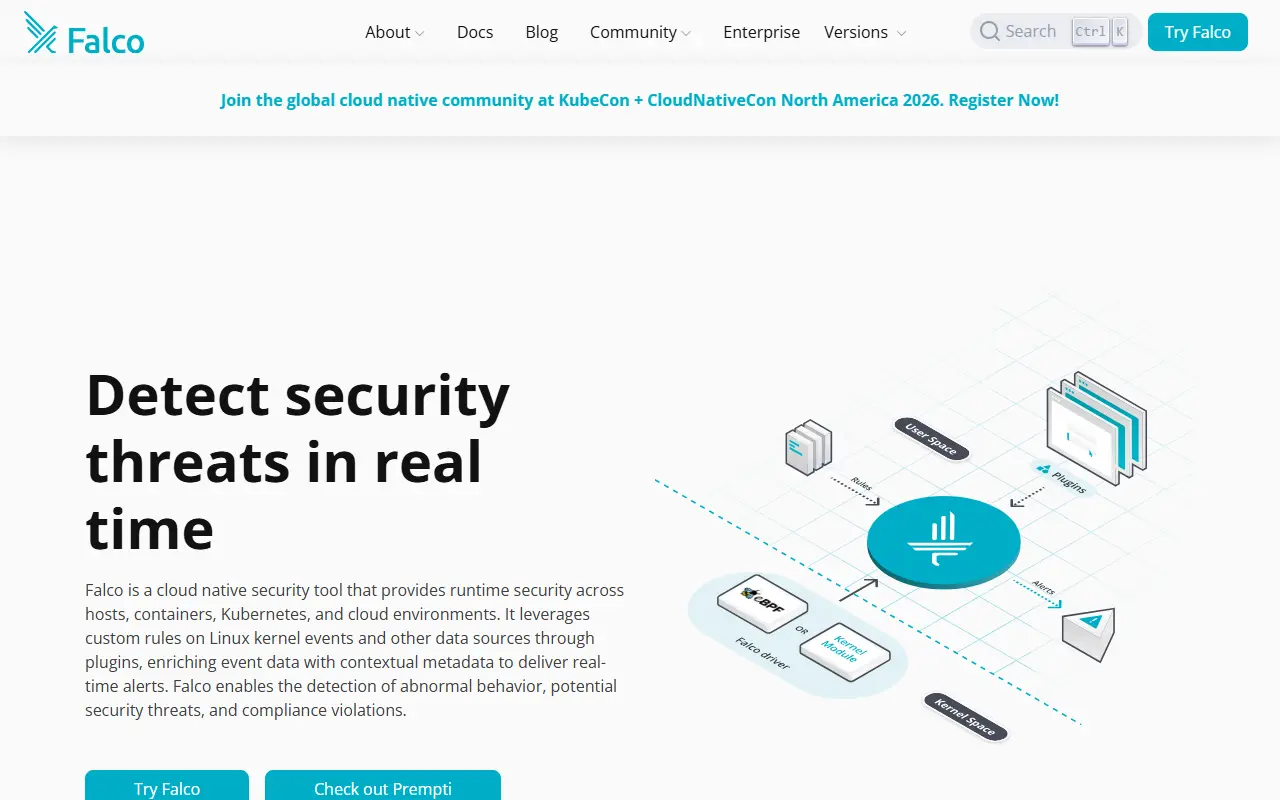
Falco is a cloud native runtime security tool for Linux. It detects and alerts on abnormal behavior and potential security threats in real time. At its core it is a kernel monitoring and detection agent that watches events such as system calls and evaluates them against custom rules.
Falco can enrich events with metadata from the container runtime and from Kubernetes, and the collected events can be analyzed off-host in SIEM or data lake systems. The project is split across repositories in the falcosecurity organization: the main repo holds the Falco binary, while others hold the core libraries and kernel drivers, the official ruleset, and plugins that extend detection beyond syscalls and container events.
Falco was originally created by Sysdig and is a graduated project of the Cloud Native Computing Foundation, used in production by various organizations. It is written in C++ and released under the Apache-2.0 license, with a change log and detailed documentation on falco.org. Topics in the repository mention eBPF-based collection.
Key features
- Kernel-level syscall monitoring
- Custom detection rules
- Container and Kubernetes metadata enrichment
- Official ruleset for common threats
- Plugins for additional event sources
- Export to SIEM or data lake systems
Good fit for
- →Detecting suspicious container behavior
- →Runtime threat alerts for Kubernetes clusters
- Tags
- runtime-security
- kubernetes
- containers
- ebpf
- cncf
- threat-detection
- linux
- cloud-native
Falco: questions and answers
- What is Falco used for?
- Falco is a cloud native runtime security tool that monitors Linux kernel events and alerts on abnormal behavior and threats in real time. It is a good fit for detecting suspicious container behavior and runtime threat alerts for Kubernetes clusters.
- Is Falco open source?
- Yes. Falco is open source under the Apache-2.0 licence. Its source code is on GitHub at falcosecurity/falco and is written mainly in C++.
- Is Falco free?
- Yes. Falco is open source, so the software itself is free to use.
- Can I self-host Falco?
- Yes. Falco can be self-hosted on your own server or infrastructure; there is no official hosted version.
- What is Falco an alternative to?
- Falco is an open-source alternative to Wiz, CrowdStrike, Palo Alto Networks and SentinelOne. Other open-source alternatives to Wiz include Kubescape, Trivy and Grype.
- Is Falco actively maintained?
- Yes. The most recent commit to Falco was on 30 September 2026, and the latest release is 0.45.0, published on 21 September 2026. The project has 9.4k stars on GitHub.
Open-source alternatives to Falco
See all
Kubescape
Security
Kubescape is an open-source Kubernetes security platform for your IDE, CI/CD pipelines, an
Apache-2.0vs Wiz★ 12k
Trivy
Security
Find vulnerabilities, misconfigurations, secrets, SBOM in containers, Kubernetes, code rep
Apache-2.0vs Snyk★ 38k
Grype
Security
A vulnerability scanner for container images and filesystems
Apache-2.0vs Snyk★ 13k
Wazuh
Security
Wazuh - The Open Source Security Platform. Unified XDR and SIEM protection for endpoints a
OSSvs Splunk★ 17k
tfsec
Security
Tfsec is now part of Trivy
MITvs Aikido Security★ 7k
OSSEC
Security
OSSEC is an Open Source Host-based Intrusion Detection System that performs log analysis,
GPL-2.0vs CrowdStrike★ 5.1k
SaaS alternatives to Falco
See allWiz
Security
Agentless cloud security platform mapping risk across code, cloud and runtime
SaaS
CrowdStrike
Security
Cloud-native endpoint protection, threat detection and response platform
SaaS
Palo Alto Networks
Security
Network, cloud and endpoint security vendor selling firewalls, SASE and SOC tools
SaaS
SentinelOne
Security
AI-driven endpoint, cloud and identity security platform with automated response
SaaS
Trend Micro
Security
Cybersecurity vendor for endpoint, cloud workload and email security
SaaS
Aikido Security
Security
All-in-one application security platform for code, cloud and runtime scanning
SaaS