9 open-source alternatives ranked by real activity

Open-source Prisma Cloud alternatives

A curated, ranked list of the 9 best open-source alternatives to Prisma Cloud.

The best open-source alternative to Prisma Cloud is Trivy. If that doesn't suit you, other good options are Prowler, Falco, Kubescape and Checkov.

Commercial alternatives to Prisma Cloud include Sysdig, Orca Security, Aqua Security and Amazon GuardDuty. See all 18.

Prisma Cloud alternatives are mainly security tools, but some are also infrastructure & container tools. 8 of them shipped code in the last 30 days, 9 can be self-hosted, and 7 use a permissive licence.

Last updated November 13, 2026 · ranked by GitHub stars, growth and recent commits

Trivy

A security scanner that finds vulnerabilities, misconfigurations, secrets and license issues in container images, filesystems, Git repositories and Kubernetes.

GitHub stars
39k
Last commit
yesterday
Latest release
v0.76.2
Licence
Apache-2.0
trivy.devTrivy homepage screenshot

Trivy is a security scanner from Aquasec, written in Go and released under the Apache-2.0 license. It has scanners that look for different security issues and targets where those issues can be found. The README describes it as comprehensive and versatile, and it covers the major programming languages, operating systems and platforms.

Targets include container images, filesystems, remote Git repositories, virtual machine images and Kubernetes. Scanners look for OS packages and software dependencies in use, which produces an SBOM, known vulnerabilities (CVEs), infrastructure-as-code issues and misconfigurations, sensitive information and secrets, and software licenses. Its topics reference DevSecOps and vulnerability scanning.

Trivy is available through most common channels, including Homebrew, a Docker image and downloadable binaries, and integrates with platforms such as GitHub Actions, a Kubernetes operator and a VS Code plugin. Canary builds are produced with each push to the main branch. It suits developers, platform teams and security engineers who want to scan images and code in CI pipelines.

Key features

  • Scans container images and filesystems
  • Scans Git repositories and Kubernetes
  • Known vulnerability (CVE) detection
  • IaC misconfiguration and secret detection
  • SBOM generation and license scanning
  • GitHub Actions and VS Code integrations

Pricing: Free and open source under the Apache-2.0 license.
Read more about TrivyWebsiteGitHub#1 Prisma Cloud alternative

Prowler

Prowler is an open-source cloud security platform that scans AWS, Azure, Google Cloud, Kubernetes, GitHub, Microsoft 365 and more, then prioritizes and fixes risks.

GitHub stars
15k
Last commit
yesterday
Latest release
5.48.0
Licence
Apache-2.0
Self-hosted
Yes
Hosted version
Available
prowler.comProwler homepage screenshot

Prowler is an open-source cloud security platform that automates security and compliance across cloud environments. It provides a single control plane where humans and agents collaborate, supporting connections to tools like Claude, Codex, Cursor, and Copilot.

The platform runs more than 2,500 checks across cloud accounts and maps results to 70+ compliance frameworks. Findings are ranked by severity, and users can follow step-by-step remediation for the console, CLI, or Infrastructure as Code, with Lighthouse AI to explain each fix.

Key features

  • Runs more than 2,500 security checks across cloud accounts
  • Maps results to 70+ compliance frameworks
  • Ranks findings by severity to prioritize risks
  • Provides step-by-step remediation for console, CLI, or IaC
  • Supports scanning of AWS, Azure, Google Cloud, Kubernetes, GitHub, Microsoft 365, and more
  • Offers a CLI, SDK, local server, and cloud edition
Read more about ProwlerWebsiteGitHub#2 Prisma Cloud alternative

Falco

Cloud native runtime security tool that monitors Linux kernel events and alerts on abnormal behavior and threats in real time.

GitHub stars
9.6k
Last commit
4 days ago
Latest release
0.45.2
Licence
Apache-2.0
Self-hosted
Yes
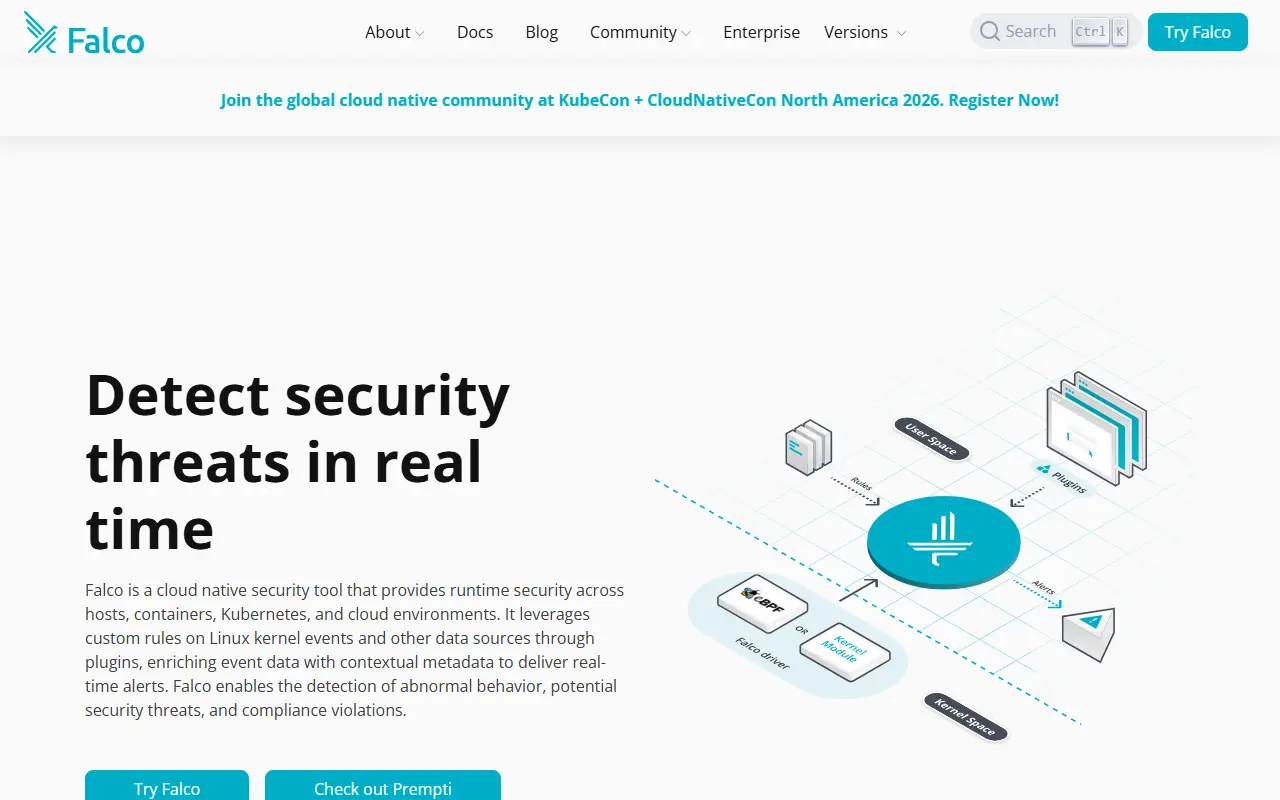
falco.orgFalco homepage screenshot

Falco is a cloud native runtime security tool for Linux. It detects and alerts on abnormal behavior and potential security threats in real time. At its core it is a kernel monitoring and detection agent that watches events such as system calls and evaluates them against custom rules.

Falco can enrich events with metadata from the container runtime and from Kubernetes, and the collected events can be analyzed off-host in SIEM or data lake systems. The project is split across repositories in the falcosecurity organization: the main repo holds the Falco binary, while others hold the core libraries and kernel drivers, the official ruleset, and plugins that extend detection beyond syscalls and container events.

Falco was originally created by Sysdig and is a graduated project of the Cloud Native Computing Foundation, used in production by various organizations. It is written in C++ and released under the Apache-2.0 license, with a change log and detailed documentation on falco.org. Topics in the repository mention eBPF-based collection.

Key features

  • Kernel-level syscall monitoring
  • Custom detection rules
  • Container and Kubernetes metadata enrichment
  • Official ruleset for common threats
  • Plugins for additional event sources
  • Export to SIEM or data lake systems

Pricing: Free and open source under the Apache-2.0 license.
Read more about FalcoWebsiteGitHub#3 Prisma Cloud alternative

Kubescape

Open-source Kubernetes security platform covering misconfiguration scanning, image vulnerabilities, compliance checks and runtime monitoring.

GitHub stars
12k
Last commit
2 days ago
Latest release
v4.0.20
Licence
Apache-2.0
Self-hosted
Yes
kubescape.ioKubescape homepage screenshot

Kubescape is an open-source Kubernetes security platform that covers the lifecycle from development to runtime. It was created by ARMO and is a Cloud Native Computing Foundation incubating project. It works in an IDE, in CI/CD pipelines and against running clusters, with the aim of saving administrators time on risk analysis and compliance work.

Misconfiguration scanning checks clusters, YAML files and Helm charts against NSA-CISA guidance, MITRE ATT&CK and CIS Benchmarks. Image vulnerability scanning detects CVEs using Grype, image patching uses Copacetic, and auto-remediation can fix manifest issues. Admission control uses Validating Admission Policies, runtime monitoring is eBPF-based through Inspektor Gadget, and an MCP server connects AI assistants.

Kubescape is written in Go and released under the Apache-2.0 license. It installs through options such as Homebrew and Krew, and an in-cluster operator is available for continuous scanning. Results include an overview of control plane status, access control risks, workload misconfigurations, network policy gaps and compliance scores.

Key features

  • Misconfiguration scanning against NSA-CISA, MITRE, CIS
  • Image vulnerability scanning with Grype
  • Automatic image patching with Copacetic
  • Auto-remediation for Kubernetes manifests
  • eBPF-based runtime security monitoring
  • In-cluster operator and MCP server

Pricing: Free and open source under the Apache-2.0 license.
Read more about KubescapeWebsiteGitHub#4 Prisma Cloud alternative

Checkov

Checkov scans cloud infrastructure configurations to find misconfigurations before they are deployed.

GitHub stars
9.2k
Last commit
yesterday
Latest release
3.4.4
Licence
Apache-2.0
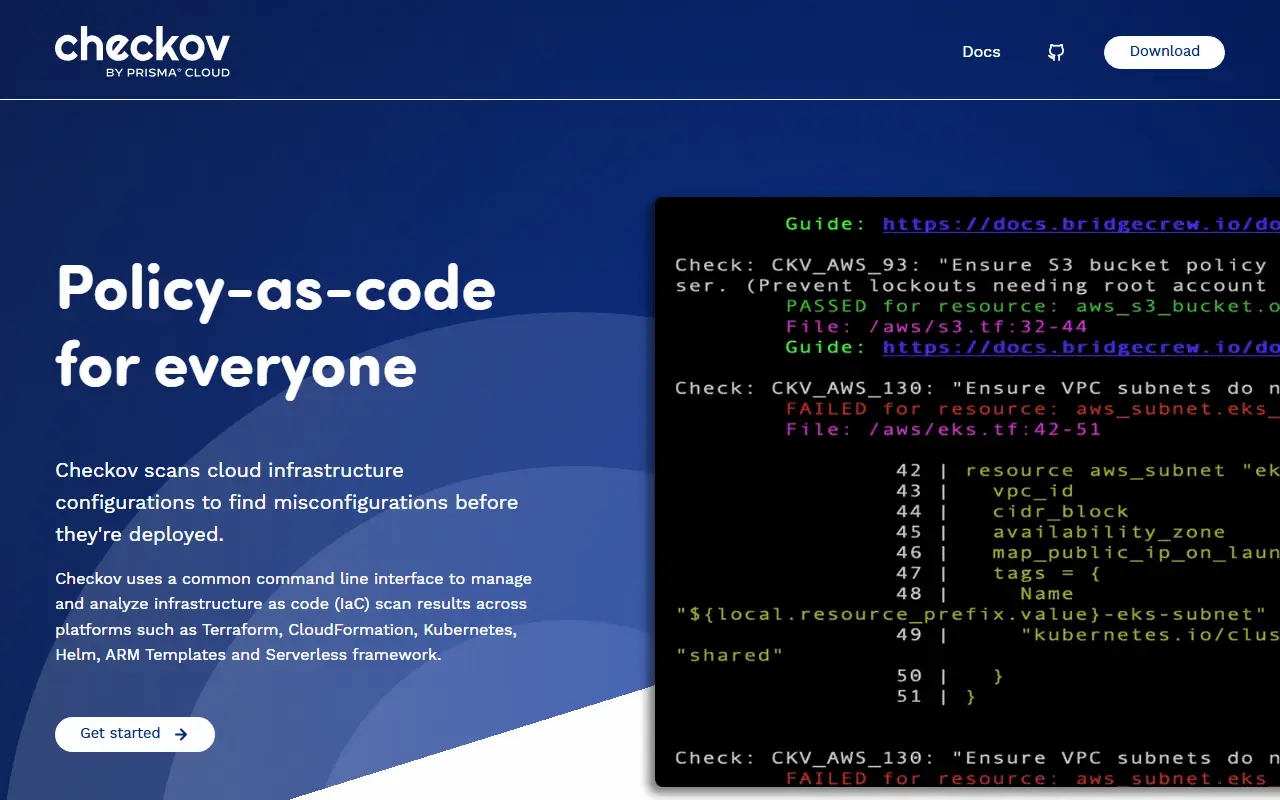
checkov.ioCheckov homepage screenshot

Checkov is a policy-as-code tool that scans cloud infrastructure configurations to find misconfigurations before they are deployed. It uses a common command line interface to manage and analyze infrastructure as code scan results across platforms such as Terraform, CloudFormation, Kubernetes, Helm, ARM Templates, and Serverless framework.

The tool supports attribute-based policies for scanning cloud resources at build-time and graph-based policies for analyzing relationships between cloud resources. It can be integrated into existing developer workflows and CI/CD pipelines to prevent misconfigurations from being deployed.

Key features

  • Scans cloud infrastructure configurations for misconfigurations before deployment
  • Supports Terraform, CloudFormation, Kubernetes, Helm, ARM Templates, Serverless, and AWS CDK
  • Attribute-based policies for scanning cloud resources at build-time
  • Graph-based policies for analyzing relationships between cloud resources
  • Extensible policy management for custom policies, providers, and suppressions
  • Integration with CI/CD and version control systems
Read more about CheckovWebsiteGitHub#5 Prisma Cloud alternative

Steampipe

An open-source command-line tool for querying cloud APIs and other data sources with SQL, without ETL or a separate database.

GitHub stars
8k
Last commit
yesterday
Latest release
v2.4.9
Licence
AGPL-3.0
Hosted version
Available
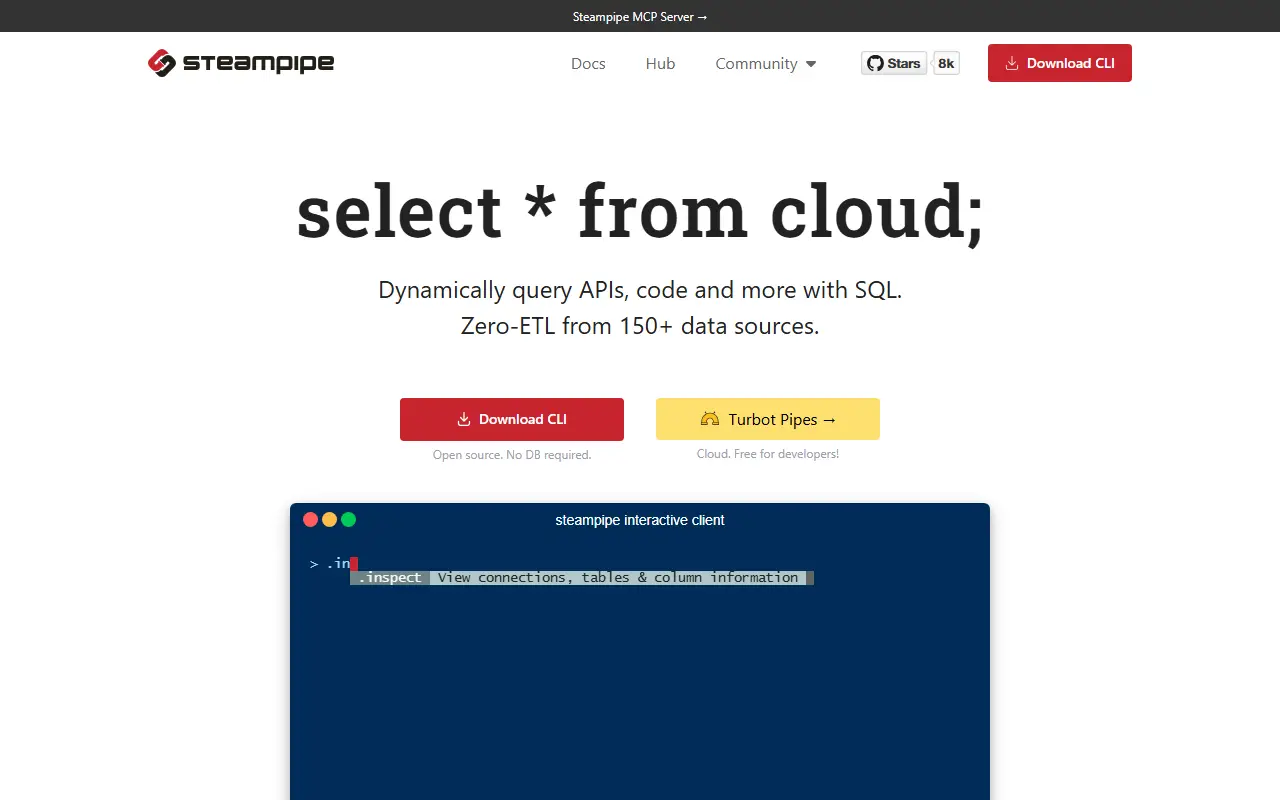
steampipe.ioSteampipe homepage screenshot

Steampipe provides a common SQL interface for dynamically querying APIs, code and more. The site cites zero-ETL access to more than 150 data sources and treats your cloud as a live database, so queries run against current configuration data rather than a synced copy. It is open source and does not need a database.

Typical questions are which users have MFA enabled right now or which security groups are open to the world, filed under compliance and security use cases. Live cloud configuration data can be joined with internal or external data sets. The CLI is licensed AGPL-3.0, a plugin library covers the data sources, and an MCP server and the Turbot Pipes cloud service are offered alongside.

Key features

  • SQL over APIs and cloud services
  • Join live cloud data with other data sets
  • Queries run against live data, not a synced copy
  • Large library of plugins
  • Compliance and security checks written as queries

Pricing: The CLI is open source. The Turbot Pipes cloud service is listed as free for developers.

Read more about SteampipeWebsiteGitHub#6 Prisma Cloud alternative

KICS

KICS scans Infrastructure as Code for security vulnerabilities, compliance issues, and misconfigurations.

GitHub stars
2.7k
Last commit
3 days ago
Latest release
v2.2.1
Licence
Apache-2.0
Self-hosted
Yes
kics.ioKICS homepage screenshot

KICS is an open source static code analysis tool for Infrastructure as Code. It scans IaC files to find security vulnerabilities, compliance issues, and infrastructure misconfigurations early in the development cycle.

The tool supports multiple IaC platforms including Terraform, Kubernetes, Docker, AWS CloudFormation, Ansible, Helm, and others. It includes over 2400 customizable queries and is designed to be easy to install, run, and integrate into CI pipelines.

Key features

  • Scans Infrastructure as Code for security vulnerabilities, compliance issues, and misconfigurations
  • Supports Terraform, Kubernetes, Docker, AWS CloudFormation, Ansible, Helm, Google Deployment Manager, AWS SAM, Microsoft ARM, Azure
  • Includes over 2400 customizable queries
  • Open source scanning engine and queries
  • Extensible architecture for adding new IaC support and custom queries
  • Easy to integrate into CI pipelines
Read more about KICSWebsiteGitHub#7 Prisma Cloud alternative

OpenSCAP

OpenSCAP is a library and command-line tool for parsing and evaluating SCAP standard components, supporting configuration and vulnerability scans.

GitHub stars
1.8k
Last commit
3 days ago
Latest release
1.4.6
Licence
LGPL-2.1
Self-hosted
Yes
open-scap.orgOpenSCAP homepage screenshot

OpenSCAP is a library and command-line tool that parses and evaluates each component of the SCAP standard. The library enables creation of new SCAP tools, while the command-line tool, oscap, formats content into documents or scans the system based on that content. It supports SCAP 1.2 and is backward compatible with SCAP 1.1 and 1.0.

The tool can evaluate DISA STIGs, NIST's USGCB, and Red Hat's Security Response Team's content. It performs configuration and vulnerability scans of a local system, evaluating XCCDF benchmarks and OVAL definitions and generating results. OpenSCAP is available on various Linux distributions and, since version 1.3.0, also on Microsoft Windows.

Key features

  • Parses and evaluates each component of the SCAP standard
  • Command-line tool oscap for configuration and vulnerability scans
  • Supports SCAP 1.2, backward compatible with SCAP 1.1 and 1.0
  • Evaluates DISA STIGs, NIST USGCB, and Red Hat Security Response Team content
  • Evaluates XCCDF benchmarks and OVAL definitions
  • Available on Linux distributions and Microsoft Windows
Read more about OpenSCAPWebsiteGitHub#8 Prisma Cloud alternative

tfsec

tfsec is a static analysis scanner for Terraform code that finds cloud misconfigurations, now being folded into Aqua Security's Trivy.

GitHub stars
7.1k
Last commit
7 mo ago
Latest release
v1.28.14
Licence
MIT
Self-hosted
Yes
aquasecurity.github.iotfsec homepage screenshot

tfsec is a security scanner that uses static analysis of Terraform code to spot potential misconfigurations. It checks infrastructure as code against hundreds of built-in rules for the major cloud providers, so problems such as open storage or weak settings can be caught in review or CI before resources are deployed.

It scans local and remote modules, evaluates HCL expressions, Terraform functions and relationships between resources, works with the Terraform CDK, and applies user-defined Rego policies. Output is available in several formats, including a readable default and JSON. The README announces that tfsec is now part of Trivy, the broader Aqua Security scanner, and encourages users to migrate, with a guide comparing the two tools.

tfsec stays available for the time being, but engineering attention goes to Trivy, which offers more languages and integrations and commercial support from Aqua. tfsec is written in Go and licensed under MIT, and runs locally or in CI with nothing to host. It suits DevSecOps teams with existing Terraform scanning who are planning their move to Trivy.

Key features

  • Static analysis of Terraform code
  • Hundreds of built-in misconfiguration rules
  • Scans local and remote modules
  • Custom Rego policy support
  • Multiple output formats
  • Migration path to Trivy

Pricing: Free and open source under the MIT licence.

Read more about tfsecWebsiteGitHub#9 Prisma Cloud alternative

Commercial Prisma Cloud alternatives

Hosted, closed-source products that compete with Prisma Cloud. Showing 12 of 18.

See every Prisma Cloud alternative on its tool page

Prisma Cloud alternatives: questions

What is the best open-source alternative to Prisma Cloud?
Trivy is the top-ranked open-source alternative to Prisma Cloud on Enlisted: A security scanner that finds vulnerabilities, misconfigurations, secrets and license issues in container images, filesystems, Git repositories and Kubernetes. Other strong options are Prowler, Falco, Kubescape and Checkov.
What are the best commercial alternatives to Prisma Cloud?
Sysdig, Orca Security, Aqua Security, Amazon GuardDuty and Qualys are among the hosted, closed-source alternatives to Prisma Cloud listed on Enlisted, which lists 18 in total. Compare their pricing and features on each tool page.
Are these Prisma Cloud alternatives free?
All 9 are open source, so the code is free to use under its licence, and all of them can be self-hosted on your own server or computer. 2 also offer a paid or managed cloud version if you'd rather not host it yourself.
How is this list of Prisma Cloud alternatives ranked?
By a score built from GitHub stars, star growth over the last 30 days and how recently the code changed. 8 of these projects shipped code in the last 30 days. Data is refreshed daily, and nobody can pay to move up.

People also look for alternatives to…

View all