
 Arctic Wolf
 Trellix
 Microsoft Sentinel
 IBM QRadar
 Exabeam
 Google Security Operations
 Vectra AI
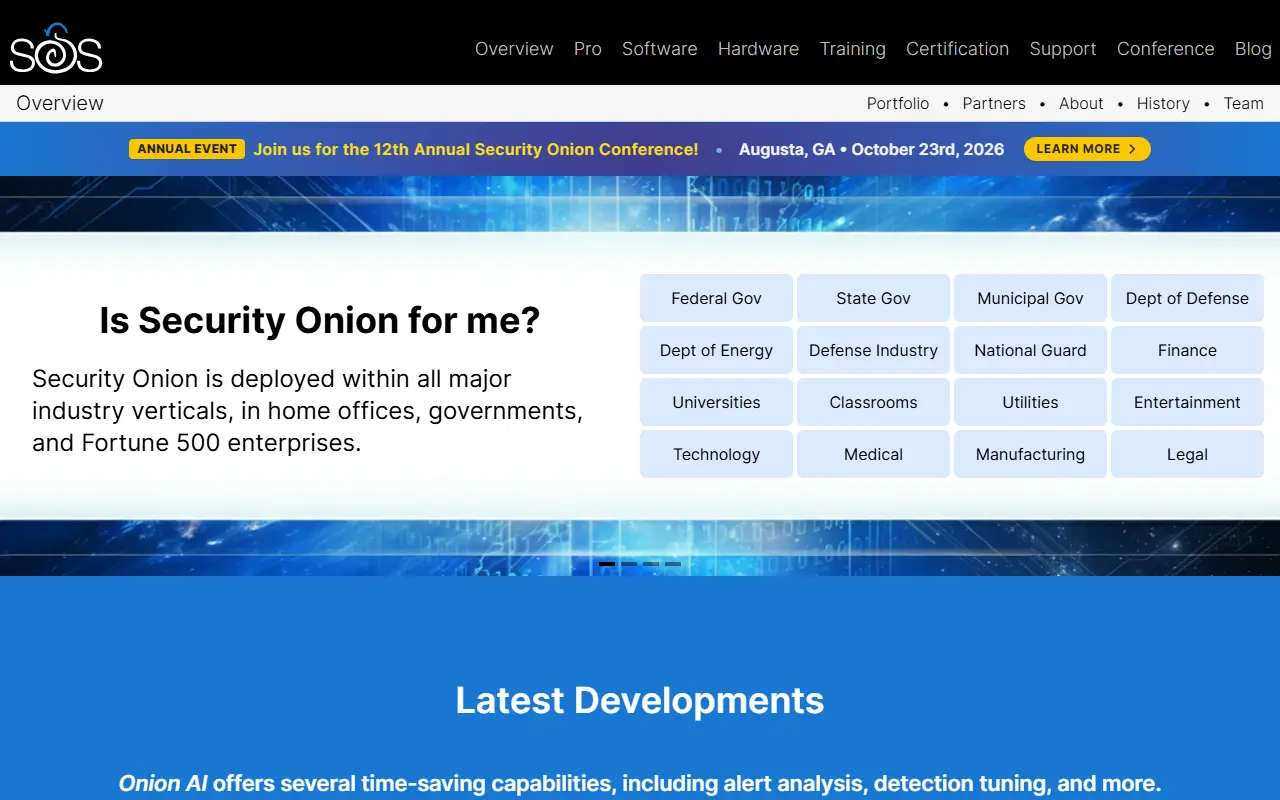
About Security Onion
Security Onion is a no-cost, open Linux distribution built for threat hunting, security monitoring across an enterprise, and log management. It bundles a suite of tools designed to work together so defenders get visibility into both network and host activity from a single platform.
The Security Onion Console is a unified web interface for analyzing events and managing the deployment, with its own tools for alerting, dashboards, hunting, packet capture, detections and case management. Underneath it uses the Elastic Stack for search, Suricata for network intrusion detection, Elastic Fleet for host monitoring, Zeek for network metadata and other tools such as osquery and CyberChef. The installer and configuration are largely shell scripts.
The repository license appears as 'Other' on GitHub. Security Onion is deployed on your own hardware or virtual machines, either standalone or as a distributed grid. It suits security operations centers, incident responders and blue teams that want an integrated, open alternative to commercial monitoring platforms.
Key features
- Unified Security Onion Console web interface
- Network intrusion detection with Suricata
- Network metadata from Zeek
- Elastic Stack search and dashboards
- Case management and threat hunting
- Packet capture and detections
Good fit for
- →Security operations center monitoring
- →Threat hunting across network traffic
- →Incident investigation with full packet capture
- Built with
- Shell
- Tags
- security
- threat-hunting
- ids
- siem
- log-management
- suricata
- zeek
- blue-team
Security Onion: questions and answers
- What is Security Onion used for?
- Security Onion is a free Linux platform for threat hunting, network and host security monitoring and log management, with a unified web console. It is a good fit for security operations center monitoring, threat hunting across network traffic and incident investigation with full packet capture.
- Is Security Onion open source?
- Yes. Security Onion is open source under a custom licence. Its source code is on GitHub at Security-Onion-Solutions/securityonion and is written mainly in Shell.
- Is Security Onion free?
- Yes. Security Onion is open source, so the software itself is free to use under the terms of its own licence.
- Can I self-host Security Onion?
- Yes. Security Onion can be self-hosted on your own server or infrastructure; there is no official hosted version.
- What is Security Onion an alternative to?
- Security Onion is an open-source alternative to Splunk, Darktrace, Microsoft Defender and Sumo Logic. Other open-source alternatives to Splunk include Wazuh and Graylog.
- Is Security Onion actively maintained?
- Yes. The most recent commit to Security Onion was on 2 October 2026, and the latest release is 3.3.0-20260911, published on 11 September 2026. The project has 4.9k stars on GitHub.
Open-source alternatives to Security Onion
See all
Wazuh
Security
Wazuh - The Open Source Security Platform. Unified XDR and SIEM protection for endpoints a
OSSvs Splunk★ 17k
Graylog
Monitoring & Observability
Free and open log management
OSSvs Splunk★ 8.2k
OSSEC
Security
OSSEC is an Open Source Host-based Intrusion Detection System that performs log analysis,
GPL-2.0vs CrowdStrike★ 5.1k
Suricata
Security
Suricata is a network Intrusion Detection System, Intrusion Prevention System and Network
GPL-2.0vs Palo Alto Networks★ 6.7k
Falco
Security
Cloud Native Runtime Security
Apache-2.0vs Wiz★ 9.4k
Tracecat
Security
Open-source security automation platform for teams and AI agents
AGPL-3.0vs Tines★ 3.8k
SaaS alternatives to Security Onion
See all
Splunk
Monitoring & Observability
Splunk is a data platform for security and observability that collects, searches and analyzes machine data to detect threats and prevent downtime.
SaaS
Darktrace
Security
Self-learning AI that detects anomalous activity across network, cloud and email
SaaS
Microsoft Defender
Security
Microsoft endpoint, identity and cloud threat protection suite
SaaS
Sumo Logic
Monitoring & Observability
Cloud log analytics and security monitoring platform
SaaS
CrowdStrike
Security
Cloud-native endpoint protection, threat detection and response platform
SaaS
SentinelOne
Security
AI-driven endpoint, cloud and identity security platform with automated response
SaaS