 TrackMedia
 TrackRev

About osquery
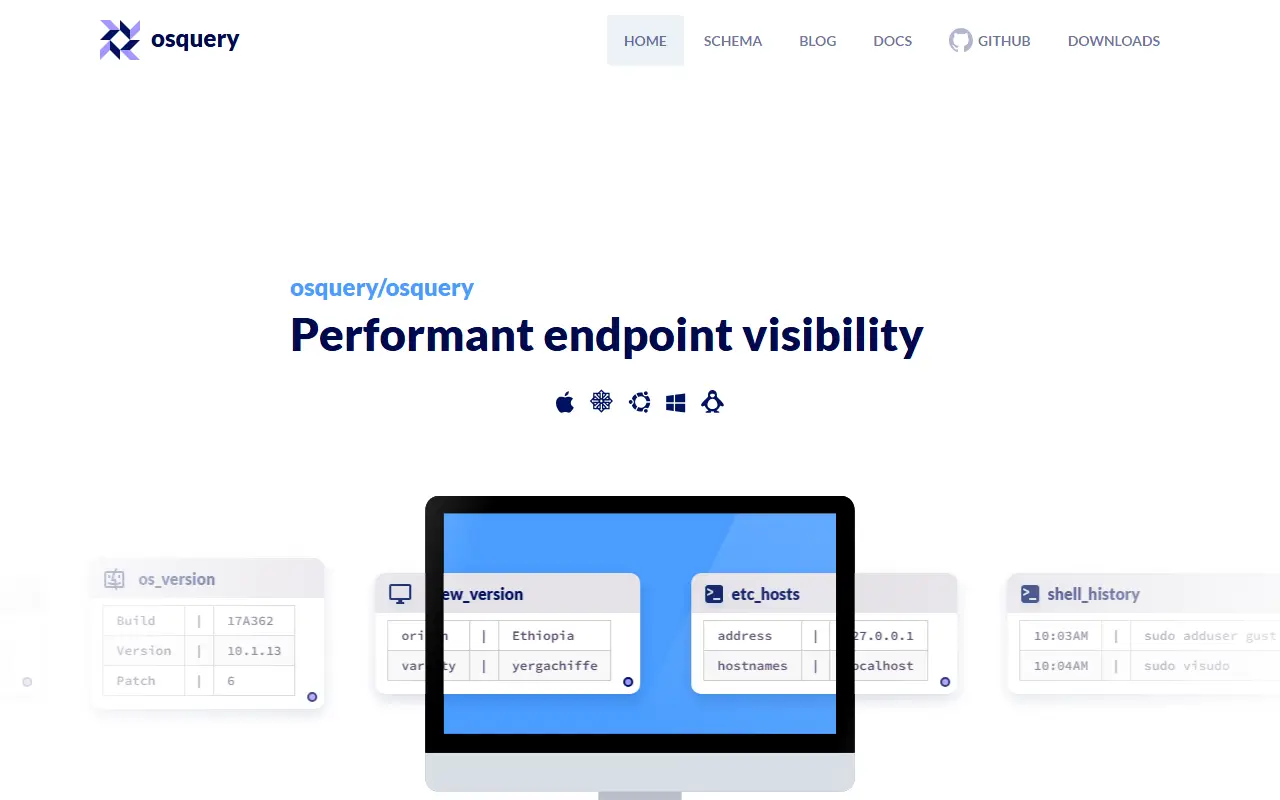
osquery is an instrumentation, monitoring and analytics framework that lets you ask questions about an operating system using SQL. It makes the machine look like a high-performance relational database, so instead of writing scripts for each platform you query tables describing things like processes, kernel modules, network sockets, browser extensions, hardware events and file hashes.
It works on Linux, macOS and Windows. New tables are added through a simple plugin and extensions API, and a public schema reference documents the available tables. The README illustrates its expressiveness with sample queries such as listing users or finding processes whose binaries were deleted from disk. Resources include documentation on ReadTheDocs, downloads, Stack Overflow and a Slack community, and topics tag it for security, intrusion detection and monitoring.
osquery is written in C++ and its license is listed as 'Other' on GitHub, so check the repository for the exact terms. It runs locally on each endpoint, and organizations typically deploy it across a fleet and collect results with their own tooling. It suits security teams, IT administrators and detection engineers who want consistent endpoint visibility.
Key features
- SQL queries over operating system data
- Tables for processes, network connections and kernel modules
- Linux, macOS and Windows support
- Plugin and extensions API for new tables
- Public schema documentation
- Suitable for fleet-wide endpoint monitoring
Good fit for
- Endpoint security investigation
- Inventory of software and hardware across machines
- Threat hunting with SQL
osquery: questions and answers
- What is osquery used for?
- osquery is a SQL-powered framework that exposes an operating system as a relational database for monitoring, security investigation and analytics on Linux, macOS and Windows. It is a good fit for endpoint security investigation, inventory of software and hardware across machines, and threat hunting with SQL.
- Is osquery open source?
- Yes. osquery is open source under a custom licence. Its source code is on GitHub at osquery/osquery and is written mainly in C++.
- Is osquery free?
- Yes. osquery is open source, so the software itself is free to use under the terms of its own licence.
- What is osquery an alternative to?
- osquery is an open-source alternative to Tanium. Other open-source alternatives to Tanium include Fleet, Wazuh and Ansible.
- Is osquery actively maintained?
- Yes. The most recent commit to osquery was on 12 November 2026, and the latest release is 5.24.1, published on 29 October 2026. The project has 24k stars on GitHub, with 119 added in the last 30 days.
Open-source alternatives to osquery
See all
Fleet
Security
Open device management
OSSvs Jamf★ 7.2k
Wazuh
Security
Wazuh - The Open Source Security Platform. Unified XDR and SIEM protection for endpoints a
OSSvs Splunk★ 18k
Ansible
CI/CD & DevOps
Ansible is a radically simple IT automation platform that makes your applications and syst
GPL-3.0vs AWS CodeDeploy★ 71k
Salt Project
CI/CD & DevOps
Software to automate the management and configuration of infrastructure and applications a
Apache-2.0vs Red Hat Ansible Automation Platform★ 16k
Chef
CI/CD & DevOps
Chef Infra, a powerful automation platform that transforms infrastructure into code automa
Apache-2.0vs Northflank★ 8.3k
CrowdSec
Security
Open-source IDS/IPS, WAF and bot detection for Linux, Windows, Docker and Kubernetes, with
MITvs Cloudflare★ 16k
SaaS alternatives to osquery
See all
Tanium
Security
Endpoint management and security platform
SaaS
Ivanti
Security
IT and security management software for endpoints, patching and service management
SaaS
NinjaOne
Security
Endpoint management and remote monitoring software for IT teams and MSPs
SaaS
Omnissa Workspace ONE
Security
Unified endpoint management and digital workspace platform
SaaS
Adverse Monitor
Security
Cyber threat intelligence tool that watches the dark web for incident claims naming your company
SaaS
Beacky
Security
Invisible beacons that alert you when your website is cloned on unauthorized domains
SaaS