 TrackMedia
 TrackRev

 LogRhythm
 Splunk Observability Cloud
 Securonix
 Fortinet
 SolarWinds Network Performance Monitor
 ManageEngine OpManager
 Prisma Access
 CrowdStrike
 Datadog
 Azure Maps
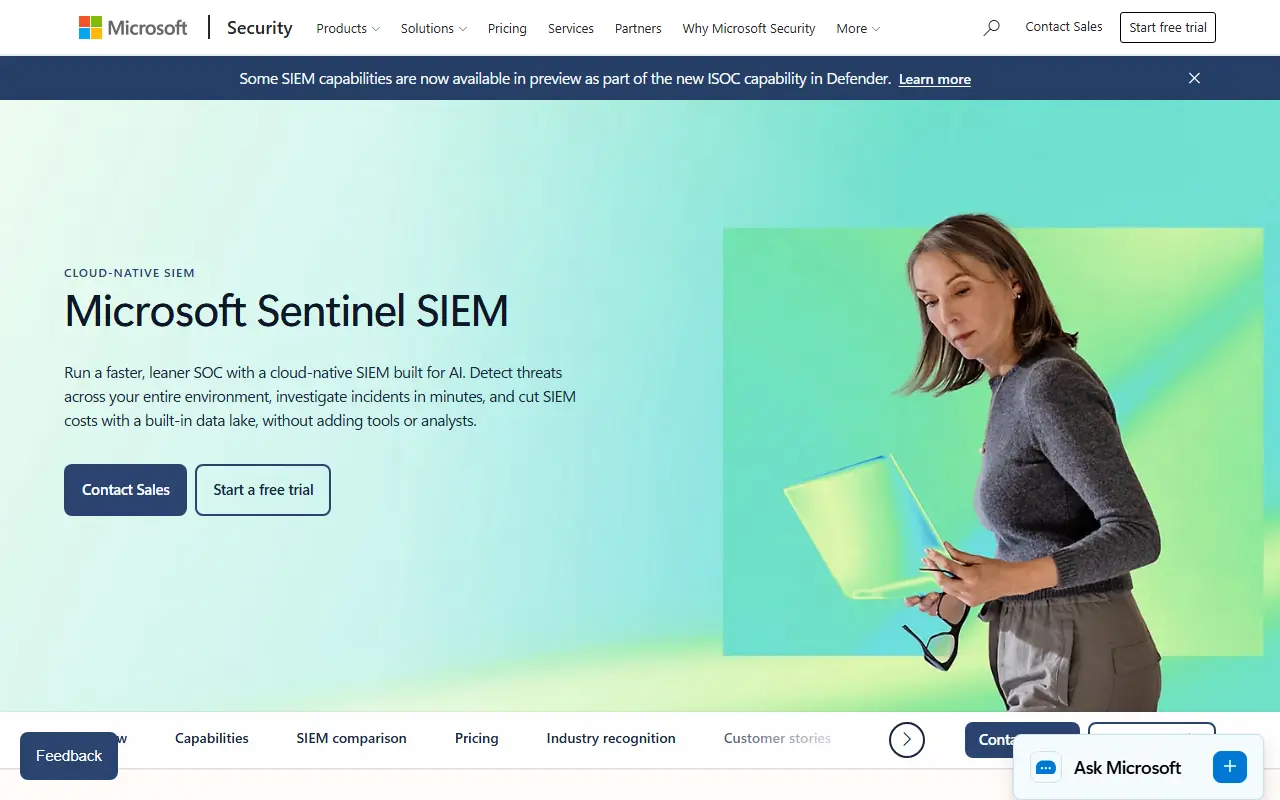
About Microsoft Sentinel
Microsoft Sentinel is a cloud-native security information and event management service, with security orchestration and automated response built in. It is aimed at security operations centers that want to detect threats, investigate them and respond from one place without running their own SIEM infrastructure.
Microsoft says it helps teams detect threats faster, automate response and lower SIEM costs through a data lake. It sits within the Microsoft Security portfolio next to Defender, Entra, Intune and Purview, and the page notes that some SIEM capabilities are now in preview as part of a new security operations capability in Defender.
Sentinel is a hosted Microsoft cloud service with a free trial, a pricing overview and extensive documentation, training and certifications. There is no self-hosted edition. Pricing is covered on a separate Microsoft Security pricing overview page, and product trials are available.
Key features
- Cloud-native SIEM for security operations
- Automated response with SOAR
- Threat detection across data sources
- Data lake for lower-cost log storage
- Integration with Microsoft Defender
- Free trial available
Good fit for
- SOC teams centralizing security logs and alerts
- Organizations replacing on-premises SIEM infrastructure
Microsoft Sentinel: questions and answers
- What is Microsoft Sentinel used for?
- Microsoft Sentinel is a cloud-native SIEM and SOAR service that helps security operations teams detect threats and automate incident response. It is a good fit for SOC teams centralizing security logs and alerts, and organizations replacing on-premises SIEM infrastructure.
- How much does Microsoft Sentinel cost?
- Microsoft Sentinel is a paid product with no free plan.
- Is Microsoft Sentinel open source?
- No. Microsoft Sentinel is proprietary (closed-source) software and can't be self-hosted. Open-source alternatives to Microsoft Sentinel include Wazuh, Tracecat and Security Onion.
- What are some alternatives to Microsoft Sentinel?
- Microsoft Sentinel competes with Splunk, IBM QRadar and Exabeam. For open-source options, see Enlisted's ranked list of open-source Microsoft Sentinel alternatives.
Open-source alternatives to Microsoft Sentinel
See all
Wazuh
Security
Wazuh - The Open Source Security Platform. Unified XDR and SIEM protection for endpoints a
OSSvs Splunk★ 18k
Tracecat
Security
Open-source security automation platform for teams and AI agents
AGPL-3.0vs Tines★ 3.9k
Security Onion
Security
Security Onion is a free and open platform for threat hunting, enterprise security monitor
OSSvs Splunk★ 5k
Graylog
Monitoring & Observability
Free and open log management
OSSvs Splunk★ 8.2k
Kibana
Monitoring & Observability
Your window into all of your data
OSSvs Splunk★ 21k
Falco
Security
Cloud Native Runtime Security
Apache-2.0vs Wiz★ 9.6k
SaaS alternatives to Microsoft Sentinel
See all
Splunk
Monitoring & Observability
Splunk is a data platform for security and observability that collects, searches and analyzes machine data to detect threats and prevent downtime.
SaaS
IBM QRadar
Security
Security information and event management platform from IBM
SaaS
Exabeam
Security
SIEM and security analytics platform with behavioral detection
SaaS
Google Security Operations
Security
Cloud security operations platform with SIEM and SOAR from Google
SaaS
Sumo Logic
Monitoring & Observability
Cloud log analytics and security monitoring platform
SaaS
Rapid7
Security
Vulnerability management, SIEM and managed detection tools for security teams
SaaS