 TrackMedia
 TrackRev

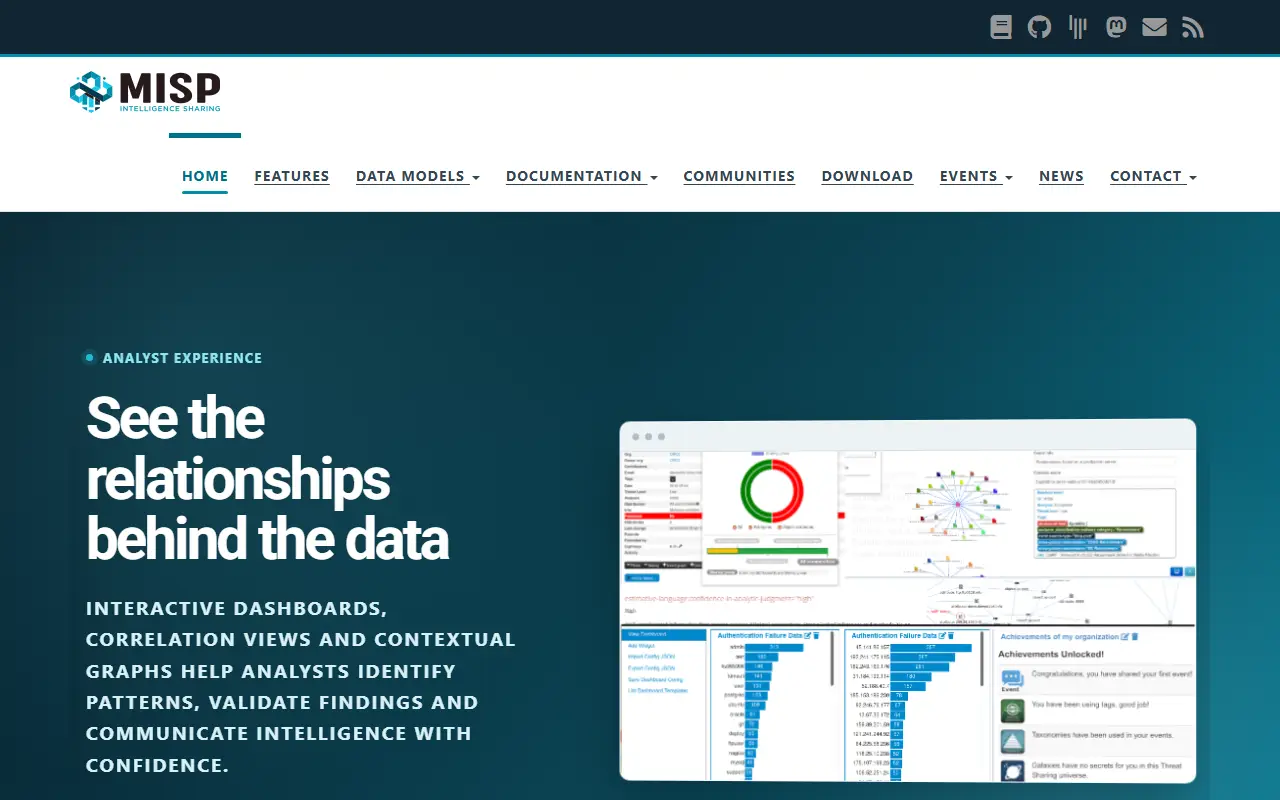
About MISP
MISP is open-source software for gathering, storing, distributing and sharing cyber security indicators and details from incident and malware analysis. It is aimed at incident analysts, security and ICT staff and malware reverse engineers, who use it to exchange structured information efficiently.
Beyond sharing, MISP supports the consumption of that information by network intrusion detection systems, log analysis tools and SIEMs. Threat intelligence from indicators through techniques to tactics can be described in a machine-readable form or as detailed reports in Markdown, and the integrated reporting system cross-references the structured data. Repository topics point to STIX, threat hunting and fraud detection use cases.
The core software is written in PHP and licensed under AGPL-3.0. The README says it can be deployed on premises, in the cloud or as a SaaS solution, so organizations of different sizes can run their own instance and choose which partners to share data with. Installation guides, documentation and a support site are linked from the repository.
Key features
- Collect and store threat indicators
- Share structured intelligence with communities
- Machine-readable and Markdown reports
- Export to IDS, log analysis tools and SIEMs
- STIX-related threat intelligence formats
- On-premise, cloud or SaaS deployment
Good fit for
- Sharing indicators between security teams
- Feeding threat intelligence into a SIEM
MISP: questions and answers
- What is MISP used for?
- MISP is an open-source threat intelligence platform for collecting, storing and sharing cyber security indicators between analysts and security teams. It is a good fit for sharing indicators between security teams and feeding threat intelligence into a SIEM.
- Is MISP open source?
- Yes. MISP is open source under the AGPL-3.0 licence. Its source code is on GitHub at MISP/MISP and is written mainly in PHP.
- Is MISP free?
- Yes. MISP is open source, so the software itself is free to use. A managed cloud version is also available.
- Can I self-host MISP?
- Yes. MISP can be self-hosted on your own server or infrastructure.
- What is MISP an alternative to?
- MISP is an open-source alternative to Recorded Future, Mandiant, Rapid7 and Torq. Other open-source alternatives to Recorded Future include OpenCTI.
- Is MISP actively maintained?
- Yes. The most recent commit to MISP was on 11 November 2026, and the latest release is v2.5.51, published on 11 November 2026. The project has 6.7k stars on GitHub, with 72 added in the last 30 days.
Open-source alternatives to MISP
See all
OpenCTI
Security
Open Cyber Threat Intelligence Platform
OSSvs Recorded Future★ 10k
Wazuh
Security
Wazuh - The Open Source Security Platform. Unified XDR and SIEM protection for endpoints a
OSSvs Splunk★ 18k
Kibana
Monitoring & Observability
Your window into all of your data
OSSvs Splunk★ 21k
Security Onion
Security
Security Onion is a free and open platform for threat hunting, enterprise security monitor
OSSvs Splunk★ 5k
DefectDojo
Security
Open-Source Unified Vulnerability Management, DevSecOps & ASPM
BSD-3-Clausevs Tenable★ 5.2k
OpenVAS
Security
This repository contains the scanner component for Greenbone Community Edition.
GPL-2.0vs Tenable★ 4.9k
SaaS alternatives to MISP
See all
Recorded Future
Security
Threat intelligence platform
SaaS
Mandiant
Security
Threat intelligence and incident response services and products from Google
SaaS
Rapid7
Security
Vulnerability management, SIEM and managed detection tools for security teams
SaaS
Torq
Security
Security automation platform for orchestrating SOC workflows and AI-assisted response
SaaS
isMalicious
Security
Cyber threat intelligence suite with a SIEM API, STIX/TAXII, OpenCTI and an MCP server
SaaS
Swimlane
Security
Low-code security automation platform for case management and incident response
SaaS