
About IBM QRadar
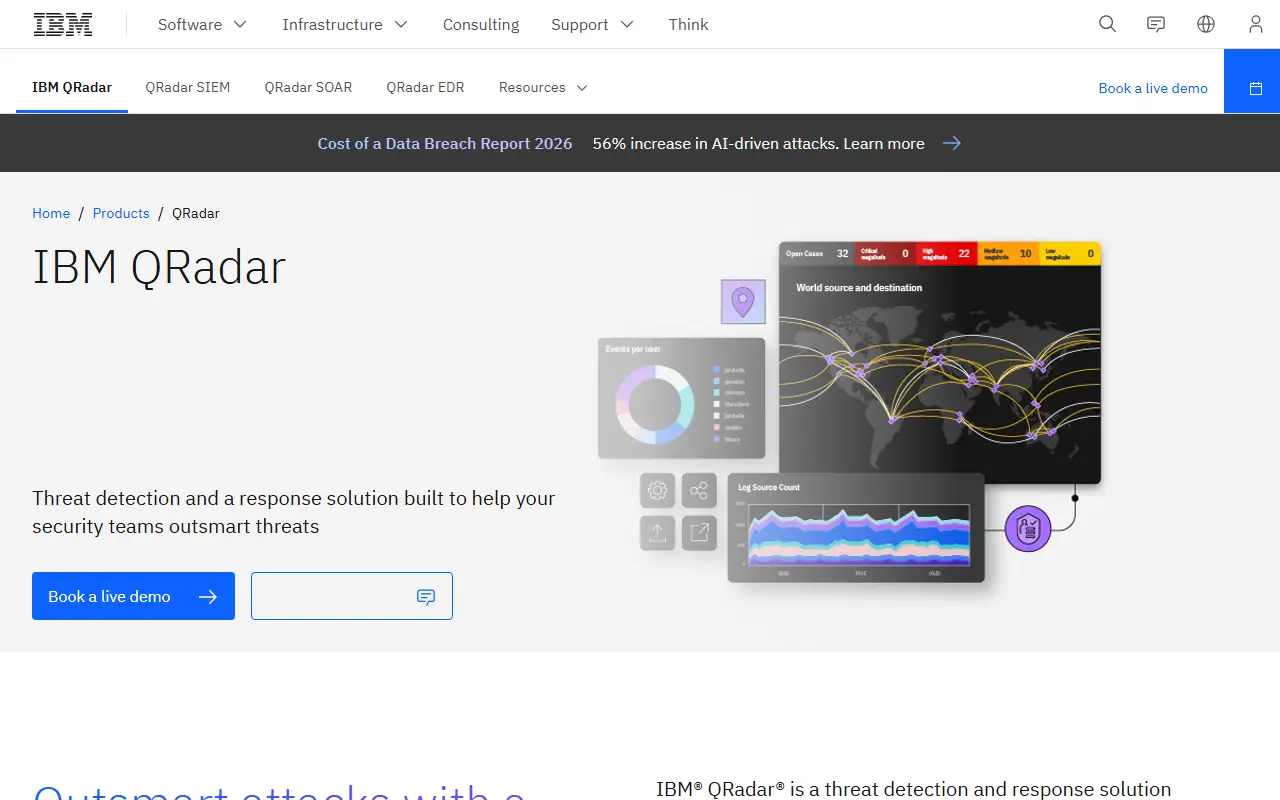
QRadar is a product from IBM for threat detection and response, designed for enterprise security teams. It aims to give visibility into activity across an organization so incidents can be detected, investigated and handled more efficiently.
The suite includes endpoint detection and response, SIEM, SOAR, user behavior analytics and network detection and response. The SIEM component applies network and user behavior analytics, and its UBA module builds a baseline of normal behavior for users and generates insights about risk from data already in the SIEM. A data collector supports passive protocols that listen for events on specific ports and active protocols that poll external sources through APIs.
QRadar is sold by IBM as a commercial product, and live demos can be booked on the site. IBM also offers SaaS and on-premises deployment, which makes it usable in both hosted and self-managed environments.
Key features
- SIEM with log and event correlation
- SOAR for automated incident response
- User behavior analytics baselines
- Network detection and response
- Endpoint detection and response
- Data collection from many telemetry sources
Good fit for
- →Enterprise SOCs correlating events from many systems
- →Teams detecting insider threats through behavior analysis
- Tags
- siem
- soar
- threat-detection
- ueba
- network-detection
- security-operations
- ibm
IBM QRadar: questions and answers
- What is IBM QRadar used for?
- IBM QRadar is a modular security suite covering SIEM, SOAR, user behavior analytics and network detection to help teams detect and respond to threats. It is a good fit for enterprise SOCs correlating events from many systems and teams detecting insider threats through behavior analysis.
- How much does IBM QRadar cost?
- IBM QRadar doesn't publish fixed prices; pricing is quoted on request.
- Is IBM QRadar open source?
- No. IBM QRadar is proprietary (closed-source) software. Open-source alternatives to IBM QRadar include Wazuh, Security Onion and Graylog.
- Can I self-host IBM QRadar?
- Yes. Although IBM QRadar is closed source, it can be self-hosted on your own servers, and the vendor also offers a hosted version.
- What are some alternatives to IBM QRadar?
- IBM QRadar competes with Splunk, Microsoft Sentinel and Exabeam. For open-source options, see Enlisted's ranked list of open-source IBM QRadar alternatives.
Open-source alternatives to IBM QRadar
See all
Wazuh
Security
Wazuh - The Open Source Security Platform. Unified XDR and SIEM protection for endpoints a
OSSvs Splunk★ 17k
Security Onion
Security
Security Onion is a free and open platform for threat hunting, enterprise security monitor
OSSvs Splunk★ 4.9k
Graylog
Monitoring & Observability
Free and open log management
OSSvs Splunk★ 8.2k
Falco
Security
Cloud Native Runtime Security
Apache-2.0vs Wiz★ 9.4k
MISP
Security
MISP (core software) - Open Source Threat Intelligence and Sharing Platform
AGPL-3.0vs Recorded Future★ 6.6k
OSSEC
Security
OSSEC is an Open Source Host-based Intrusion Detection System that performs log analysis,
GPL-2.0vs CrowdStrike★ 5.1k
SaaS alternatives to IBM QRadar
See all
Splunk
Monitoring & Observability
Splunk is a data platform for security and observability that collects, searches and analyzes machine data to detect threats and prevent downtime.
SaaS
Microsoft Sentinel
Security
Cloud-native SIEM and SOAR service from Microsoft
SaaS
Exabeam
Security
SIEM and security analytics platform with behavioral detection
SaaS
Google Security Operations
Security
Cloud security operations platform with SIEM and SOAR from Google
SaaS
Sumo Logic
Monitoring & Observability
Cloud log analytics and security monitoring platform
SaaSRapid7
Security
Vulnerability management, SIEM and managed detection tools for security teams
SaaS