 TrackMedia
 TrackRev
About Logentries
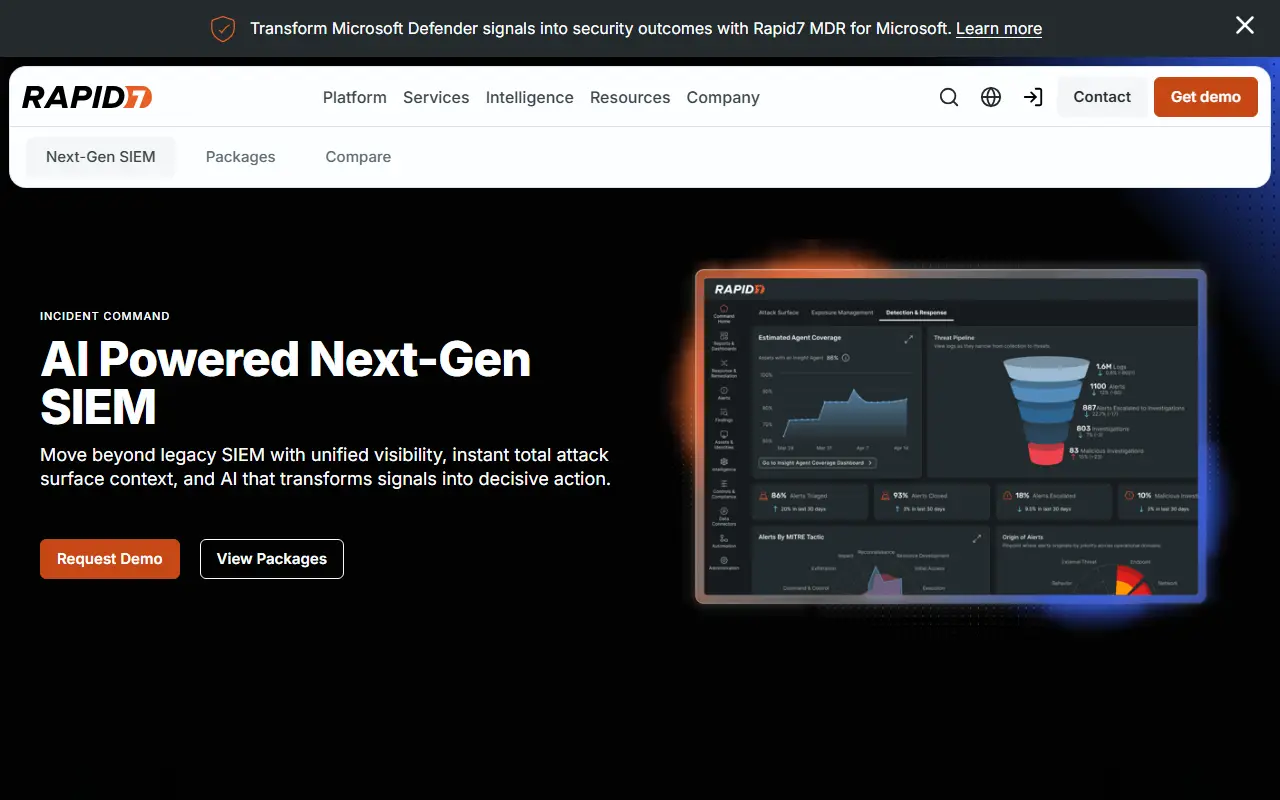
Incident Command is a next-generation security information and event management (SIEM) solution from Rapid7. It is designed for cloud-first environments and uses AI-powered detections to help security teams investigate and respond to threats.
The platform is part of Rapid7's broader Command Platform, which includes attack surface management, vulnerability management, and other security capabilities. It is positioned as a tool to help organizations respond faster and outpace attackers.
Key features
- AI-driven detections for investigation
- Cloud-native architecture for cloud-first environments
- Part of Rapid7's Command Platform
- Integrates with Microsoft Defender signals
Good fit for
- Security operations center (SOC) teams
- Incident response and threat hunting
- Cloud security monitoring and alerting
Logentries: questions and answers
- What is Logentries used for?
- Logentries is Rapid7's next-gen SIEM that uses AI-driven detections to investigate and respond to security incidents in cloud-first environments. It is a good fit for security operations center (SOC) teams, incident response and threat hunting, and cloud security monitoring and alerting.
- Is Logentries open source?
- No. Logentries is proprietary (closed-source) software. In the Security category, open-source options include Wazuh, MISP and Security Onion.
- What are some alternatives to Logentries?
- Logentries competes with Sumo Logic.
Open-source alternatives to Logentries
See all
Wazuh
Security
Wazuh - The Open Source Security Platform. Unified XDR and SIEM protection for endpoints a
OSSvs Splunk★ 18k
MISP
Security
MISP (core software) - Open Source Threat Intelligence and Sharing Platform
AGPL-3.0vs Recorded Future★ 6.7k
Security Onion
Security
Security Onion is a free and open platform for threat hunting, enterprise security monitor
OSSvs Splunk★ 5k
OSSEC
Security
OSSEC is an Open Source Host-based Intrusion Detection System that performs log analysis,
GPL-2.0vs CrowdStrike★ 5.1k
OpenBao
Security
OpenBao is a software solution to manage, store, and distribute sensitive data including s
MPL-2.0vs AWS Secrets Manager★ 9k
Infisical
Security
Infisical is the open-source platform for secrets, certificates, and privileged access man
OSSvs Doppler★ 30k
SaaS alternatives to Logentries
See all
Sumo Logic
Monitoring & Observability
Cloud log analytics and security monitoring platform
SaaS
Amazon GuardDuty
Security
Managed AWS threat detection service for accounts, workloads and data
SaaS
Exabeam
Security
SIEM and security analytics platform with behavioral detection
SaaS
Google Security Operations
Security
Cloud security operations platform with SIEM and SOAR from Google
SaaS
IBM QRadar
Security
Security information and event management platform from IBM
SaaS
Microsoft Sentinel
Security
Cloud-native SIEM and SOAR service from Microsoft
SaaS