About UseShipReady
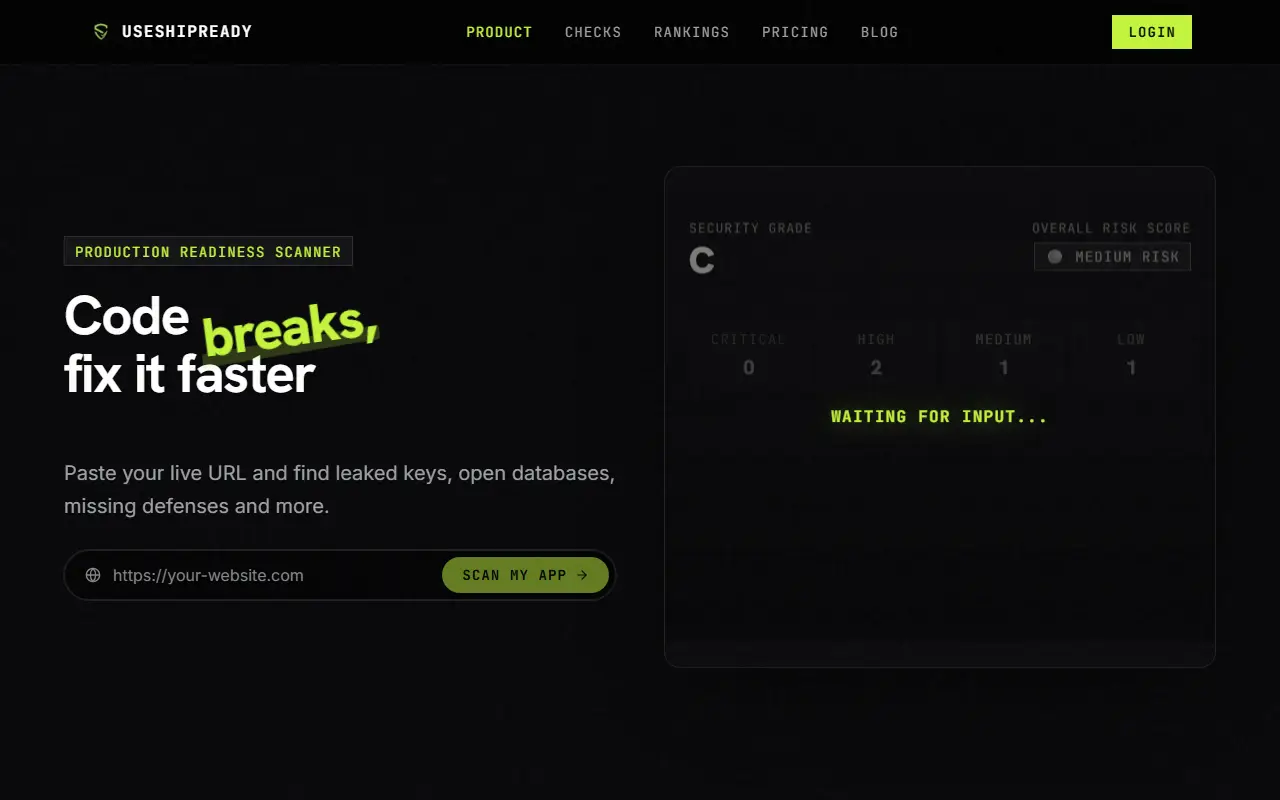
UseShipReady scans a deployed site and reports launch blockers. You paste a live URL, with no repository access or configuration, and it runs 198 checks across 10 pillars including security headers, cookie flags, exposed source maps, leaked model keys, email authentication with SPF, DKIM and DMARC, SEO and AI answer-engine visibility, performance, compliance such as cookies and accessibility, and database configuration signals such as Supabase row-level security. Findings are ranked by impact, and anything it could not test is named in the report.
Every finding comes with a fix prompt that can be pasted into Cursor, Claude Code or Lovable, for example telling an agent to move an API key off the frontend. Connected scans for a GitHub repository and a Supabase database are listed as coming soon, along with continuous uptime monitoring, and a VS Code extension pulls findings into the editor.
The site positions it for AI-built apps and offers a security scanner, threat detection, SEO scanner, AEO scanner, accessibility audit and email deliverability check from one subscription. It is a hosted service with a pricing page and a blog.
Key features
- 198 checks across 10 pillars
- Security header, cookie and CORS checks
- Exposed API key and source map detection
- SPF, DKIM and DMARC verification
- SEO and AI answer-engine checks
- Fix prompts for Cursor and Claude Code
- VS Code extension
Good fit for
- Checking an AI-built app before launch
- Finding leaked keys and missing security headers
UseShipReady: questions and answers
- What is UseShipReady used for?
- UseShipReady is a scanner that checks a live URL against 198 security, SEO, email, performance and compliance checks and returns a ranked report with fix prompts for AI coding tools. It is a good fit for checking an AI-built app before launch, and finding leaked keys and missing security headers.
- Is UseShipReady free?
- Yes. UseShipReady has a free plan, and paid plans start at $5 per month.
- Is UseShipReady open source?
- No. UseShipReady is proprietary (closed-source) software and can't be self-hosted. In the Security category, open-source options include Trivy, uBlock Origin and Cryptomator.
- What are some alternatives to UseShipReady?
- UseShipReady competes with Intruder, Invicti and Aikido Security.
Open-source alternatives to UseShipReady
See all
Trivy
Security
Find vulnerabilities, misconfigurations, secrets, SBOM in containers, Kubernetes, code rep
Apache-2.0vs Snyk★ 38kuBlock Origin
Security
uBlock Origin - An efficient blocker for Chromium and Firefox. Fast and lean.
GPL-3.0★ 68k
Cryptomator
Security
Cryptomator for Windows, macOS, and Linux: Secure client-side encryption for your cloud st
GPL-3.0vs Tresorit★ 16k
VeraCrypt
Security
Disk encryption with strong security based on TrueCrypt
OSS★ 12k
Certimate
Security
ssl tls https ssl-certificate ssl-certificates ssl-cert https-certificate https-certificat
MITvs Sectigo★ 9.3k
Certd
Security
开源SSL证书管理工具;全自动证书申请、更新、续期;通配符证书,泛域名证书申请;证书自动化部署到阿里云、腾讯云、主机、群晖、宝塔;https证书,pfx证书,der证书,TLS证书
AGPL-3.0vs Sectigo★ 5k
SaaS alternatives to UseShipReady
See all
Intruder
Security
Cloud-based vulnerability scanner for external attack surface
SaaS
Invicti
Security
Web application security scanning platform formerly known as Netsparker
SaaS
Aikido Security
Security
All-in-one application security platform for code, cloud and runtime scanning
SaaS
CheckVibe
Security
Scans live sites for security, SEO and performance issues left behind by AI coding agents
SaaS
AuditYourApp
Security
Scans Supabase projects, websites and mobile apps for exposed RLS rules, open RPCs and leaked API keys
SaaS
Vibe App Scanner
Security
Automated external security scanner for AI-built apps with one-click AI-ready fix instructions
SaaS