About CheckVibe
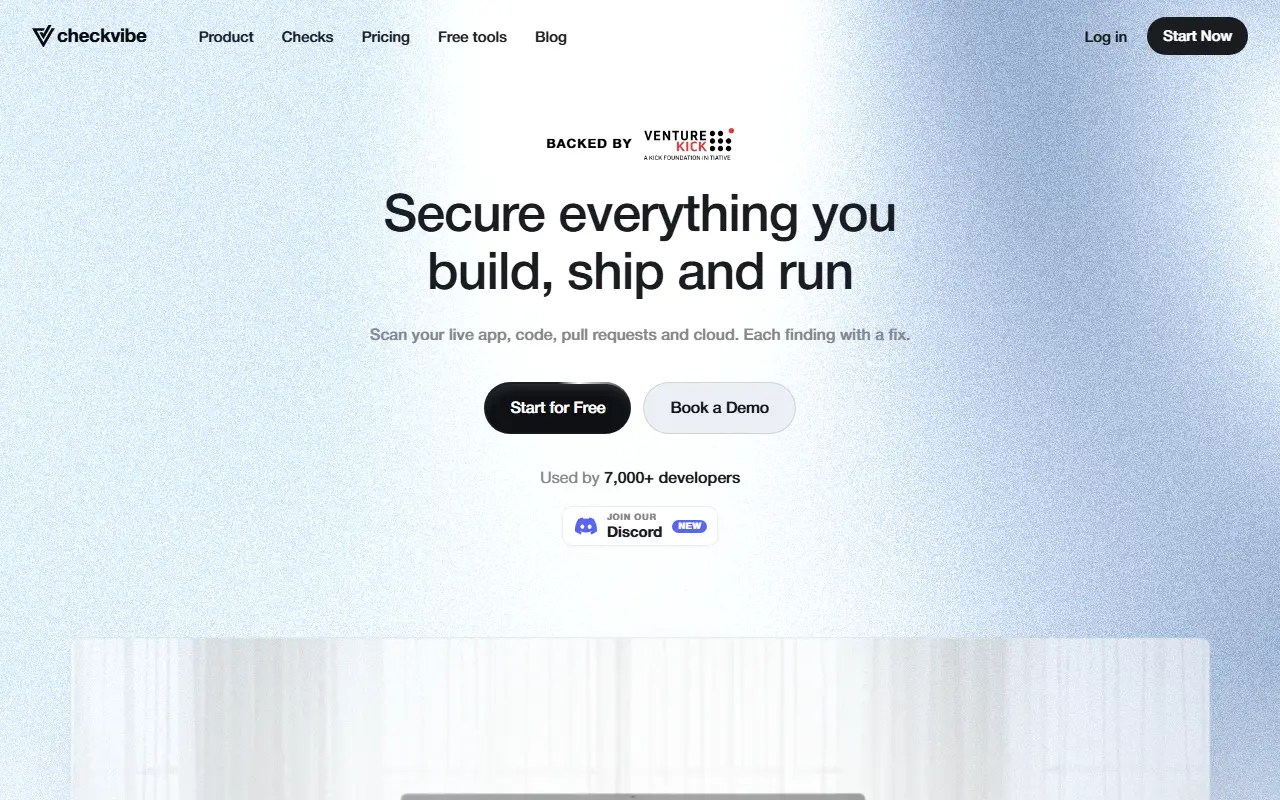
CheckVibe is a security platform for developer teams building with AI coding tools. It scans a live app, code repositories, pull requests, dependencies, secrets, cloud setup and containers, ranks each finding by impact and returns a full report in about a minute.
Each finding comes with a fix, and CheckVibe can turn findings into a copy-paste prompt that a coding agent such as Cursor or Claude can use to repair the issue. It can connect to GitHub repositories and a Supabase backend, review pull requests, detect live threats and monitor uptime. An MCP server and REST API let it plug into Cursor, Windsurf, VS Code, Codex and Copilot. A free start with no credit card is offered, and the site lists performance, accessibility and compliance checks as well.
Key features
- Scans of live apps, code and pull requests
- Detection of secrets and vulnerable dependencies
- Fix prompts for AI coding agents
- GitHub and Supabase connections
- MCP server and REST API
- Uptime and live threat monitoring
Good fit for
- →Teams shipping AI-generated prototypes
- →Developers auditing a vibe-coded app before launch
- Tags
- security
- vulnerability-scanning
- ai-code
- secrets-detection
- mcp
- devsecops
- github
CheckVibe: questions and answers
- What is CheckVibe used for?
- CheckVibe is a security scanner for teams shipping AI-written code that checks live apps, repos, dependencies, secrets and cloud, with fix prompts. It is a good fit for teams shipping AI-generated prototypes and developers auditing a vibe-coded app before launch.
- How much does CheckVibe cost?
- CheckVibe is a paid product with no free plan.
- Is CheckVibe open source?
- No. CheckVibe is proprietary (closed-source) software and can't be self-hosted. In the Security category, open-source options include Kubescape, Legitify and Trivy.
- What are some alternatives to CheckVibe?
- CheckVibe competes with AuditYourApp, Intruder and Invicti.
Open-source alternatives to CheckVibe
See all
Kubescape
Security
Kubescape is an open-source Kubernetes security platform for your IDE, CI/CD pipelines, an
Apache-2.0vs Wiz★ 12k
Legitify
Security
Detect and remediate misconfigurations and security risks across all your GitHub and GitLa
Apache-2.0★ 889
Trivy
Security
Find vulnerabilities, misconfigurations, secrets, SBOM in containers, Kubernetes, code rep
Apache-2.0vs Snyk★ 38k
Gitleaks
Security
Find secrets with Gitleaks 🔑
MITvs GitGuardian★ 30k
TruffleHog
Security
Find, verify, and analyze leaked credentials
AGPL-3.0vs GitGuardian★ 28k
Semgrep
Security
Lightweight static analysis for many languages. Find bug variants with patterns that look
LGPL-2.1vs Snyk★ 17k
SaaS alternatives to CheckVibe
See all
AuditYourApp
Security
Scans Supabase projects, websites and mobile apps for exposed RLS rules, open RPCs and leaked API keys
SaaS
Intruder
Security
Cloud-based vulnerability scanner for external attack surface
SaaS
Invicti
Security
Web application security scanning platform formerly known as Netsparker
SaaS
AttackerView
Security
Security auditor that shows what an attacker can see on your website
SaaSComplyeah
Security
External vulnerability scans and penetration tests for verified domains with control-mapped reports and certificates
SaaS
Pentera
Security
Automated penetration testing and security validation platform
SaaS