 TrackMedia
 TrackRev
About Invicti
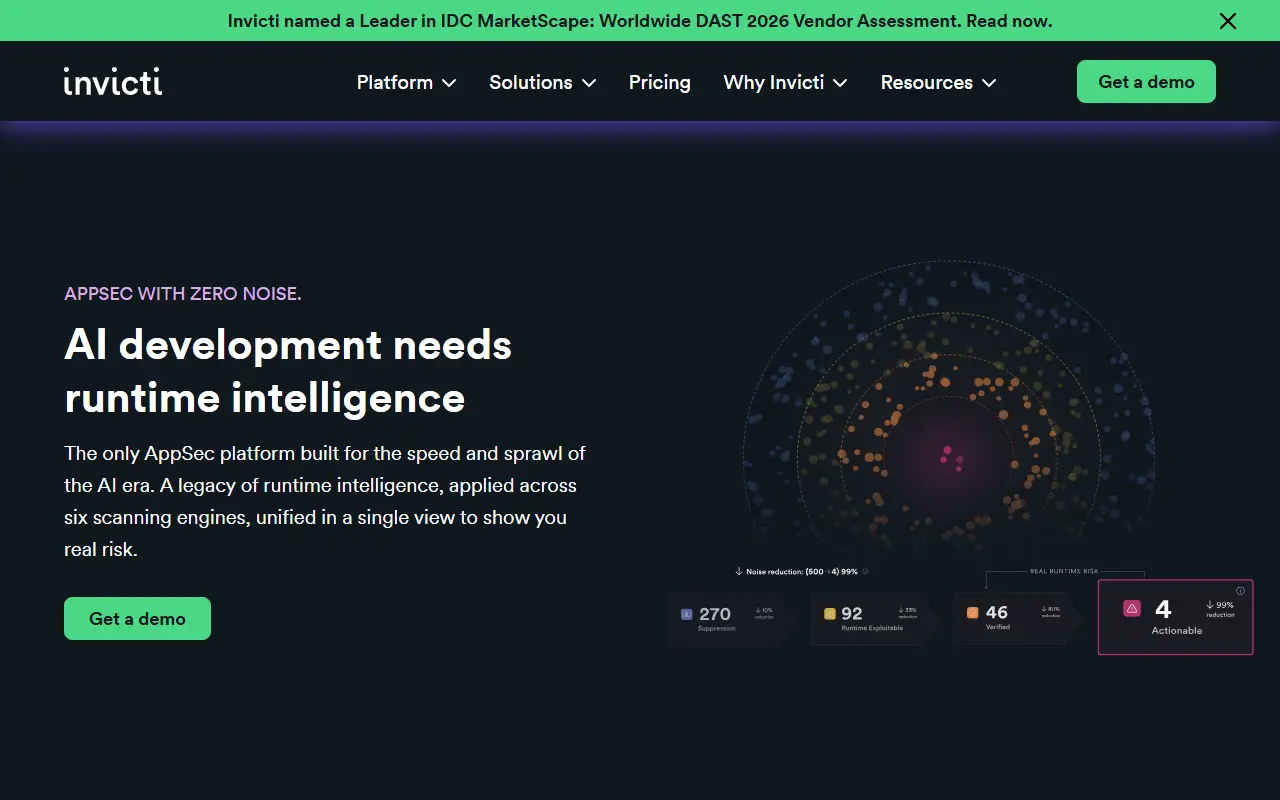
Invicti is an application security platform, formerly known as Netsparker, that tests websites, web applications and APIs for vulnerabilities. It describes itself as DAST-first, meaning it tests running applications the way an attacker would and tries to prove that findings are exploitable to reduce false alarms.
Around that core, the platform now includes scanning of code before runtime: static analysis, open source dependency analysis, SBOM and license risk tracking, secrets detection, infrastructure as code and container image checks. Runtime testing covers DAST and AI-assisted DAST, agentic pentesting, API security testing, attack surface management and cloud application security. A vulnerability management layer correlates findings from these tools and supports compliance and executive reporting.
Invicti is a commercial enterprise product with pricing and demo pages, plus resources such as documentation, a vulnerability database, training, a savings calculator and managed security provider and partner programs.
Key features
- Dynamic application security testing
- Exploitability proof for scanner findings
- API discovery and security testing
- Static analysis and open source dependency checks
- SBOM and license risk tracking
- Attack surface management
- Vulnerability correlation and compliance reporting
Good fit for
- Enterprise AppSec teams scanning thousands of web apps
- Developers verifying API security before release
- MSSPs offering web application testing
Invicti: questions and answers
- What is Invicti used for?
- Invicti, formerly Netsparker, is a web application security platform built around automated DAST scanning, with code, API and attack surface testing. It is a good fit for enterprise AppSec teams scanning thousands of web apps, developers verifying API security before release and MSSPs offering web application testing.
- How much does Invicti cost?
- Invicti is a paid product with no free plan. Platform packages (Web + API, AppSec Core, AppSec Flex) are quoted on request. The Agentic Pentest is listed at a maximum of $500 per pentest. Proof-of-concept licenses are offered.
- Is Invicti open source?
- No. Invicti is proprietary (closed-source) software. In the Security category, open-source options include OpenVAS, Nuclei and Semgrep.
- What are some alternatives to Invicti?
- Invicti competes with Veracode, Checkmarx and Rapid7.
Open-source alternatives to Invicti
See all
OpenVAS
Security
This repository contains the scanner component for Greenbone Community Edition.
GPL-2.0vs Tenable★ 4.9k
Nuclei
Security
Nuclei is a fast, customizable vulnerability scanner powered by the global security commun
MITvs Checkmarx★ 33k
Semgrep
Security
Lightweight static analysis for many languages. Find bug variants with patterns that look
LGPL-2.1vs Snyk★ 18k
Horusec
Security
Horusec is an open source tool that improves identification of vulnerabilities in your pro
Apache-2.0vs Checkmarx★ 1.3k
OpenBao
Security
OpenBao is a software solution to manage, store, and distribute sensitive data including s
MPL-2.0vs AWS Secrets Manager★ 9k
Infisical
Security
Infisical is the open-source platform for secrets, certificates, and privileged access man
OSSvs Doppler★ 30k
SaaS alternatives to Invicti
See all
Veracode
Security
Application security testing platform covering static, dynamic and software composition
SaaS
Checkmarx
Security
Application security testing platform with SAST, SCA and API security
SaaS
Rapid7
Security
Vulnerability management, SIEM and managed detection tools for security teams
SaaS
Tenable
Security
Vulnerability management and exposure assessment, maker of the Nessus scanner
SaaS
Snyk
Security
Developer security platform that scans code, dependencies, containers and IaC
SaaS
Intruder
Security
Cloud-based vulnerability scanner for external attack surface
SaaS