 TrackMedia
 TrackRev
About ShiftLeft
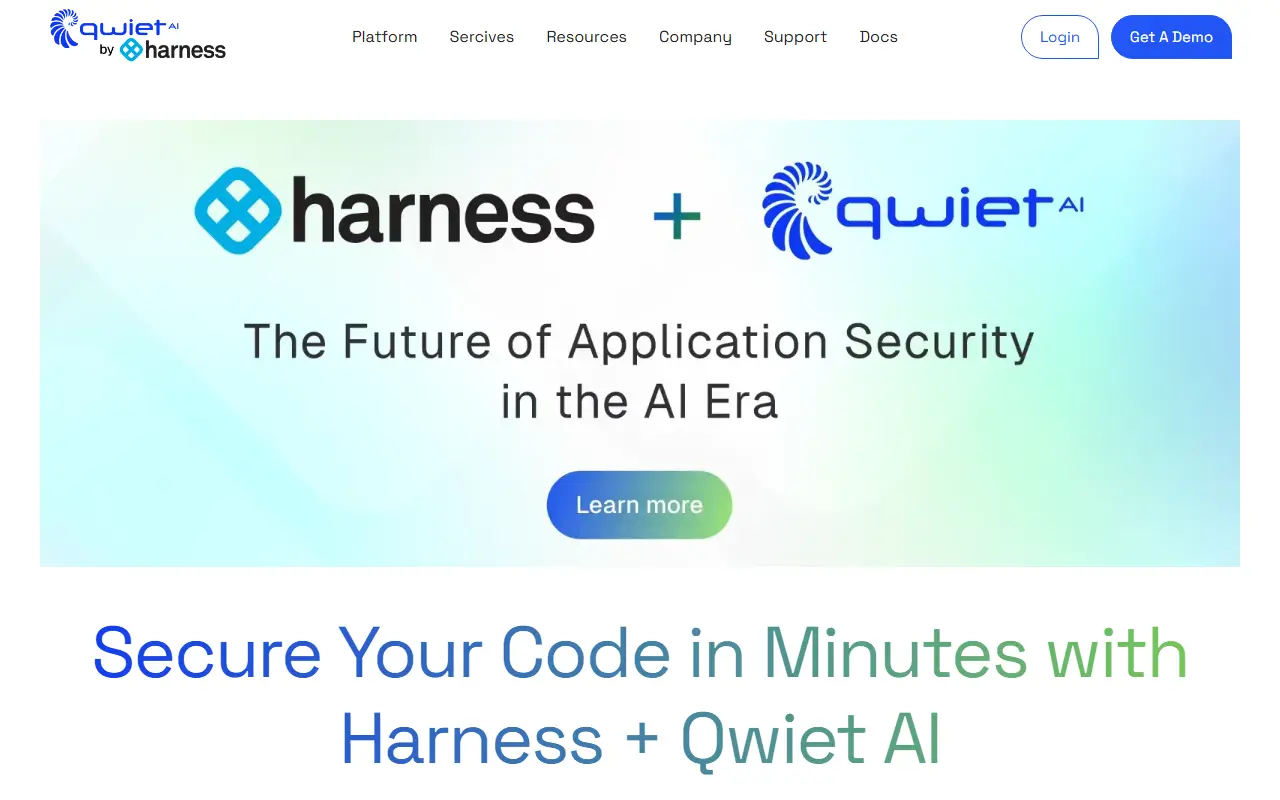
The ShiftLeft site now presents the product as Qwiet AI by Harness, application security testing that is part of the Harness platform. It aims to run one scan that covers SAST, SCA, IaC, container and secrets checks instead of separate tools, and shows the results in a single view.
To cut noise it filters findings by reachability and exploitability, showing which vulnerabilities can actually be reached and which are most at risk from active exploits. AI agents then propose code fixes, with an AI Autofix step that the site says resolves vulnerabilities in five minutes. The product is shown in both a web platform and an IDE.
The site states figures such as a 97% true positive rate and 10x faster scans, and quotes customer reviews from healthcare, retail, finance and services companies that mention CI/CD pipeline fit and scanning depth. Access is through a demo request.
Key features
- One scan covering SAST, SCA, IaC, containers and secrets
- Reachability and exploitability filtering of findings
- AI agents supply verified code fixes
- AI Autofix for resolving vulnerabilities
- Prioritizes by active exploit risk
- Designed to run inside pipelines
Good fit for
- Static code scanning in CI/CD
- Prioritizing exploitable vulnerabilities
- Automated fix suggestions
ShiftLeft: questions and answers
- What is ShiftLeft used for?
- ShiftLeft's application security scanning now appears as Qwiet AI by Harness, combining several scan types with reachability filtering and AI fixes. It is a good fit for static code scanning in CI/CD, prioritizing exploitable vulnerabilities and automated fix suggestions.
- Is ShiftLeft open source?
- No. ShiftLeft is proprietary (closed-source) software. In the Security category, open-source options include Semgrep, Horusec and Gitleaks.
- What are some alternatives to ShiftLeft?
- ShiftLeft competes with Checkmarx.
Open-source alternatives to ShiftLeft
See all
Semgrep
Security
Lightweight static analysis for many languages. Find bug variants with patterns that look
LGPL-2.1vs Snyk★ 18k
Horusec
Security
Horusec is an open source tool that improves identification of vulnerabilities in your pro
Apache-2.0vs Checkmarx★ 1.3k
Gitleaks
Security
Find secrets with Gitleaks 🔑
MITvs GitGuardian★ 31k
Trivy
Security
Find vulnerabilities, misconfigurations, secrets, SBOM in containers, Kubernetes, code rep
Apache-2.0vs Snyk★ 39k
TruffleHog
Security
Find, verify, and analyze leaked credentials
AGPL-3.0vs GitGuardian★ 29k
DefectDojo
Security
Open-Source Unified Vulnerability Management, DevSecOps & ASPM
BSD-3-Clausevs Tenable★ 5.2k
SaaS alternatives to ShiftLeft
See all
Checkmarx
Security
Application security testing platform with SAST, SCA and API security
SaaS
Aikido Security
Security
All-in-one application security platform for code, cloud and runtime scanning
SaaS
Mend
Security
Application security platform for software composition analysis and code scanning
SaaS
Snyk
Security
Developer security platform that scans code, dependencies, containers and IaC
SaaS
Veracode
Security
Application security testing platform covering static, dynamic and software composition
SaaS
Black Duck
Security
Software composition analysis and application security testing products
SaaS