7 open-source alternatives ranked by real activity

Open-source StrongDM alternatives

A curated, ranked list of the 7 best open-source alternatives to StrongDM.

The best open-source alternative to StrongDM is Infisical. If that doesn't suit you, other good options are Netmaker, Firezone, Octelium and Pomerium.

Commercial alternatives to StrongDM include CyberArk, BeyondTrust, Teleport and Delinea Secret Server. See all 13.

StrongDM alternatives are mainly networking & VPN tools, but some are also security tools. 7 of them shipped code in the last 30 days, 7 can be self-hosted, and 4 use a permissive licence.

Last updated November 13, 2026 · ranked by GitHub stars, growth and recent commits

Infisical

Infisical is an open-source platform for managing secrets, certificates and privileged access, with syncing, rotation and leak prevention.

GitHub stars
30k
Last commit
yesterday
Latest release
v0.167.8
Self-hosted
Yes
Hosted version
Available
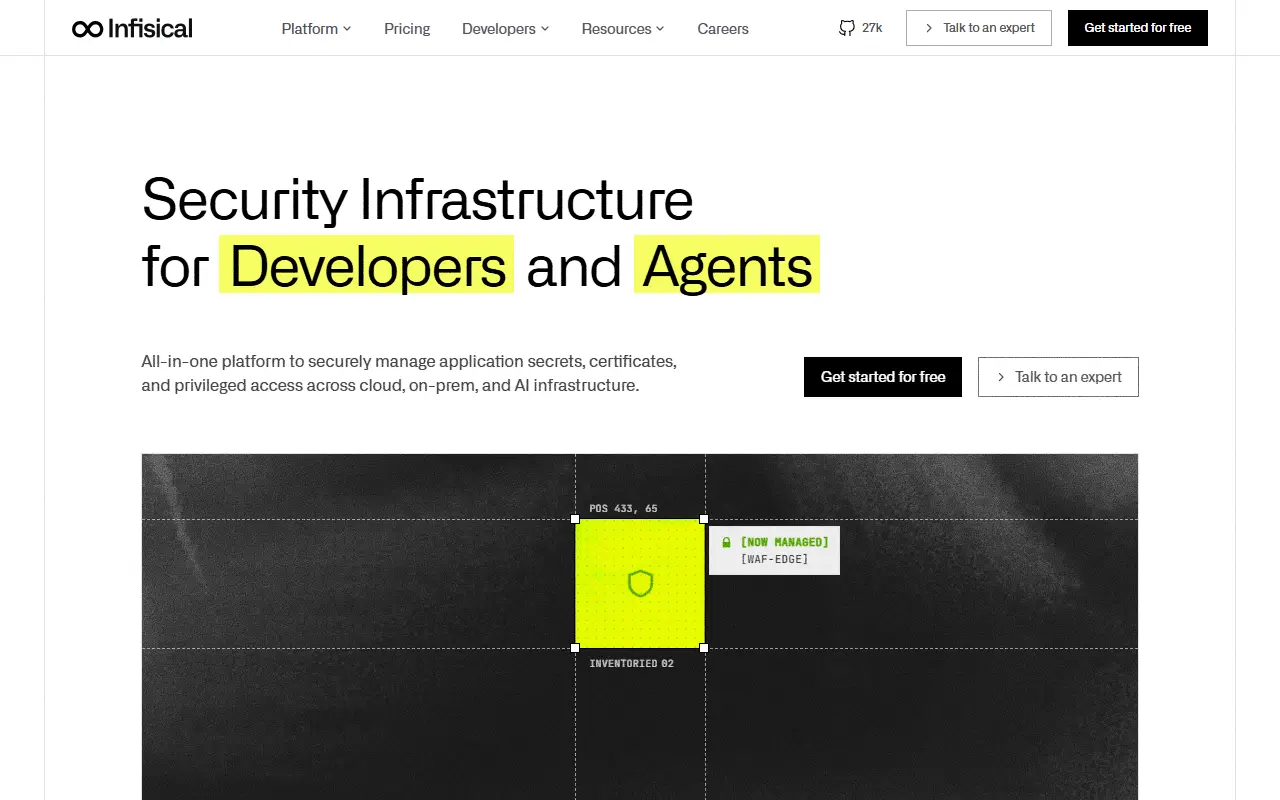
infisical.comInfisical homepage screenshot

Infisical is an open-source security infrastructure platform used by teams to manage application secrets, certificates and privileged access. It centralizes secrets and configuration across environments, with versioning, rotation and leak prevention. The stack is TypeScript and Go on PostgreSQL, and the project offers both a hosted Infisical Cloud and a self-hosting option.

Secrets are organized by project and environment, such as development and production, in a dashboard. Secret syncs push values to platforms like GitHub, Vercel and AWS and work with tools such as Terraform and Ansible. Further features include point-in-time recovery, scheduled rotation for databases and AWS IAM, ephemeral dynamic secrets, secret scanning that stops leaks into git, a Kubernetes operator, and an agent that injects secrets without code changes. It also offers honey tokens as decoy credentials and brokered access for AI agents. The repository metadata lists the license as Other, so check it for exact terms.

Key features

  • Secrets dashboard across projects and environments
  • Secret syncs to GitHub, Vercel and AWS
  • Versioning with point-in-time recovery
  • Automatic secret rotation and dynamic secrets
  • Secret scanning to prevent leaks into git
  • Kubernetes operator and injection agent

Pricing: Free for up to 5 identities. Pro is $23 and Advanced $46 per identity per month, or $20 and $40 billed annually; Enterprise is custom. Paid plans include a free trial.
Netmaker

A platform that automates WireGuard networks for mesh VPNs, remote access and site-to-site links, available as open-source self-hosted software or a managed SaaS.

GitHub stars
12k
Last commit
yesterday
Latest release
v1.7.0
Self-hosted
Yes
Hosted version
Available
netmaker.ioNetmaker homepage screenshot

Netmaker builds on WireGuard to create and manage virtual networks automatically, from a home lab to an enterprise. It markets itself as a zero trust networking platform for connecting devices, clouds and sites, with an admin UI so that networks do not have to be configured by hand with wg-quick files.

Its capabilities include WireGuard networks, mesh VPNs, remote access gateways, site-to-site connectivity, private DNS, access control lists and OAuth sign-in. Clients are available for Linux, Mac and Windows, and the server can be deployed with Docker or on Kubernetes. The topics also mention IPv6 support and overlay networking.

You can deploy the open-source server yourself, for example on an Ubuntu 24.04 cloud VM with a static public IP, using a quick-start script and opening the documented ports, or install the self-hosted Pro version. A managed Netmaker SaaS is also offered for those who want to skip operations. The repository lists the license as Other.

Key features

  • Automated WireGuard network management
  • Mesh VPNs and site-to-site links
  • Remote access gateways
  • Admin UI for network administration
  • Access control lists and private DNS
  • OAuth login support
  • Clients for Linux, Mac and Windows

Pricing: The open-source edition is free to self-host. Team starts at $2 and Business at $4 per active connection per month, with a 7-day trial; a self-hosted Professional tier is $99 per month and Enterprise is custom.

Firezone

Firezone is a zero trust access platform based on WireGuard, released as open source, that replaces traditional VPNs with policy-based access to apps and networks.

GitHub stars
9.2k
Last commit
yesterday
Latest release
headless-client-1.5.16
Licence
Apache-2.0
Hosted version
Available
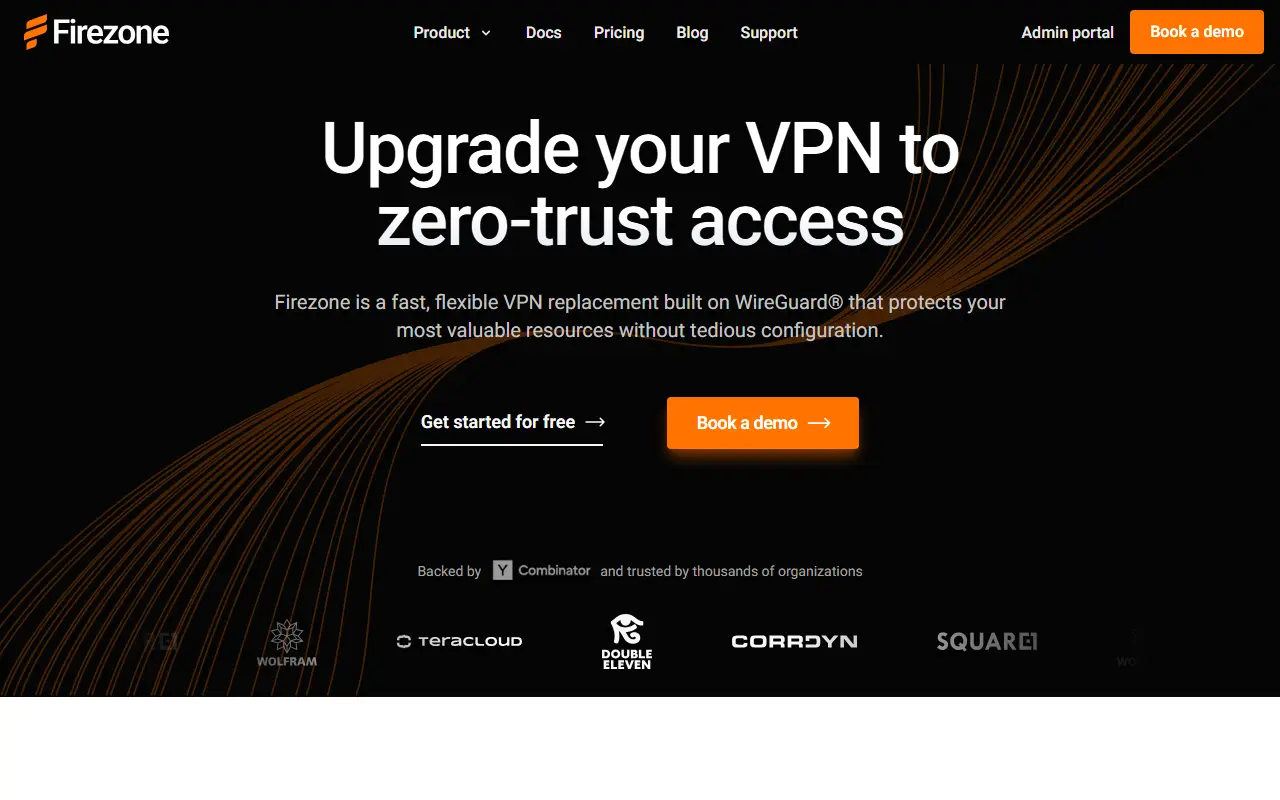
firezone.devFirezone homepage screenshot

Firezone is a zero trust access platform that uses WireGuard and is published as open source. It is positioned as a replacement for a traditional VPN, connecting users to internal apps, services and networks through access policies rather than broad network-level rules.

Administrators define policies for resources and can restrict access by conditions such as device location and time of day, with every authorized connection visible by user, resource or policy. Users and groups sync from an identity provider, which simplifies onboarding and offboarding. Lightweight Gateways run as Linux binaries wherever access is needed, and using two or more Gateways gives automatic load balancing and failover. Hole-punching keeps protected resources hidden from the public internet.

Client apps are available for macOS, Windows, Linux, Android, ChromeOS and iOS. The codebase is licensed under Apache-2.0 and written largely in Elixir, with Rust used for networking components. The vendor offers a hosted admin portal, a free way to get started and a separate pricing page.

Key features

  • WireGuard-based VPN replacement
  • Access policies per resource and group
  • Identity provider directory sync
  • Conditional access by location and time
  • Gateways with load balancing and failover
  • Clients for desktop and mobile platforms

Pricing: Free Starter plan for up to 6 users. Team costs $5 per user per month, or $4.16 billed annually; Enterprise is quoted via sales. Source code can be self-hosted without vendor support.

Octelium

Octelium is a self-hosted zero trust access platform that can act as a VPN, ZTNA system, API and AI gateway, tunnel service or PaaS on Kubernetes.

GitHub stars
4.2k
Last commit
today
Latest release
v0.50.0
Licence
AGPL-3.0
Self-hosted
Yes
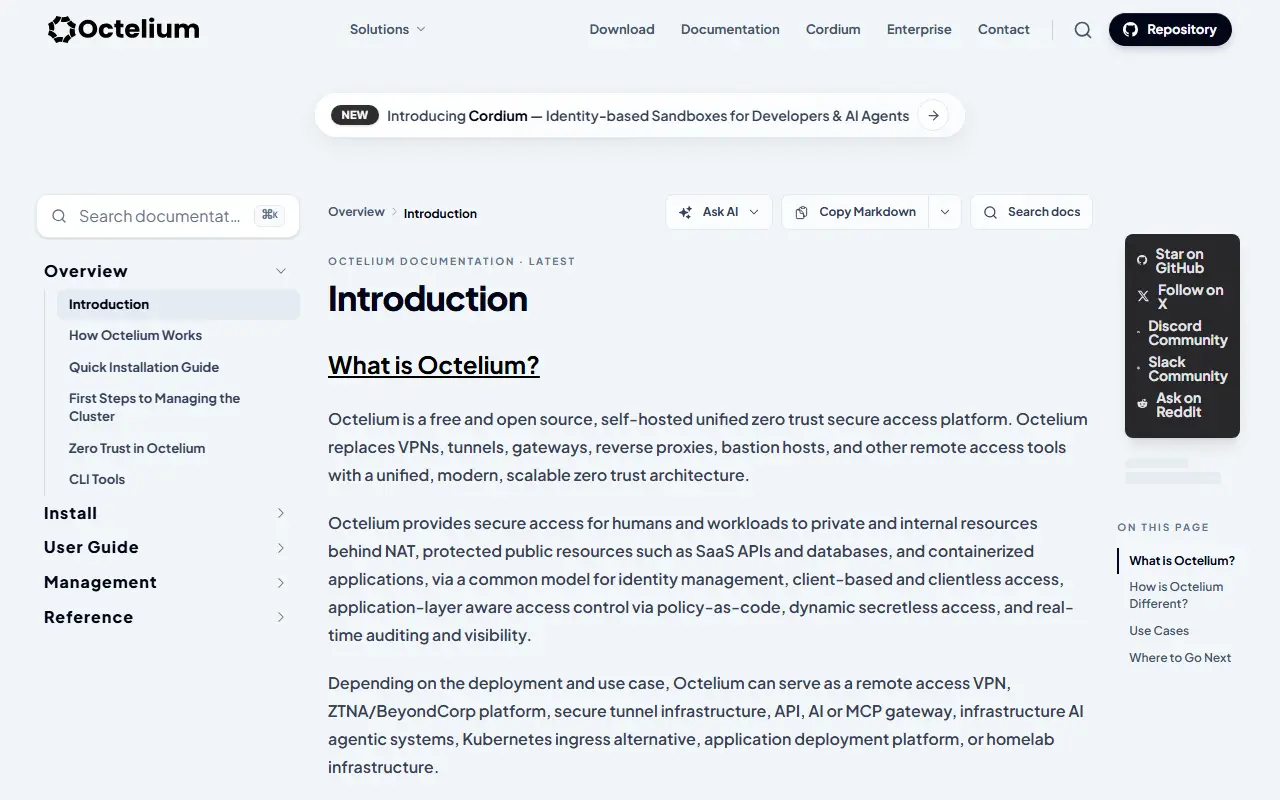
octelium.comOctelium homepage screenshot

Octelium is a self-hosted, open-source platform that unifies zero trust secure access under one system. It is flexible enough to act as a zero-config remote access VPN, a Zero Trust Network Access and BeyondCorp-style platform, an alternative to ngrok and Cloudflare Tunnel, an API gateway, an AI and LLM gateway, and an infrastructure for building MCP gateways and AI agent access.

Repository topics list attribute-based access control, policy as code, WireGuard, QUIC, SSO, multi-factor authentication, OpenTelemetry and SSH access. The README includes use cases, a feature overview, a guide to try it in a Codespace, CLI installation and instructions to install your first cluster. It is written in Go and runs on Kubernetes. It is compared to ngrok, Cloudflare Tunnel and Apigee for different roles.

Octelium is licensed under AGPL-3.0 and you operate the cluster yourself. It suits platform and security teams, homelab users and developers who want to replace several access, tunnel and gateway tools with one self-hosted system.

Key features

  • Zero-config remote access VPN
  • ZTNA and BeyondCorp-style access
  • API, AI and MCP gateway capabilities
  • Tunnel service as ngrok alternative
  • Attribute-based policy as code
  • Runs on Kubernetes clusters

Pricing: Free and open source under AGPL-3.0.

Pomerium

An identity and context-aware access proxy written in Go that secures internal apps and services without a corporate VPN.

GitHub stars
5.1k
Last commit
yesterday
Latest release
v0.34.1
Licence
Apache-2.0
Self-hosted
Yes
Hosted version
Available
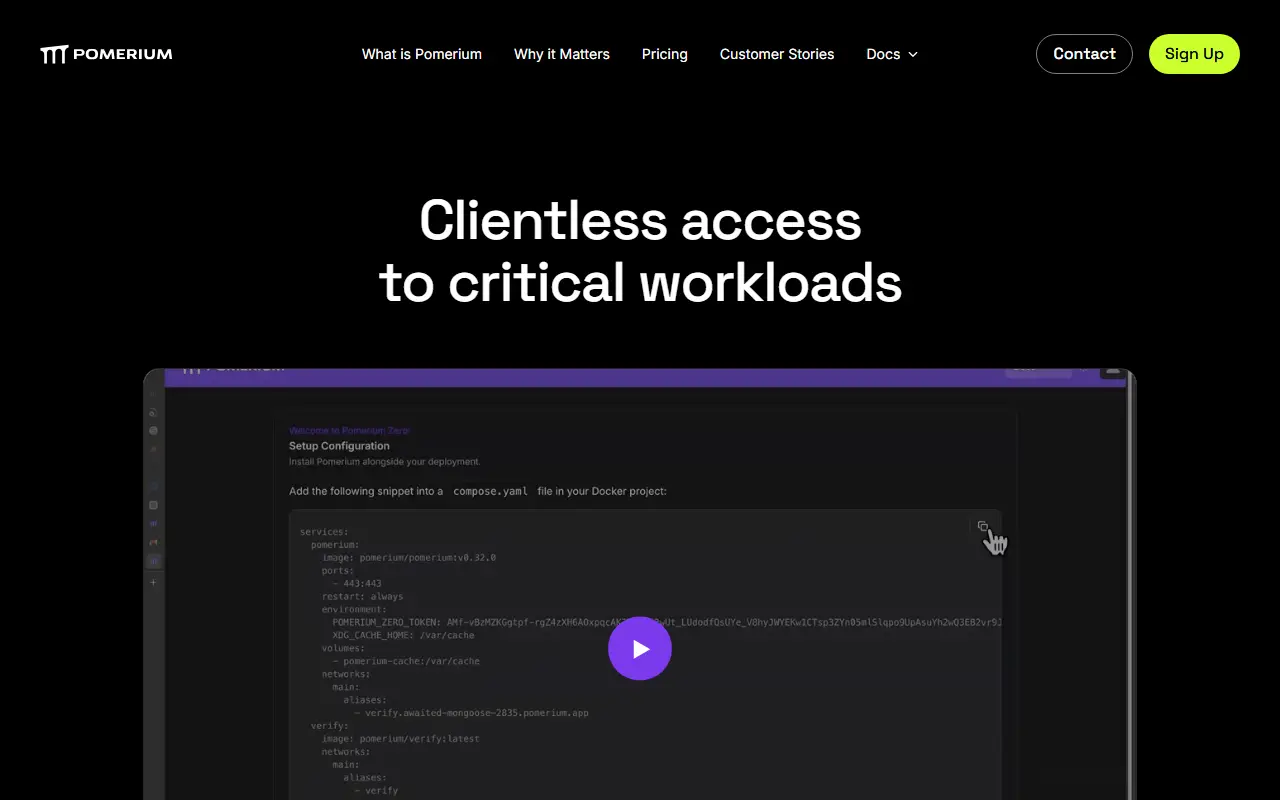
pomerium.comPomerium homepage screenshot

Pomerium is an identity and context-aware reverse proxy that makes secure, clientless connections to internal web apps and other services. The goal is to protect internal resources without asking users to connect through a corporate VPN.

According to the project, clientless access makes it easier to adopt, running tunnel-free and close to your apps and services makes it faster, and verifying each action before it executes makes it safer. Context-aware policies can draw on data from several sources, so access decisions can reflect your organization's own needs. Repository topics point to zero-trust, BeyondCorp-style, identity-aware proxy and IAM use cases.

Pomerium is written in Go and licensed under Apache-2.0. Teams that want a hosted control plane and a management GUI can look at Pomerium Zero, while the open-source proxy can be run on your own infrastructure. Documentation and tutorials are available on pomerium.com.

Key features

  • Identity-aware reverse proxy
  • Clientless access to internal apps
  • Per-request verification of every action
  • Context-aware access policies
  • Tunnel-free deployment near your services
  • Hosted control plane via Pomerium Zero

Pricing: Free Personal plan. Business costs $7 per user per month billed annually, with a free trial; Enterprise for fully self-hosted deployments is quoted.

OpenZiti

An open source zero-trust networking platform that makes services invisible to unauthorized users using cryptographic identity and end-to-end encryption.

GitHub stars
4.5k
Last commit
2 days ago
Latest release
v2.0.8
Licence
Apache-2.0
Self-hosted
Yes
Hosted version
Available

OpenZiti is an open-source zero-trust networking platform. Every connection, whether from a user, service, device or workload, is authenticated with cryptographic identity, authorized by policy and encrypted end-to-end. Its stated goal is to make network services invisible to unauthorized users.

It works with existing applications through lightweight tunnelers that need no code changes, and with new applications through embedded SDKs for what it calls the strongest zero-trust model. A Python SDK is published on PyPI, where it can turn a web server into a zero-trust embedded application with a few lines of code.

The README lists use cases that include replacing VPNs, keeping APIs dark with no listening ports, giving IoT devices unique identities, linking workloads across clouds and Kubernetes clusters, and reaching self-hosted services such as Nextcloud or Home Assistant without open router ports. It was created and sponsored by NetFoundry, is Apache 2.0 licensed, and has a managed solution.

Key features

  • Every connection is authenticated, authorized and encrypted
  • Tunnelers secure existing apps without code changes
  • Embedded SDKs for new applications
  • Each service individually authorized instead of VPN access
  • Dark services with no listening ports
  • Python SDK distributed through PyPI
  • One overlay across clouds, on-prem and edge

Apache Guacamole

The server-side components of Apache Guacamole, a clientless remote desktop gateway that provides VNC, RDP and SSH access through a web browser.

GitHub stars
4k
Last commit
10 days ago
Licence
Apache-2.0
Self-hosted
Yes
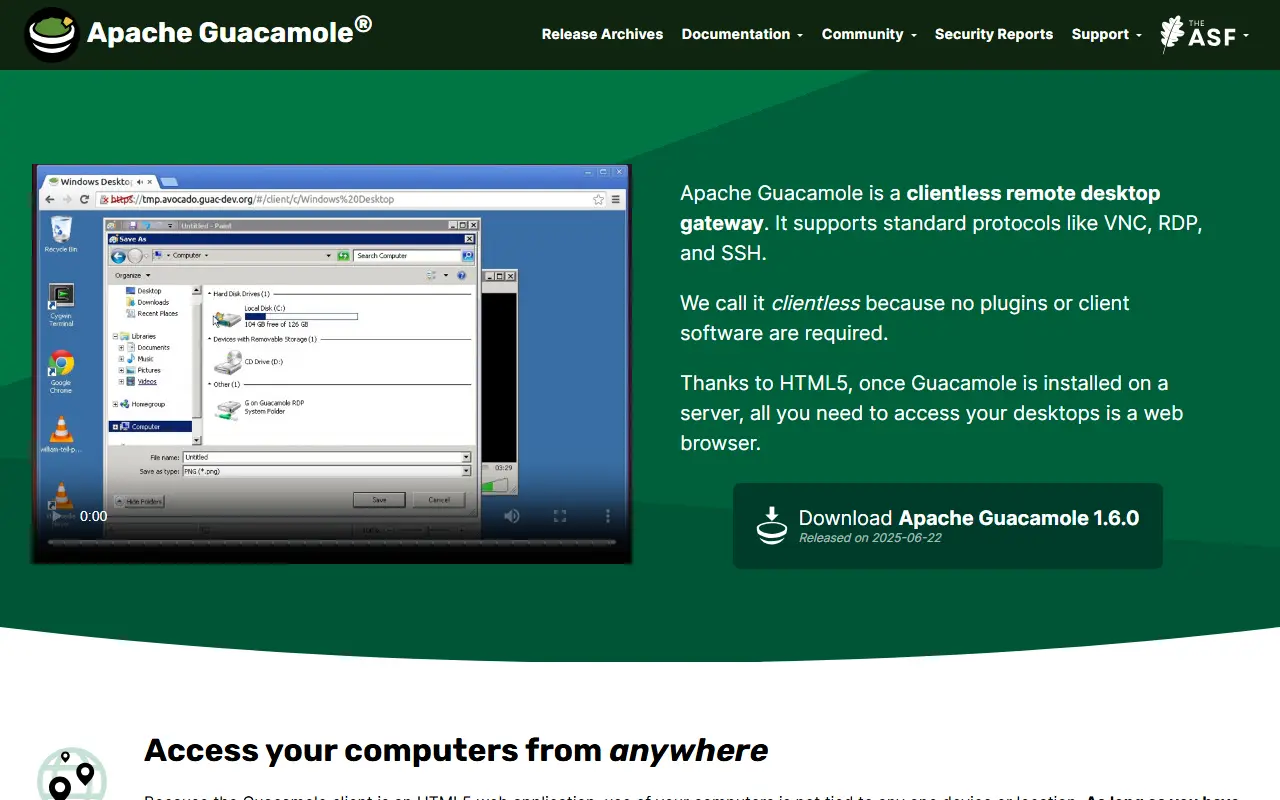
guacamole.apache.orgApache Guacamole homepage screenshot

This repository holds the server-side parts of Apache Guacamole: the guacd proxy daemon, the libguac C API and protocol support. Guacamole itself is a clientless remote desktop gateway that supports standard protocols such as VNC, RDP and SSH.

It is called clientless because no plugins or client software are needed. Once Guacamole is installed on a server, a web browser is all that is required to reach your desktops, since the client is an HTML5 web application. That frees access from any one device or location, and the desktops can even be virtual machines hosted in the cloud.

Guacamole is built on its own documented stack of core APIs, with tutorials and conceptual overviews in the online manual. It is a project of the Apache Software Foundation, licensed under Apache-2.0, and the codebase combines C, Java and JavaScript. The project provides release archives, mailing lists, an issue tracker and commercial support options.

Key features

  • Clientless remote desktop gateway
  • VNC, RDP and SSH protocol support
  • HTML5 browser client
  • guacd proxy daemon
  • libguac C API
  • Documented core APIs

Pricing: Free and open source under the Apache-2.0 licence.

Commercial StrongDM alternatives

Hosted, closed-source products that compete with StrongDM. Showing 12 of 13.

See every StrongDM alternative on its tool page

StrongDM alternatives: questions

What is the best open-source alternative to StrongDM?
Infisical is the top-ranked open-source alternative to StrongDM on Enlisted: Infisical is an open-source platform for managing secrets, certificates and privileged access, with syncing, rotation and leak prevention. Other strong options are Netmaker, Firezone, Octelium and Pomerium.
What are the best commercial alternatives to StrongDM?
CyberArk, BeyondTrust, Teleport, Delinea Secret Server and Google Memorystore are among the hosted, closed-source alternatives to StrongDM listed on Enlisted, which lists 13 in total. Compare their pricing and features on each tool page.
Are these StrongDM alternatives free?
All 7 are open source, so the code is free to use under its licence, and all of them can be self-hosted on your own server or computer. 5 also offer a paid or managed cloud version if you'd rather not host it yourself.
How is this list of StrongDM alternatives ranked?
By a score built from GitHub stars, star growth over the last 30 days and how recently the code changed. 7 of these projects shipped code in the last 30 days. Data is refreshed daily, and nobody can pay to move up.

People also look for alternatives to…

View all