 TrackMedia
 TrackRev
About External Secrets
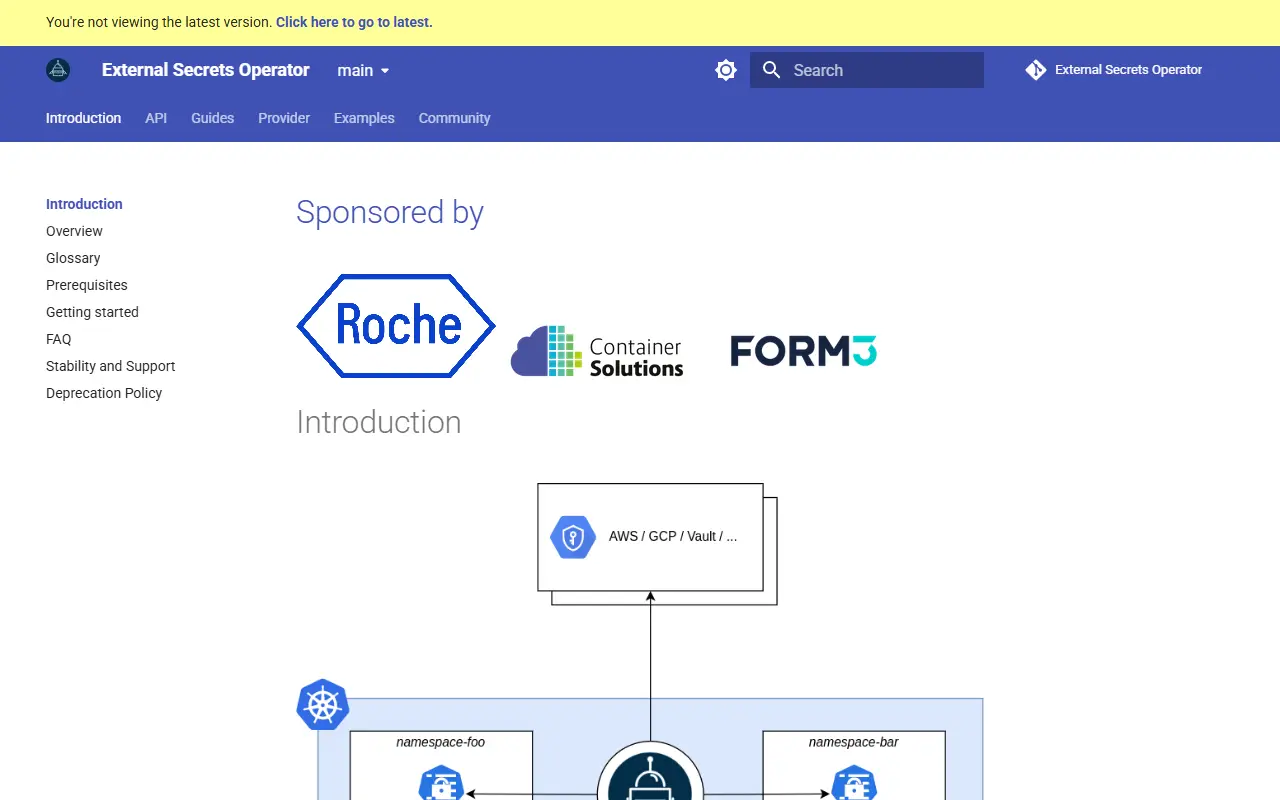
External Secrets Operator (ESO) is a Kubernetes operator that connects external secret management systems to a cluster. It reads from the external API and injects the values into a Kubernetes Secret automatically, so applications keep using ordinary Secret objects.
The stated goal is to synchronise secrets from external APIs into Kubernetes. To do that, ESO adds custom API resources: ExternalSecret, SecretStore and ClusterSecretStore, which wrap the external API and manage the lifecycle of the secrets. The documentation also lists ClusterExternalSecret, PushSecret and ClusterPushSecret resources, plus generators for things like container registry credentials and passwords.
The provider list is long. It names AWS Secrets Manager, Parameter Store, Azure Key Vault, Google Cloud Secret Manager, HashiCorp Vault, IBM Secrets Manager, Akeyless, 1Password, Doppler, Bitwarden Secrets Manager, Infisical, OpenBao and many more. Guides cover templating, multi-tenancy, security best practices and a threat model, and the licence is Apache-2.0.
Key features
- Integrates external secret managers with Kubernetes
- Injects external values into Kubernetes Secrets
- Syncs secrets from external APIs into Kubernetes
- Custom resources for ExternalSecret, SecretStore and ClusterSecretStore
- Many providers including AWS, Azure, Google, Vault and IBM
Good fit for
- Syncing cloud secret manager values into a cluster
- Pushing Kubernetes secrets out to a provider
- Multi-tenant secret access in shared clusters
External Secrets: questions and answers
- What is External Secrets used for?
- External Secrets is a Kubernetes operator that syncs secrets from external managers such as AWS Secrets Manager and HashiCorp Vault into native Kubernetes Secrets. It is a good fit for syncing cloud secret manager values into a cluster, pushing Kubernetes secrets out to a provider and multi-tenant secret access in shared clusters.
- Is External Secrets open source?
- Yes. External Secrets is open source under the Apache-2.0 licence. Its source code is on GitHub at external-secrets/external-secrets and is written mainly in Go.
- Is External Secrets free?
- Yes. External Secrets is open source, so the software itself is free to use.
- Can I self-host External Secrets?
- Yes. External Secrets can be self-hosted on your own server or infrastructure.
- What is External Secrets an alternative to?
- External Secrets is an open-source alternative to Google Secret Manager, Akeyless and AWS Secrets Manager. Other open-source alternatives to Google Secret Manager include Bitwarden, Conjur and OpenBao.
- Is External Secrets actively maintained?
- Yes. The most recent commit to External Secrets was on 11 November 2026. The project has 6.9k stars on GitHub, with 49 added in the last 30 days.
Open-source alternatives to External Secrets
See all
Bitwarden
Password Management
Bitwarden infrastructure/backend (API, database, Docker, etc).
OSSvs 1Password★ 21k
Conjur
Password Management
CyberArk Conjur automatically secures secrets used by privileged users and machine identit
OSSvs CyberArk★ 956
OpenBao
Security
OpenBao is a software solution to manage, store, and distribute sensitive data including s
MPL-2.0vs AWS Secrets Manager★ 9k
Infisical
Security
Infisical is the open-source platform for secrets, certificates, and privileged access man
OSSvs Doppler★ 30kVaultwarden
Password Management
Unofficial Bitwarden compatible server written in Rust, formerly known as bitwarden_rs
AGPL-3.0vs 1Password★ 71k
Kubernetes
Infrastructure & Containers
Production-Grade Container Scheduling and Management
Apache-2.0vs Amazon EKS★ 129k
SaaS alternatives to External Secrets
See all
Google Secret Manager
Security
Google Cloud service for storing and versioning API keys, passwords and certificates
SaaS
Akeyless
Security
SaaS secrets management and machine identity platform for apps and pipelines
SaaS
AWS Secrets Manager
Security
Managed service to store, rotate and retrieve database credentials and API keys
SaaS
ManageEngine Password Manager Pro
Password Management
Privileged password vault with session recording and password rotation for IT teams
SaaS
LastPass
Password Management
Password manager with autofill, vault sharing and admin controls
SaaS
Norton Password Manager
Password Management
Password manager from Norton with autofill, a password generator and synced vault
SaaS