8 open-source alternatives ranked by real activity

Open-source heylogin alternatives

A curated, ranked list of the 8 best open-source alternatives to heylogin.

The best open-source alternative to heylogin is Vaultwarden. If that doesn't suit you, other good options are Keycloak, Bitwarden, step-ca and Passbolt.

Commercial alternatives to heylogin include 1Password, Proton Pass, LastPass and Teleport. See all 15.

heylogin alternatives are mainly password managers, but some are also auth & identity tools and security tools. 7 of them shipped code in the last 30 days, 8 can be self-hosted, and 4 use a permissive licence.

Last updated November 13, 2026 · ranked by GitHub stars, growth and recent commits

Vaultwarden

Vaultwarden is an AGPL-3.0 server written in Rust that implements the Bitwarden client API for self-hosted password vaults.

GitHub stars
71k
Last commit
yesterday
Latest release
1.37.5
Licence
AGPL-3.0
Self-hosted
Yes

Vaultwarden is an alternative server for the Bitwarden Client API, written in Rust and compatible with the official Bitwarden clients. The README positions it for self-hosting where running the official, more resource-heavy service may not suit. It is unofficial and not associated with Bitwarden, and bug reports go to its own maintainers rather than Bitwarden support.

The listed coverage is nearly the whole client API: personal vault, Send, attachments, website icons, a personal API key, organizations with collections, sharing, roles, groups, event logs, policies and the Directory Connector, plus several two-factor methods (authenticator, email, FIDO2 WebAuthn, YubiKey and Duo) and emergency access. An admin backend and a modified web vault are bundled.

The recommended install is the container image from ghcr.io, docker.io or quay.io, run with Docker, Podman or Docker Compose with a data volume mounted for persistence. The web vault needs HTTPS for the Web Crypto API, so a reverse proxy is suggested. Community packages exist, and you can build it yourself.

Key features

  • Personal vault, Send, attachments and website icons
  • Organizations with collections, groups and policies
  • Several two-factor options including FIDO2 and YubiKey
  • Emergency access and an admin backend
  • Works with the official Bitwarden clients
  • Container images on ghcr.io, docker.io and quay.io
  • Run with Docker, Podman or Docker Compose
Read more about VaultwardenGitHub#1 heylogin alternative

Keycloak

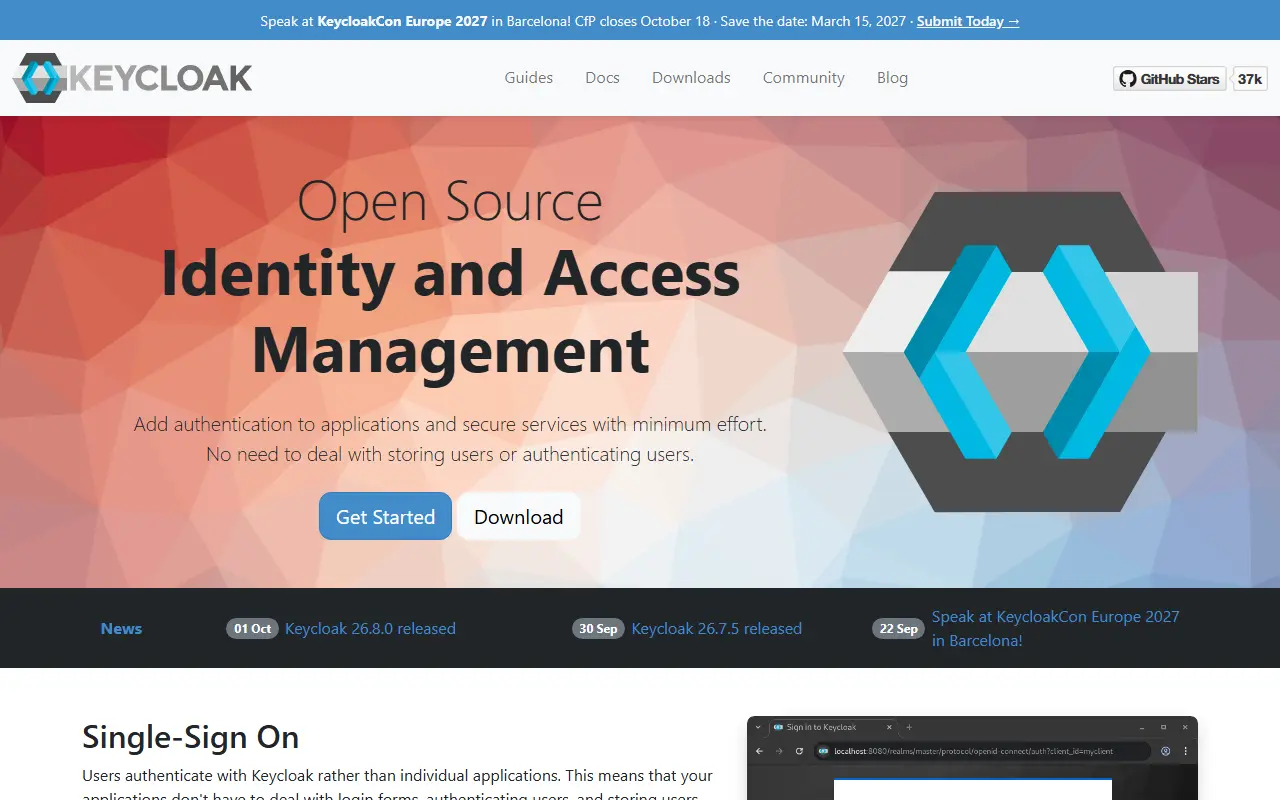
Keycloak is an open-source identity and access management server that adds single sign-on, user management and authorization to applications.

GitHub stars
38k
Last commit
yesterday
Latest release
26.8.2
Licence
Apache-2.0
Self-hosted
Yes
keycloak.orgKeycloak homepage screenshot

Keycloak is an open-source identity and access management server. It lets application teams add authentication and secure services without building their own login system, since Keycloak handles storing users and authenticating them. The project is written in Java, released under the Apache-2.0 license and governed under the Cloud Native Computing Foundation code of conduct.

Keycloak supports standard protocols such as OpenID Connect and SAML, and offers user federation, strong authentication, user management and fine-grained authorization. You can run it from the downloadable distribution using a start-dev command, or use the official Docker image published on Quay for containers and Kubernetes setups. The project provides documentation, a user mailing list and community channels for help, along with guidance for building and testing from source.

Key features

  • Single sign-on with OpenID Connect and SAML
  • User federation with external directories
  • Strong and multi-step authentication options
  • Central user and account management
  • Fine-grained authorization policies
  • Docker image and standalone distribution

Pricing: Free and open source under the Apache-2.0 license; you host and operate it yourself.

Bitwarden

This is the Bitwarden server: the API, database and Docker-based infrastructure behind the Bitwarden password manager's client apps.

GitHub stars
21k
Last commit
yesterday
Latest release
v2026.10.1
Self-hosted
Yes
Hosted version
Available
bitwarden.comBitwarden homepage screenshot

Bitwarden is a password manager, and this repository contains its server side: the APIs, database and other core infrastructure that all Bitwarden client applications connect to. The code is written in C# on .NET Core with ASP.NET Core, and the database layer is written in T-SQL for SQL Server.

The server can be developed, built, run and deployed on Windows, macOS and Linux. For deployment, the project provides Docker containers along with PowerShell and Bash scripts that bootstrap an installation, and the images are published on GitHub Container Registry. The services include Admin, API, Billing, Events, Identity, Notifications, SCIM and SSO components.

Organizations that want to keep their vaults on their own infrastructure can follow the on-premise install guide in the Bitwarden help center, which requires Docker and Docker Compose. Bitwarden also runs managed cloud clusters in the US and EU. The repository lists its license as 'Other', so check the license files for the exact terms.

Key features

  • APIs used by all Bitwarden client apps
  • Identity, SCIM and SSO services
  • SQL Server database layer
  • Docker-based on-premise deployment
  • Install scripts for Windows, macOS and Linux
  • Admin and event processing services

Pricing: A free personal plan exists. Premium is $1.65 a month, Families $3.99 a month for six users, Teams $4 and Enterprise $6 per user per month, all billed annually.

step-ca

step-ca from Smallstep is an open-source private certificate authority and ACME server that issues X.509 and SSH certificates for automated DevOps workflows.

GitHub stars
9.1k
Last commit
3 days ago
Latest release
v0.30.2
Licence
Apache-2.0
Self-hosted
Yes
smallstep.comstep-ca homepage screenshot

step-ca, published as smallstep/certificates, is an online private certificate authority built for automated certificate management in DevOps environments. It is the server counterpart to the step command-line tool, and both are maintained by Smallstep Labs.

It can issue HTTPS server and client certificates trusted by browsers, as well as TLS certificates for virtual machines, containers, APIs, database connections and Kubernetes pods. It also issues SSH certificates: users can obtain them with single sign-on tokens, and hosts can obtain them using cloud instance identity documents. As an ACME server it supports the popular challenge types, and a Go wrapper and the step CLI help with scripting.

step-ca is written in Go and released under Apache-2.0. It is tuned for a two-tier PKI, and the README points teams that need multiple authorities, active revocation through CRL or OCSP, device attestation or a web admin UI to Smallstep's separate commercial product.

Key features

  • Private certificate authority for X.509
  • SSH certificates for users and hosts
  • ACME server with common challenge types
  • TLS certificates for containers and Kubernetes pods
  • Single sign-on token exchange for SSH access
  • Go wrapper and step CLI automation

Pricing: Open source under Apache-2.0; Smallstep also sells a separate commercial CA product with additional features.

Passbolt

Passbolt is an open-source, security-focused password manager for teams, with end-to-end encryption and options to self-host or use vendor cloud.

GitHub stars
6.2k
Last commit
yesterday
Latest release
v5.18.0
Licence
AGPL-3.0
Self-hosted
Yes
Hosted version
Available
passbolt.comPassbolt homepage screenshot

Passbolt is an open-source password manager built for teams. It lets organizations gather, structure and share passwords and other secrets, and its security model relies on secret keys owned by each user together with end-to-end encryption. The vendor says the product is audited several times a year and that the findings are made public.

The repository holds the JSON API of the Community Edition, written in PHP on CakePHP. Users work through clients: browser extensions, mobile apps, a command-line tool and a desktop app. Teams can share credentials and audit access, with policies aimed at power users. The README includes guidance for running the server natively on your own machine.

Passbolt Community Edition is licensed under AGPL-3.0. The vendor also offers paid Pro and cloud-hosted options, which suit organizations that prefer managed hosting or extra features. It fits teams, from small startups to larger IT departments, that want shared credential management they can host and inspect themselves.

Key features

  • End-to-end encrypted password sharing
  • User-owned secret keys
  • Browser extensions and mobile apps
  • CLI and desktop clients
  • Credential audit and access policies
  • Self-hosted Community Edition API

Pricing: Free Community Edition with unlimited users. Pro costs $4.9 per user per month billed annually with a 10-user minimum; Enterprise is quoted.

Pomerium

An identity and context-aware access proxy written in Go that secures internal apps and services without a corporate VPN.

GitHub stars
5.1k
Last commit
yesterday
Latest release
v0.34.1
Licence
Apache-2.0
Self-hosted
Yes
Hosted version
Available
pomerium.comPomerium homepage screenshot

Pomerium is an identity and context-aware reverse proxy that makes secure, clientless connections to internal web apps and other services. The goal is to protect internal resources without asking users to connect through a corporate VPN.

According to the project, clientless access makes it easier to adopt, running tunnel-free and close to your apps and services makes it faster, and verifying each action before it executes makes it safer. Context-aware policies can draw on data from several sources, so access decisions can reflect your organization's own needs. Repository topics point to zero-trust, BeyondCorp-style, identity-aware proxy and IAM use cases.

Pomerium is written in Go and licensed under Apache-2.0. Teams that want a hosted control plane and a management GUI can look at Pomerium Zero, while the open-source proxy can be run on your own infrastructure. Documentation and tutorials are available on pomerium.com.

Key features

  • Identity-aware reverse proxy
  • Clientless access to internal apps
  • Per-request verification of every action
  • Context-aware access policies
  • Tunnel-free deployment near your services
  • Hosted control plane via Pomerium Zero

Pricing: Free Personal plan. Business costs $7 per user per month billed annually, with a free trial; Enterprise for fully self-hosted deployments is quoted.

Padloc

Padloc is a free, AGPL-licensed, open-source, end-to-end encrypted password manager for individuals and teams, with web, desktop and mobile clients.

GitHub stars
2.9k
Last commit
3 days ago
Latest release
v4.3.0
Licence
AGPL-3.0
Self-hosted
Yes
Hosted version
Available
padloc.appPadloc homepage screenshot

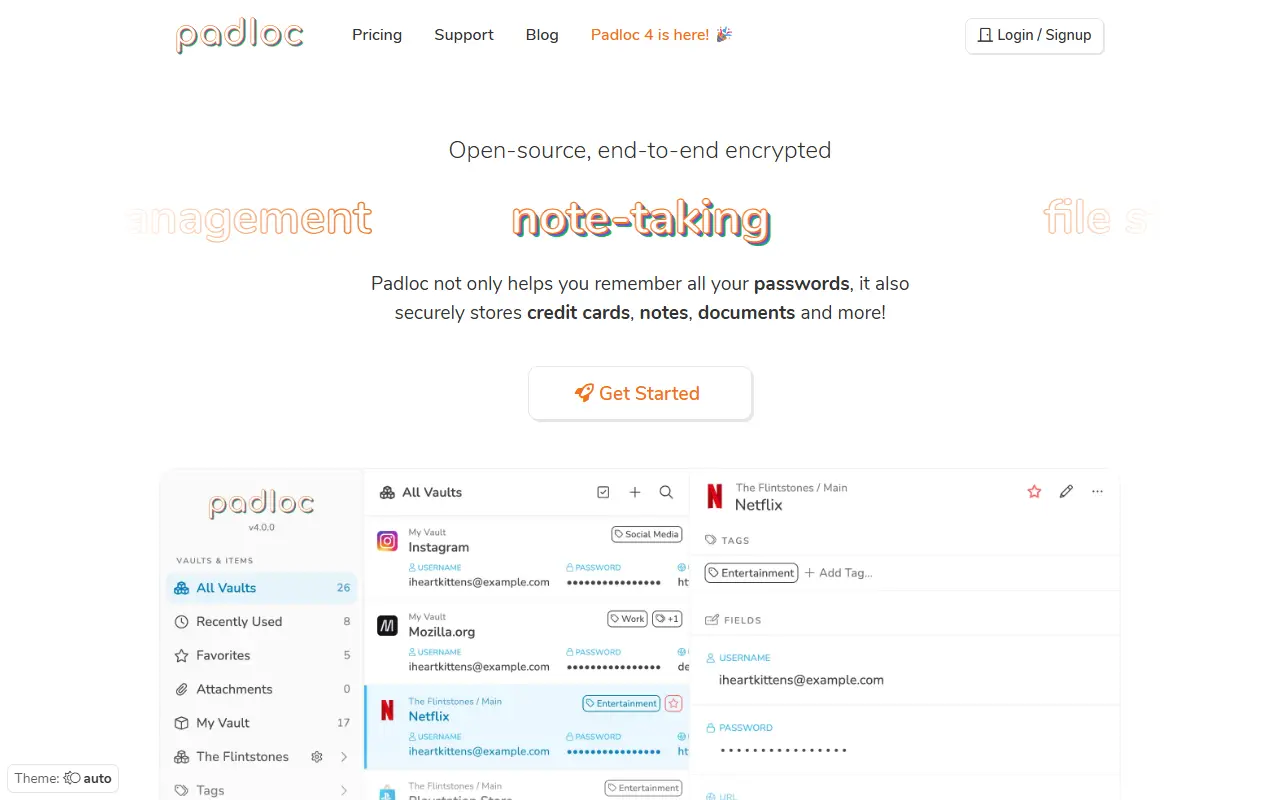
Padloc is a password and secure data manager aimed at both individuals and teams who want an open-source alternative to closed commercial password managers. It emphasizes simplicity and security, built around end-to-end encryption so that stored data is protected even from the server operator.

The project is organized as several packages: a core logic library, web-based UI components, a backend server, a progressive web app client, a desktop app built with Electron, mobile apps built with Cordova, a cross-platform native app built with Tauri, and a browser extension, along with a localization package for translations. This split lets different front ends share the same core encryption and data logic.

Setting up a local instance for testing requires installing and configuring at least the server and a web client, which the README describes as quick to do, while guides for running a production deployment and building distributable desktop and mobile apps are still being written. Padloc is written in JavaScript and TypeScript and released under the AGPL-3.0 license, making it self-hostable.

Key features

  • End-to-end encrypted password storage
  • Web, desktop, mobile and browser extension clients
  • Password generator
  • Team and individual vault support
  • Self-hostable backend server
  • Progressive web app client

Pricing: A free plan is available. Personal Premium costs $3.49 and Family $5.95 per month, Team $3.49 and Business $6.99 per month, each with a 30-day trial and cheaper yearly options; Enterprise is by request.

Webauthn.io

WebAuthn.io is a demo site from Duo Labs for trying WebAuthn and passkey registration and authentication with adjustable settings.

GitHub stars
747
Last commit
3 mo ago
Licence
BSD-3-Clause
webauthn.ioWebauthn.io homepage screenshot

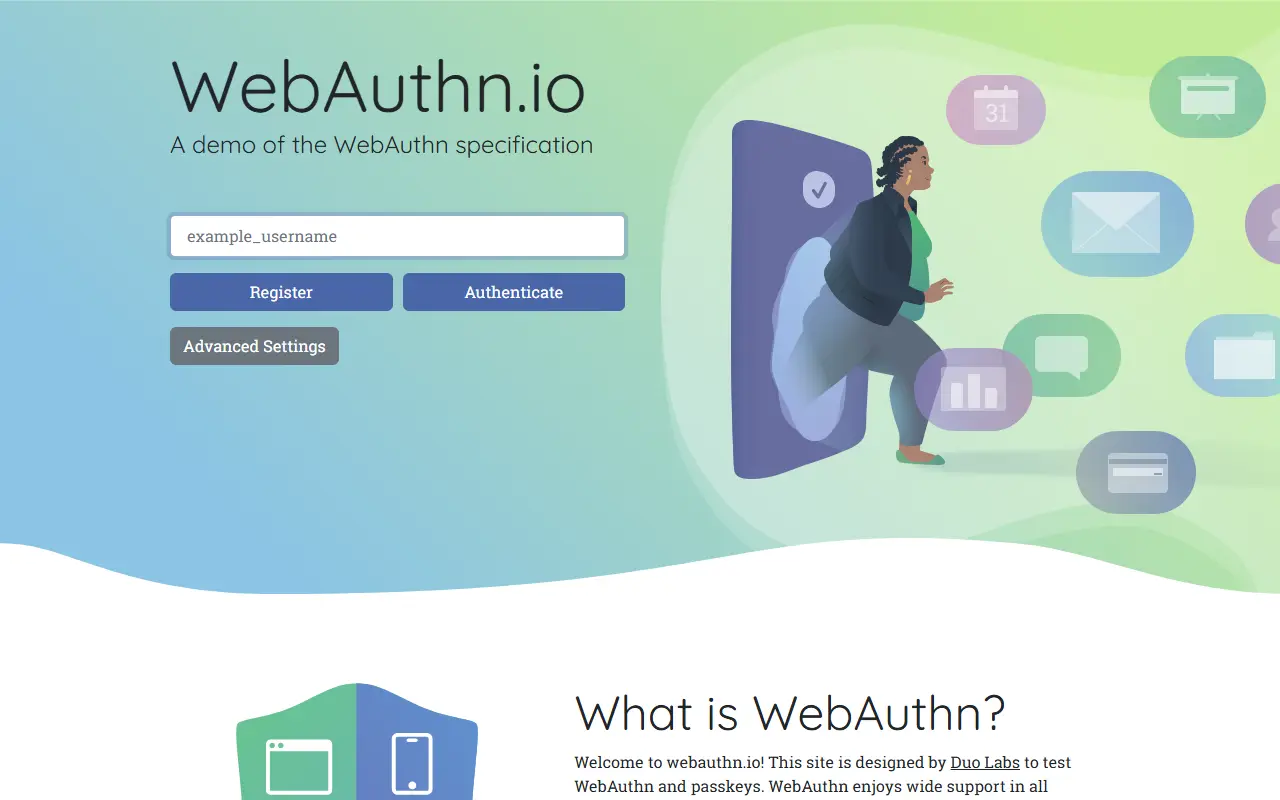
WebAuthn.io is a test site for the WebAuthn specification and passkeys, designed by Duo Labs. You register a credential and then authenticate, and an Advanced Settings panel exposes options such as user verification, attachment, discoverable credentials, attestation, and the order of public key algorithms.

A few conveniences are built in. Changes made in Advanced Settings are carried in the address bar URL, so sharing it lets others open the site with the same configuration. Authenticating without a username tests usernameless sign-in, and adding ?debug=true to the URL shows lower-level information on the profile page after login.

The page also collects pointers for people adding WebAuthn to their own sites: libraries for Python, TypeScript, Ruby, Java, .NET, Go, and Swift, plus other demos. The code for this demo is published on GitHub and the licence is listed as BSD-3-Clause.

Key features

  • Register and authenticate flows for testing passkeys
  • Shareable settings through the page URL
  • Usernameless authentication testing
  • Debug mode for lower-level information
  • Remembers usernames across page loads
  • Links to WebAuthn libraries in several languages

Commercial heylogin alternatives

Hosted, closed-source products that compete with heylogin. Showing 12 of 15.

See every heylogin alternative on its tool page

heylogin alternatives: questions

What is the best open-source alternative to heylogin?
Vaultwarden is the top-ranked open-source alternative to heylogin on Enlisted: Vaultwarden is an AGPL-3.0 server written in Rust that implements the Bitwarden client API for self-hosted password vaults. Other strong options are Keycloak, Bitwarden, step-ca and Passbolt.
What are the best commercial alternatives to heylogin?
1Password, Proton Pass, LastPass, Teleport and Dashlane are among the hosted, closed-source alternatives to heylogin listed on Enlisted, which lists 15 in total. Compare their pricing and features on each tool page.
Are these heylogin alternatives free?
All 8 are open source, so the code is free to use under its licence, and all of them can be self-hosted on your own server or computer. 4 also offer a paid or managed cloud version if you'd rather not host it yourself.
How is this list of heylogin alternatives ranked?
By a score built from GitHub stars, star growth over the last 30 days and how recently the code changed. 7 of these projects shipped code in the last 30 days. Data is refreshed daily, and nobody can pay to move up.

People also look for alternatives to…

View all