
About VulnScanners
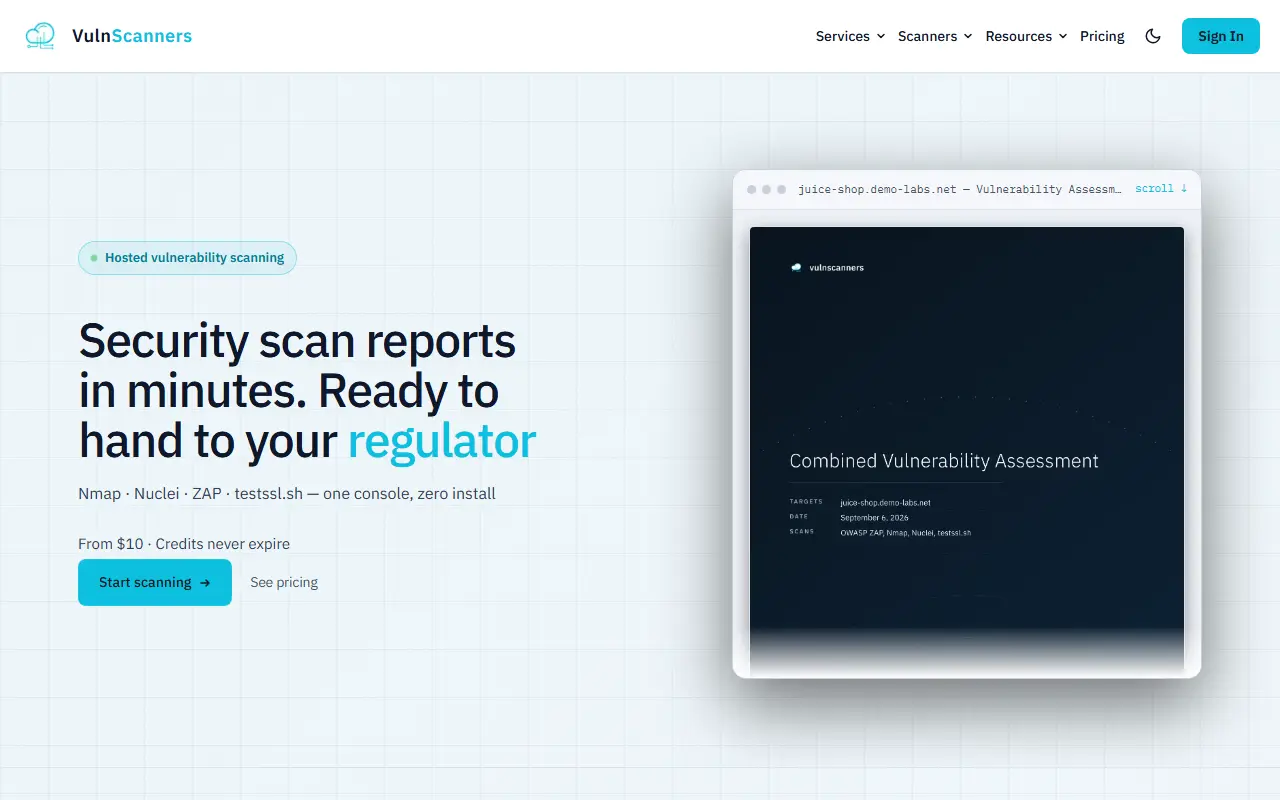
VulnScanners is a hosted service for running vulnerability scans without installing or maintaining scanner software. You pick a target and the platform runs one of four engines on its own servers: Nmap for open ports and services, Nuclei for template-based CVE detection, OWASP ZAP for a web application baseline, and testssl.sh for TLS configuration. It is aimed at managed service providers and security teams.
Each scan turns into a report that can be handed to an auditor, manager or client. The PDFs are branded, rank findings by severity and include remediation advice in plain English. The Nuclei templates are described as refreshed daily, and one console covers many targets and environments, so a new target can be onboarded in minutes. Scans are meant to return a finished report in minutes.
Pricing is per scan rather than by annual contract: each scan costs one credit, ten assessments start from $10 and credits never expire. The site presents this as a lower-cost route than annual enterprise scanner licenses and than running self-hosted scanners that need servers and regular patching.
Key features
- Hosted Nmap, Nuclei, ZAP and testssl.sh scans
- Open port and service discovery
- Template-based CVE detection
- Web application security baseline scanning
- TLS and certificate configuration audits
- Branded, severity-ranked PDF reports
- Plain-English remediation guidance
Good fit for
- MSPs delivering scan reports to clients
- Security teams skipping self-hosted scanner upkeep
- Checking TLS configuration across environments
VulnScanners: questions and answers
- What is VulnScanners used for?
- VulnScanners is a hosted vulnerability scanning with Nmap, Nuclei, ZAP and testssl.sh from one console, producing branded PDF reports for MSPs and security teams. It is a good fit for MSPs delivering scan reports to clients, security teams skipping self-hosted scanner upkeep and checking TLS configuration across environments.
- How much does VulnScanners cost?
- Paid plans for VulnScanners start at $400 per month, and there is no free plan.
- Is VulnScanners open source?
- No. VulnScanners is proprietary (closed-source) software and can't be self-hosted. In the Security category, open-source options include Trivy, Kubescape and IVRE.
- What are some alternatives to VulnScanners?
- VulnScanners competes with Intruder, Invicti and Qualys.
Open-source alternatives to VulnScanners
See all
Trivy
Security
Find vulnerabilities, misconfigurations, secrets, SBOM in containers, Kubernetes, code rep
Apache-2.0vs Snyk★ 38k
Kubescape
Security
Kubescape is an open-source Kubernetes security platform for your IDE, CI/CD pipelines, an
Apache-2.0vs Wiz★ 12k
IVRE
Security
Network recon framework. Build your own, self-hosted and fully-controlled alternatives to
GPL-3.0vs Shodan★ 4.2kuBlock Origin
Security
uBlock Origin - An efficient blocker for Chromium and Firefox. Fast and lean.
GPL-3.0★ 68k
Cryptomator
Security
Cryptomator for Windows, macOS, and Linux: Secure client-side encryption for your cloud st
GPL-3.0vs Tresorit★ 16k
VeraCrypt
Security
Disk encryption with strong security based on TrueCrypt
OSS★ 12k
SaaS alternatives to VulnScanners
See all
Intruder
Security
Cloud-based vulnerability scanner for external attack surface
SaaS
Invicti
Security
Web application security scanning platform formerly known as Netsparker
SaaS
Qualys
Security
Cloud platform for vulnerability management, compliance and asset inventory
SaaS
Tenable
Security
Vulnerability management and exposure assessment, maker of the Nessus scanner
SaaSRapid7
Security
Vulnerability management, SIEM and managed detection tools for security teams
SaaS
VeilScan
Security
Automated vulnerability scanner that maps your external perimeter and verifies findings with exploit evidence
SaaS