 TrackMedia
 TrackRev
About Netsparker
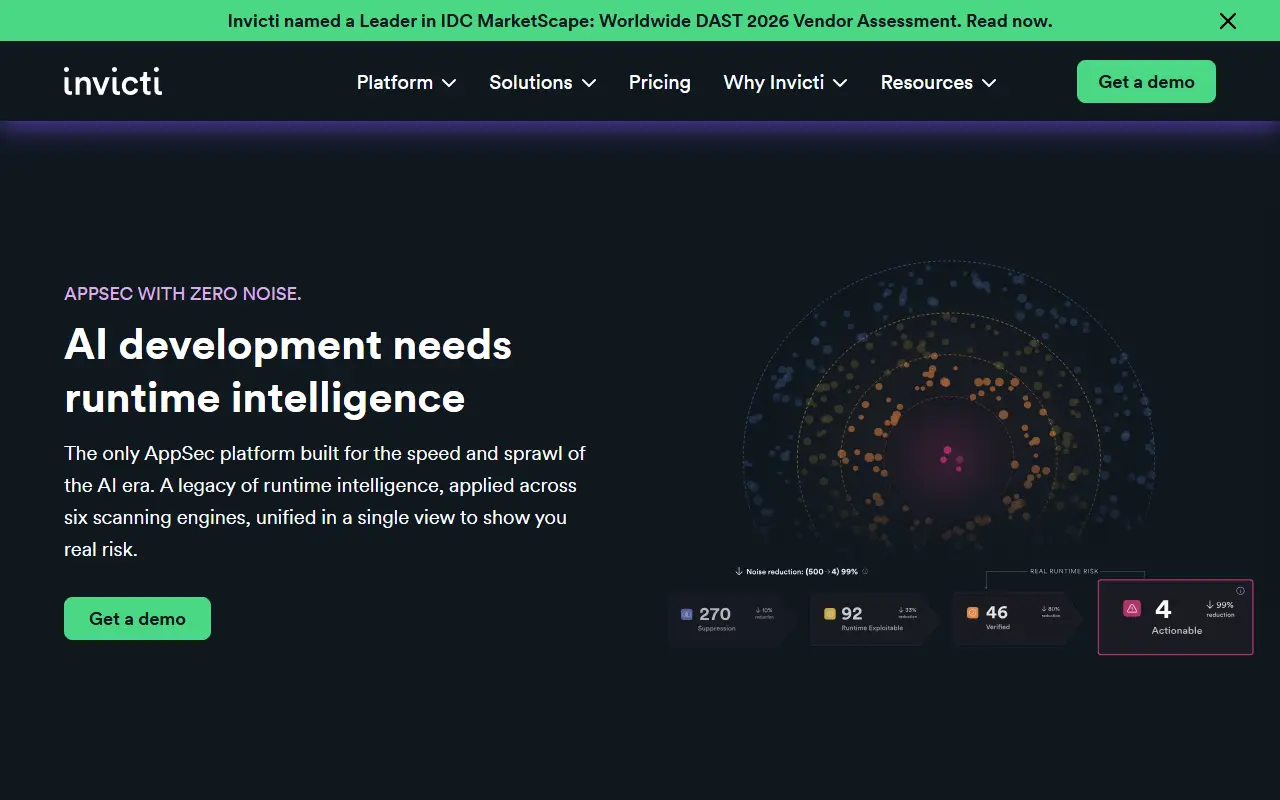
Invicti, the company behind the product formerly sold as Netsparker, describes an application security platform built around dynamic scanning of running web applications and APIs. Its proof-based scanning tries to exploit a flagged issue safely and shows the evidence, so teams can tell confirmed flaws from guesses.
Around that scanner the platform adds static analysis (SAST), software composition analysis, SBOM generation, secrets detection, infrastructure-as-code and container findings. Results from these engines are gathered into a single view and ranked using runtime reachability and exploitability, and issues can be assigned to developers.
It plugs into CI/CD systems such as Jenkins, GitHub, GitLab and Azure DevOps. The site separately advertises an agentic pentest option and API discovery for finding APIs a team did not know about. Pricing is handled through demos, apart from the pentest listing.
Key features
- Proof-based scanning confirms vulnerabilities by safely exploiting them
- Scans run from Jenkins, GitHub, GitLab or Azure DevOps
- Shadow API discovery with checks for BOLA and BFLA flaws
- SBOM generation and license-risk flagging
- Detection of exposed API keys, passwords and tokens
- Validated SAST findings traced to the file and line
- Agentic pentesting for one application and its APIs
Good fit for
- Scanning running web apps and APIs
- Finding unknown APIs
- Generating SBOMs
- Triaging findings from several scanners
- Running a pentest on one application
Netsparker: questions and answers
- What is Netsparker used for?
- Netsparker is now Invicti, an application security platform that combines DAST, SAST, SCA and API scanning with proof-based confirmation of vulnerabilities. It is a good fit for scanning running web apps and APIs, finding unknown APIs, and generating SBOMs.
- Is Netsparker open source?
- No. Netsparker is proprietary (closed-source) software. In the Security category, open-source options include DefectDojo, Dependency-Track and Trivy.
- What are some alternatives to Netsparker?
- Netsparker competes with SEOptimer and Sitebulb.
Open-source alternatives to Netsparker
See all
DefectDojo
Security
Open-Source Unified Vulnerability Management, DevSecOps & ASPM
BSD-3-Clausevs Tenable★ 5.2k
Dependency-Track
Security
Dependency-Track is an intelligent Component Analysis platform that allows organizations t
Apache-2.0vs Snyk★ 4.4k
Trivy
Security
Find vulnerabilities, misconfigurations, secrets, SBOM in containers, Kubernetes, code rep
Apache-2.0vs Snyk★ 39k
Semgrep
Security
Lightweight static analysis for many languages. Find bug variants with patterns that look
LGPL-2.1vs Snyk★ 18k
Horusec
Security
Horusec is an open source tool that improves identification of vulnerabilities in your pro
Apache-2.0vs Checkmarx★ 1.3k
OpenBao
Security
OpenBao is a software solution to manage, store, and distribute sensitive data including s
MPL-2.0vs AWS Secrets Manager★ 9k
SaaS alternatives to Netsparker
See allSEOptimer
Marketing & SEO
Website SEO audit tool and white-label reporting for agencies
SaaS
Sitebulb
Marketing & SEO
Website crawler producing technical SEO audits and prioritized hints
SaaS
Checkmarx
Security
Application security testing platform with SAST, SCA and API security
SaaS
Amabrik
Security
One-script site widgets: security scan, SEO and AI-visibility scan, and cookie consent
SaaS
Rapid7
Security
Vulnerability management, SIEM and managed detection tools for security teams
SaaS
Ultimate WP Audit
Monitoring & Observability
WordPress audit tool running 258+ automated checks across 18 categories on health, security and performance
SaaS