About actionlint
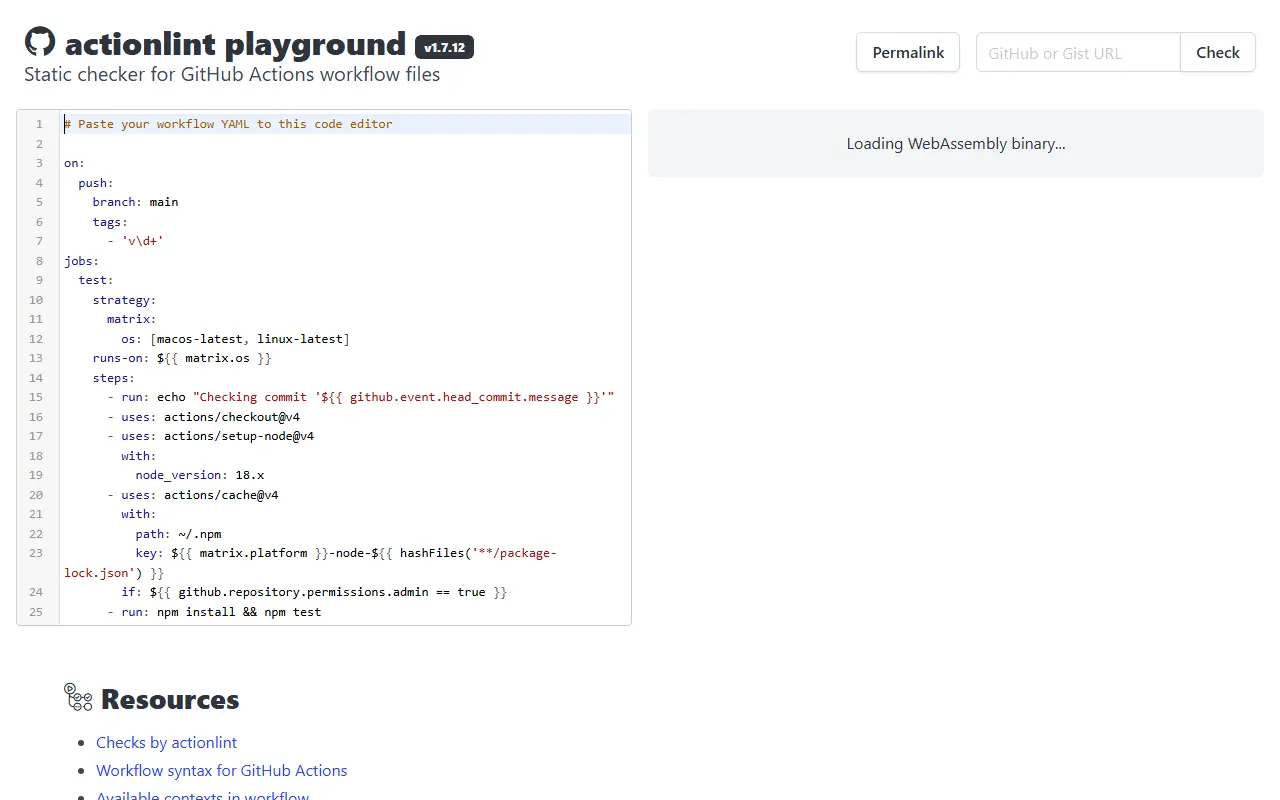
actionlint, published under the rhysd repository, is a static checker for GitHub Actions workflow files. Instead of waiting for a workflow to fail in CI, you run it locally or in a pipeline and it reports mistakes in the YAML, so broken workflows are caught before they are pushed or merged.
It validates workflow syntax against the documented keys, type-checks the ${{ }} expressions to catch references to missing properties and mismatched types, and verifies that inputs and outputs of actions and reusable workflows are used correctly. It can also run shellcheck and pyflakes on inline scripts, and includes security checks for script injection from untrusted inputs and hard-coded credentials. Other checks cover glob patterns, job dependencies, runner labels and cron syntax.
The tool is a single command written in Go and released under the MIT licence. You can install a released binary, use Homebrew or go install, or run it through Docker, and an online playground runs it in the browser through WebAssembly. It aims to keep false positives low, which suits developers and DevOps engineers who maintain many workflows.
Key features
- Syntax checking of workflow files
- Type checking of expression syntax
- Validation of action inputs and outputs
- Reusable workflow input and secret checks
- shellcheck and pyflakes integration for scripts
- Script injection and credential security checks
Good fit for
- →Linting workflows in a pre-commit hook
- →Catching broken CI configuration in pull requests
- →Reviewing workflows for injection risks
- Built with
- Go
- Tags
- github-actions
- linter
- static-analysis
- ci
- yaml
- devops
- go
- cli
- security
actionlint: questions and answers
- What is actionlint used for?
- actionlint is a static checker that finds syntax errors, type mistakes and security problems in GitHub Actions workflow files before they run. It is a good fit for linting workflows in a pre-commit hook, catching broken CI configuration in pull requests and reviewing workflows for injection risks.
- Is actionlint open source?
- Yes. actionlint is open source under the MIT licence. Its source code is on GitHub at rhysd/actionlint and is written mainly in Go.
- Is actionlint free?
- Yes. actionlint is open source, so the software itself is free to use.
- What are some alternatives to actionlint?
- Similar open-source tools in the CI/CD & DevOps category include kube-score, Act and Dockerfile Roast. SaaS products in the same category include Travis CI, Blacksmith and Buddy.
- Is actionlint actively maintained?
- Yes. The most recent commit to actionlint was on 16 July 2026, and the latest release is v1.7.12, published on 30 March 2026. The project has 4.3k stars on GitHub.
Open-source alternatives to actionlint
See allkube-score
CI/CD & DevOps
Kubernetes object analysis with recommendations for improved reliability and security. kub
MIT★ 3.1k
Act
CI/CD & DevOps
Run your GitHub Actions locally 🚀
MIT★ 72k
Dockerfile Roast
CI/CD & DevOps
droast - a dockerfile linter that actually has opinions 🔥
MIT★ 1.1k
reviewdog
CI/CD & DevOps
🐶 Automated code review tool integrated with any code analysis tools regardless of progra
MITvs Codacy★ 9.6k
Earthly
CI/CD & DevOps
Super simple build framework with fast, repeatable builds and an instantly familiar syntax
MPL-2.0vs Depot★ 12k
release-plz
CI/CD & DevOps
Publish Rust crates from CI with a Release PR.
Apache-2.0★ 1.5k
SaaS alternatives to actionlint
See all
Travis CI
CI/CD & DevOps
Hosted continuous integration service that builds and tests code from Git repos
SaaS
Blacksmith
CI/CD & DevOps
Faster GitHub Actions runners billed per minute, with build caching
SaaS
Buddy
CI/CD & DevOps
Visual CI/CD tool for building, testing and deploying web projects
SaaS
GitHub
CI/CD & DevOps
GitHub is a developer platform for hosting Git repositories, reviewing code, automating workflows and using AI coding tools such as Copilot.
SaaS
Appcircle
CI/CD & DevOps
Mobile CI/CD platform for building, testing and publishing apps, cloud or self-hosted
SaaS
AWS CodePipeline
CI/CD & DevOps
Managed AWS service that automates build, test and deploy release pipelines
SaaS