 TrackMedia
 TrackRev

 Silverfort
 Imprivata
 Entrust
About privacyIDEA
privacyIDEA is an open-source authentication server that manages multi-factor authentication for an organization. It issues and verifies second factors such as one-time passwords, hardware tokens, push notifications and FIDO2 or WebAuthn security keys, so applications and servers can add two-factor login without each building its own token handling.
The server is written in Python and exposes an API that other systems can call to check a login attempt. Its topics point to support for OTP, passkeys, push authentication and certificates, and administrators enroll and manage tokens centrally rather than configuring every service by hand. The project documentation includes how-tos for running it behind Apache2 with MySQL and for protecting a whole server farm.
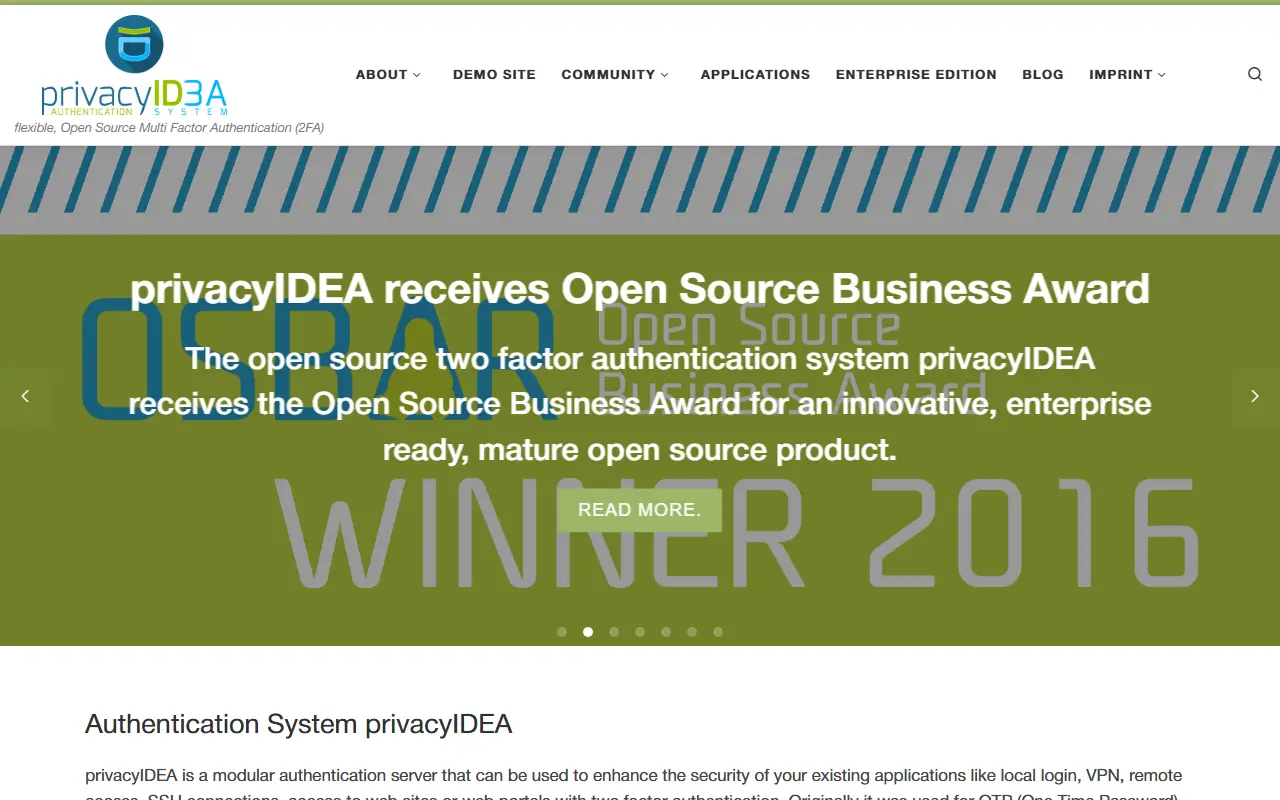
privacyIDEA is released under the AGPL-3.0 licence and can be self-hosted, which keeps token data and user policies on infrastructure you control. The project website also lists an Enterprise Edition next to the community version, along with a demo site, screenshots and community resources for anyone evaluating it.
Key features
- OTP, push, and hardware token support
- FIDO2, WebAuthn, and passkey authentication
- REST API for application integration
- Central web interface for token enrollment
- Policy-based control of authentication rules
- Certificate and CA related features
Good fit for
- Adding two-factor login to existing servers
- Running a central token service for a company
- Replacing a vendor MFA service with self-hosted software
privacyIDEA: questions and answers
- What is privacyIDEA used for?
- privacyIDEA is an open-source authentication server for managing two-factor and multi-factor logins with OTP tokens, push, FIDO2 keys and passkeys across an organization. It is a good fit for adding two-factor login to existing servers, running a central token service for a company and replacing a vendor MFA service with self-hosted software.
- Is privacyIDEA open source?
- Yes. privacyIDEA is open source under the AGPL-3.0 licence. Its source code is on GitHub at privacyidea/privacyidea and is written mainly in Python.
- Is privacyIDEA free?
- Yes. privacyIDEA is open source, so the software itself is free to use.
- Can I self-host privacyIDEA?
- Yes. privacyIDEA can be self-hosted on your own server or infrastructure.
- What is privacyIDEA an alternative to?
- privacyIDEA is an open-source alternative to Duo Security, RSA, Beyond Identity and IBM Verify. Other open-source alternatives to Duo Security include Keycloak, Authentik and Authelia.
- Is privacyIDEA actively maintained?
- Yes. The most recent commit to privacyIDEA was on 13 November 2026, and the latest release is v3.14, published on 7 October 2026. The project has 1.8k stars on GitHub, with 11 added in the last 30 days.
Open-source alternatives to privacyIDEA
See all
Keycloak
Auth & Identity
Open Source Identity and Access Management For Modern Applications and Services
Apache-2.0vs Auth0★ 38k
WSO2 Identity Server
Auth & Identity
Welcome to the WSO2 Identity Server source code! For info on working with the WSO2 Identit
Apache-2.0vs Auth0★ 889
Authentik
Auth & Identity
The authentication glue you need.
OSSvs Auth0★ 26k
FreeIPA
Auth & Identity
Mirror of FreeIPA, an integrated security information management solution
GPL-3.0vs Microsoft Entra ID★ 1.3k
Authelia
Auth & Identity
The Single Sign-On Multi-Factor portal for web apps. OpenID Certified™ and Post-Quantum Cr
Apache-2.0vs OneLogin★ 30k
Hanko
Auth & Identity
Open source, privacy-first, and built to scale. Hanko is the fastest way you integrate pas
OSSvs Auth0★ 9.1k
SaaS alternatives to privacyIDEA
See all
Duo Security
Auth & Identity
Cisco's multi-factor authentication and device trust service for workforces
SaaS
RSA
Auth & Identity
Enterprise MFA, SSO and identity governance with hardware and software tokens
SaaS
Beyond Identity
Auth & Identity
Phishing-resistant passwordless MFA with device trust checks
SaaS
IBM Verify
Auth & Identity
IBM SSO, MFA and identity governance for workforce and customer identities
SaaS
Authsignal
Auth & Identity
Step-up authentication and passkey APIs for fraud-resistant logins
SaaS
HYPR
Auth & Identity
Passwordless and phishing-resistant MFA for workforce and customers
SaaS