#1
Keycloak is an open-source identity and access management server that adds single sign-on, user management and authorization to applications.
- GitHub stars
- 38k
- Last commit
- yesterday
- Latest release
- 26.8.2
- Licence
- Apache-2.0
- Self-hosted
- Yes
keycloak.org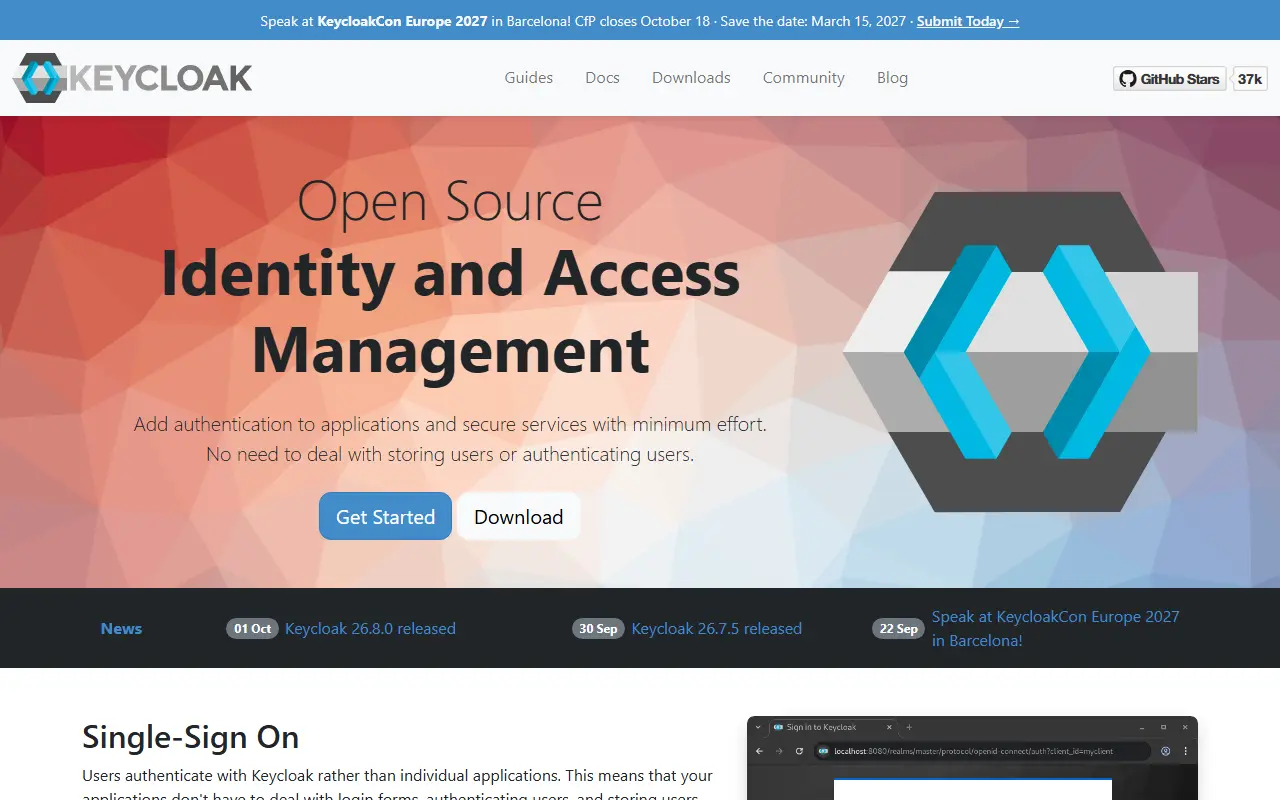
Keycloak is an open-source identity and access management server. It lets application teams add authentication and secure services without building their own login system, since Keycloak handles storing users and authenticating them. The project is written in Java, released under the Apache-2.0 license and governed under the Cloud Native Computing Foundation code of conduct.
Keycloak supports standard protocols such as OpenID Connect and SAML, and offers user federation, strong authentication, user management and fine-grained authorization. You can run it from the downloadable distribution using a start-dev command, or use the official Docker image published on Quay for containers and Kubernetes setups. The project provides documentation, a user mailing list and community channels for help, along with guidance for building and testing from source.
Key features
- Single sign-on with OpenID Connect and SAML
- User federation with external directories
- Strong and multi-step authentication options
- Central user and account management
- Fine-grained authorization policies
- Docker image and standalone distribution
Pricing: Free and open source under the Apache-2.0 license; you host and operate it yourself.
#2
A self-hosted single sign-on and multi-factor authentication portal that protects web applications, certified for OpenID Connect and ready for post-quantum cryptography.
- GitHub stars
- 30k
- Last commit
- yesterday
- Latest release
- v4.39.28
- Licence
- Apache-2.0
- Self-hosted
- Yes
authelia.com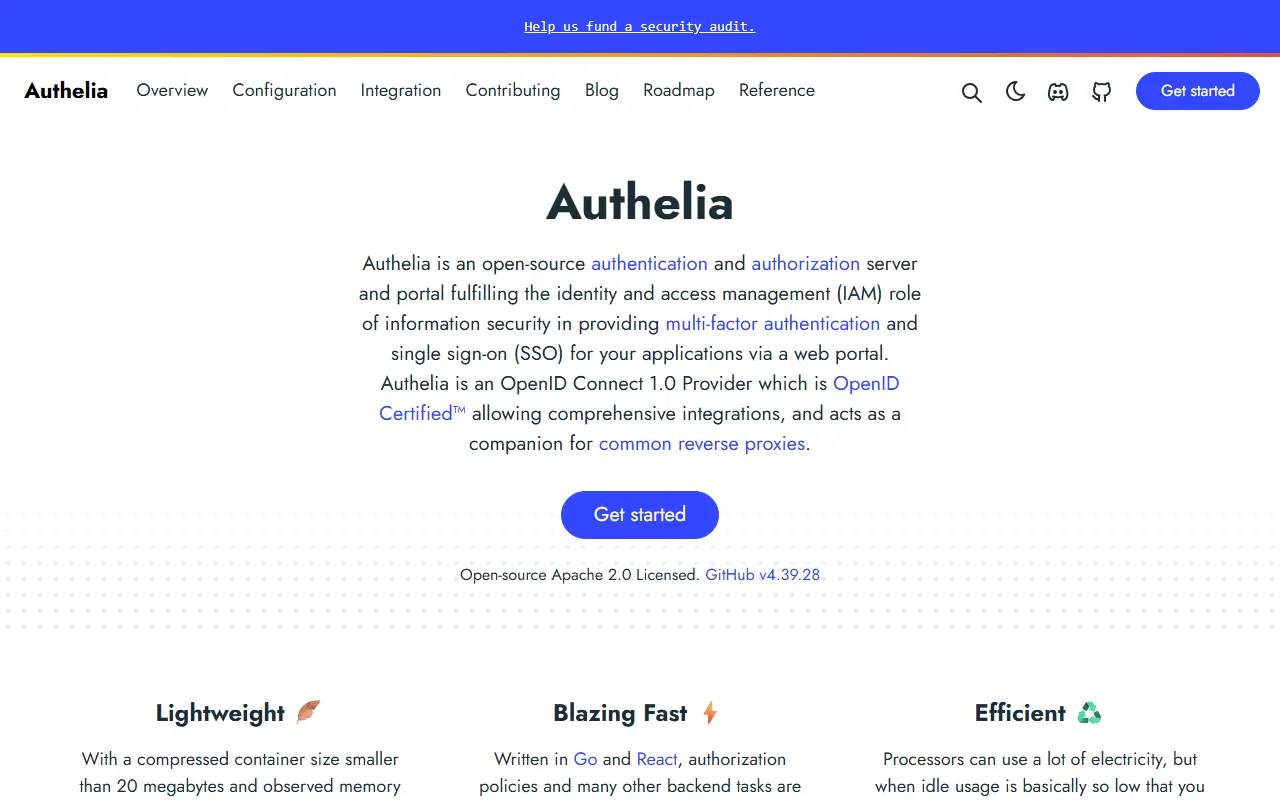
Authelia is an open-source authentication and authorization server that provides single sign-on and multi-factor authentication for web applications. It sits in front of your services, usually alongside a reverse proxy, so users sign in once at a portal and are checked against policies before reaching an app.
Supported factors and backends include TOTP, push notifications, two-factor methods and LDAP, according to its topics, and it is described as OpenID Certified and ready for post-quantum cryptography. It is written in Go and runs well as a small container, with documentation for Docker and Kubernetes deployments. Self-hosters often use it to add a consistent login and second factor to tools that have weak or no authentication of their own.
Authelia is licensed under Apache-2.0. As an authentication component, it is meant to be run on your own infrastructure, and it suits home labs, small organizations and teams wanting a lightweight identity layer without a heavier enterprise identity platform.
Key features
- Single sign-on portal for web apps
- Multi-factor authentication including TOTP
- Push notification verification
- LDAP user backend support
- OpenID Connect support
- Docker and Kubernetes deployment
Pricing: Free and open source under the Apache-2.0 license.
#3
An open-source identity provider for single sign-on that supports SAML, OAuth2 and OIDC, LDAP and RADIUS, built for self-hosting from home labs to large clusters.
- GitHub stars
- 26k
- Last commit
- yesterday
- Latest release
- version/2026.8.5
- Self-hosted
- Yes
goauthentik.io
authentik is an open-source Identity Provider for modern single sign-on. It supports SAML, OAuth2 and OpenID Connect, LDAP, RADIUS and more, and is designed for self-hosting at any scale, from a small lab to production clusters. A reverse-proxy mode also lets it protect applications that lack native SSO support.
The project positions its enterprise offering as a way for organizations to replace incumbent identity providers (Okta, Auth0, Entra ID or Ping Identity) in large-scale identity management. For installation, Docker Compose is recommended for small and test setups, a Helm chart for Kubernetes suits larger setups, and official templates exist for AWS CloudFormation and a one-click DigitalOcean Marketplace app.
The codebase is mostly Python with Kubernetes tooling, and the license is listed as 'Other' on GitHub because it mixes open-source and enterprise components, so check which features fall under which terms. authentik is a common choice for self-hosters and companies who want to centralize logins across internal tools without paying per-user fees to a hosted identity vendor.
Key features
- SAML and OAuth2/OIDC provider
- LDAP and RADIUS support
- Reverse-proxy authentication for apps
- Docker Compose and Helm chart installs
- AWS CloudFormation and DigitalOcean templates
- Enterprise edition for large deployments
Pricing: The open-source edition is free. Enterprise costs $5 per user per month billed annually, plus $0.02 per external user; Enterprise Plus starts at $20k per year. No hosted version is offered.
#4
An open-source identity and access management platform written in Go, providing single sign-on, OAuth, OIDC, SAML, MFA and a web console for users and applications.
- GitHub stars
- 15k
- Last commit
- 2 days ago
- Latest release
- v4.27.1
- Licence
- Apache-2.0
- Self-hosted
- Yes
casdoor.ai
Casdoor is a self-hosted identity and access management platform with a web console. It acts as a single sign-on and authentication server, so applications can delegate login to it instead of implementing their own user management, sessions and password handling.
Supported protocols include OIDC, OAuth 2.0, SAML 2.0, LDAP, CAS and SCIM 2.0, alongside WebAuthn, TOTP and MCP, and it can connect to identity providers such as Google Workspace, Microsoft Entra ID and GitHub. Sign-in options include passwords, email or SMS codes, WebAuthn and Face ID, plus any social providers you enable. The admin console covers users, tokens, organizations, providers and applications, and settings change without a redeploy or config file.
Casdoor is written in Go and licensed under Apache-2.0. A quick trial runs on SQLite with sample data and needs no separate database or config file. Its newer positioning emphasizes AI agents, with an MCP and agent gateway for LLM tooling, and hosted demo instances are available for trying it before installing.
Key features
- Single sign-on and authentication server
- OIDC, OAuth 2.0 and SAML support
- LDAP, CAS and SCIM integration
- WebAuthn, TOTP and MFA
- Social and enterprise identity providers
- Web console for users and organizations
- MCP and agent gateway features
Pricing: Free and open source under the Apache-2.0 licence.
Rauthy is a Rust identity provider for single sign-on, supporting OpenID Connect, OAuth 2 and PAM, with an emphasis on passkeys and secure defaults.
- GitHub stars
- 1.4k
- Last commit
- yesterday
- Latest release
- v0.37.2
- Licence
- Apache-2.0
- Self-hosted
- Yes
sebadob.github.io
Rauthy is an Identity Provider that handles OpenID Connect, OAuth 2 and PAM logins. It is written in Rust and aims to be simple to set up and operate, with secure defaults and many configuration options for people who need flexibility. Single sign-on for IoT devices and headless command-line tools is covered as well.
By default it runs on Hiqlite and needs no external database, with Postgres available as an alternative. The documentation positions it as an SSO solution comparable to Keycloak but with a smaller resource footprint, and says it can run on a Raspberry Pi. It includes high availability, client branding, UI translation, an admin UI, events and auditing.
Login options centre on FIDO 2 and WebAuthn: either a password plus a security key, or passkey-only accounts that need just an e-mail address. The project received an independent security audit by Radically Open Security as part of NGI Zero Core funding, with findings addressed in v0.32.1.
Key features
- OpenID Connect, OAuth 2 and PAM identity provider
- Passkey-only accounts without a password
- Runs without an external database by default
- High availability, branding, translations, admin UI, auditing
- Single sign-on for IoT and headless CLI tools
- New OIDC clients use ed25519 and S256 PKCE

Apereo CAS is an enterprise identity provider and single sign-on server written in Java, supporting CAS, SAML2, OpenID Connect, OAuth2 and multifactor authentication.
- GitHub stars
- 11k
- Last commit
- yesterday
- Latest release
- v8.0.3
- Licence
- Apache-2.0
- Self-hosted
- Yes
apereo.github.io
This entry covers Apereo CAS, the Central Authentication Service. CAS is both an open and well-documented authentication protocol and the primary open-source Java server implementing it, which works as a multilingual, enterprise-grade identity provider and web single sign-on solution.
Beyond its own protocol, the server supports additional authentication protocols and features, including SAML2, OpenID Connect, OAuth2, LDAP authentication and multifactor authentication, with topics also referencing FIDO and Duo Security. It is built on Spring Boot, Spring Webflow and Spring Cloud, and aims to be a comprehensive platform for authentication and authorization needs.
Apereo CAS is licensed under Apache-2.0. The recommended way to deploy it is the WAR Overlay method, and cloning the full codebase is only needed if you want to contribute. Documentation, release notes, a maintenance policy and a release schedule are published by the project. It is typically adopted by universities and other organizations that need centralized login across many applications.
Key features
- Single sign-on for web applications
- CAS protocol server
- SAML2 and OpenID Connect support
- OAuth2 and LDAP authentication
- Multifactor authentication including FIDO
- Spring Boot based Java server
- WAR overlay deployment method
Pricing: Free and open source under the Apache-2.0 licence.
#7
Self-hostable single sign-on and user management provider with OIDC, proxy ForwardAuth, LDAP, passkeys, invitations, and an admin panel.
- GitHub stars
- 2.9k
- Last commit
- yesterday
- Latest release
- v1.19.1
- Licence
- AGPL-3.0
- Self-hosted
- Yes
voidauth.app
VoidAuth is an open-source SSO authentication and user management provider that sits in front of self-hosted applications. It is meant to be easy for administrators and end users, adding features such as passkeys, user invitations, self-registration, and email support. It runs in Docker and is released under the AGPL-3.0 license.
It acts as an OpenID Connect provider, supports proxy ForwardAuth for protecting apps behind a reverse proxy, and offers an LDAP directory server. Administrators manage users and groups from an admin panel, invite users or allow self-registration, and customize the logo, title, theme color, and email templates. Security options include multi-factor authentication, passkey-only accounts, and password resets verified by email.
Data is stored in Postgres or SQLite with encryption at rest. VoidAuth suits homelab users and small teams who run several services and want one login across them, as a lighter alternative to larger identity platforms.
Key features
- OpenID Connect provider
- Proxy ForwardAuth for reverse proxies
- LDAP directory server
- User and group management with invitations
- Multi-factor authentication and passkeys
- Customizable branding and email templates
- Encryption at rest with Postgres or SQLite
Pricing: Free and open source under the AGPL-3.0 license.
#8
Java identity and access management product offering single sign-on with OAuth 2, OpenID Connect, SAML, CAS, JWT, and SCIM, plus RBAC and user lifecycle management.
- GitHub stars
- 2k
- Last commit
- today
- Latest release
- 4.2.0
- Licence
- Apache-2.0
- Self-hosted
- Yes
maxkey.top
MaxKey, from the Dromara community, is an IAM and IDaaS product written in Java and released under the Apache-2.0 license. It provides single sign-on, identity management, access management, RBAC-based permission control, and resource management. The name is a homophone of a phrase about a master key that unlocks enterprise security needs, according to the README.
It supports standard protocols including OAuth 2.x and OpenID Connect, SAML 2.0, CAS, JWT, and SCIM, and its topics also list LDAP, Active Directory, Kerberos, multi-factor authentication, TOTP, and multi-tenancy. Features focus on user lifecycle management and compliance, and the project presents itself as open, secure, and self-controlled. Documentation is in English and Chinese.
MaxKey is aimed at enterprises, particularly in Chinese-speaking markets, that need a self-hosted alternative to commercial identity platforms. Teams should confirm industry claims in the README against their own requirements.
Key features
- Single sign-on across applications
- OAuth 2.x, OpenID Connect, SAML 2.0, and CAS
- SCIM provisioning and user lifecycle management
- RBAC permission management
- LDAP, Active Directory, and MFA integration
- Multi-tenancy support
Pricing: Free and open source under the Apache-2.0 license.
#9
FreeIPA is an integrated identity, authentication and access control system for Linux and UNIX networks, built on LDAP, Kerberos and PKI.
- GitHub stars
- 1.3k
- Last commit
- 2 days ago
- Licence
- GPL-3.0
- Self-hosted
- Yes
freeipa.org
FreeIPA lets Linux administrators centrally manage identity, authentication and access control for Linux and UNIX systems. It provides command-line and web-based management tools that are simple to install and use, and it focuses on ease of management and automation of installation and configuration. The repository is a mirror of the upstream project and is written mostly in Python.
The README lists benefits such as letting users access every machine with the same credentials and security settings, transparent access to personal files from any machine, grouping to restrict services and files to specific users, central management of passwords, SSH public keys, sudo rules, keytabs and access control rules, and delegation of selected administrative tasks to other power users.
FreeIPA bundles well-known open-source components with unified tools: an LDAP server based on the 389 project, a Kerberos KDC based on MIT Kerberos, a public key infrastructure based on Dogtag, Samba libraries for Active Directory integration and a DNS server based on BIND. It can integrate into Active Directory environments through cross-realm Kerberos trust or user synchronization. The code is licensed under GPL-3.0.
Key features
- Central identity and authentication management
- LDAP and Kerberos services
- Certificate authority based on Dogtag
- Integrated DNS server
- Sudo rules and SSH key management
- Active Directory trust and synchronization
Pricing: Free and open source under the GPL-3.0 license.
#10
SimpleSAMLphp is a PHP authentication application that acts as a SAML 2.0 service provider or identity provider and supports CAS, OpenID Connect and OAuth.
- GitHub stars
- 1.1k
- Last commit
- 2 days ago
- Latest release
- v2.5.4
- Licence
- LGPL-2.1
- Self-hosted
- Yes
simplesamlphp.org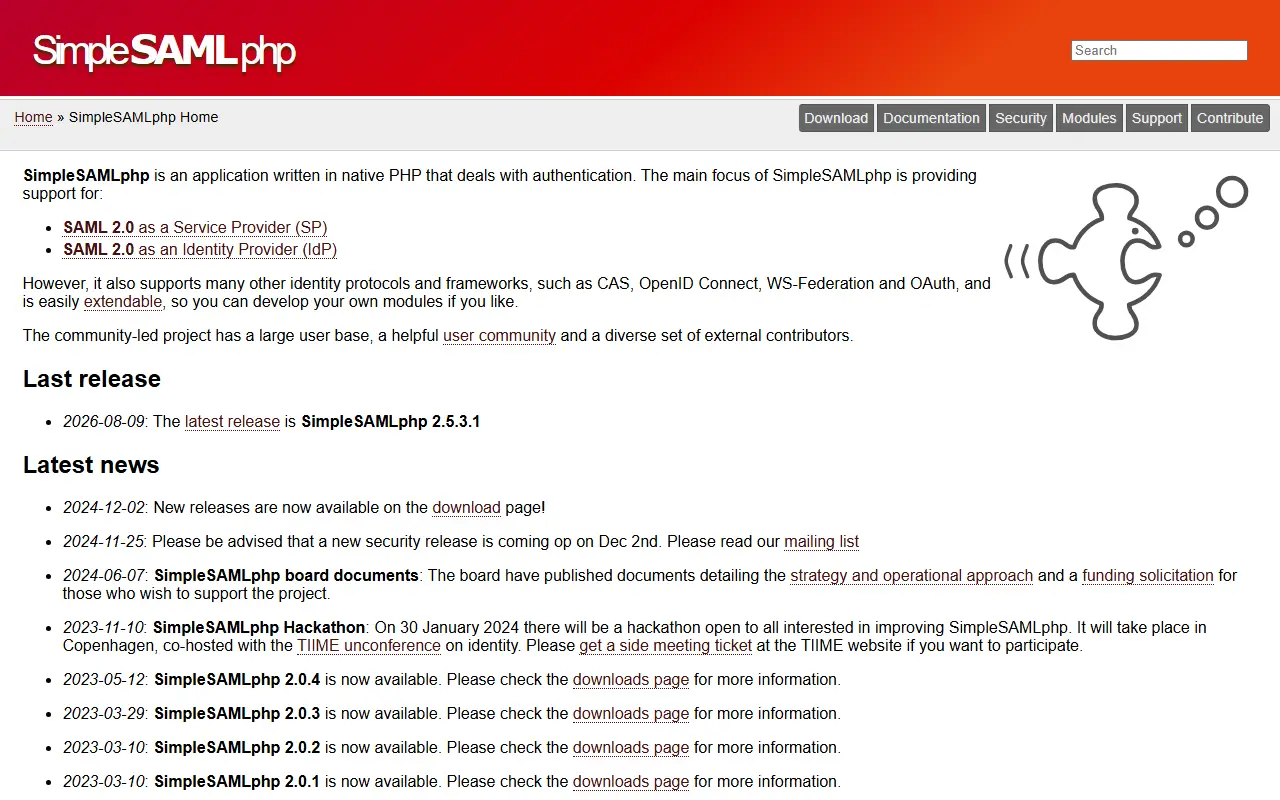
SimpleSAMLphp is an application written in native PHP that deals with authentication. Its main focus is SAML 2.0, where it can act either as a service provider that protects a web application or as an identity provider that authenticates users, which makes it common in universities and organizations using federated login.
It also supports other identity protocols and frameworks including CAS, OpenID Connect, WS-Federation and OAuth, and it is easy to extend with custom modules. The project site offers downloads, documentation, security announcements, modules and support, and the community-led project publishes regular releases, with security releases announced on its mailing list in advance.
SimpleSAMLphp is licensed under LGPL-2.1 and installed on your own PHP web server, so it is self-hosted. The project is run by a board and community of contributors. It suits developers and identity administrators who need to connect PHP applications to a SAML federation or run a lightweight identity provider.
Key features
- SAML 2.0 service provider
- SAML 2.0 identity provider
- CAS, OpenID Connect, and WS-Federation support
- OAuth support
- Extensible through modules
- Regular releases with security announcements
Pricing: Free and open source under the LGPL-2.1 licence.
2 more OneLogin alternatives
OneLogin alternatives: questions
- What is the best open-source alternative to OneLogin?
- Keycloak is the top-ranked open-source alternative to OneLogin on Enlisted: Keycloak is an open-source identity and access management server that adds single sign-on, user management and authorization to applications. Other strong options are Authelia, Authentik, Casdoor and Rauthy.
- What are the best commercial alternatives to OneLogin?
- Microsoft Entra ID, IBM Verify, JumpCloud, Ping Identity and Duo Security are among the hosted, closed-source alternatives to OneLogin listed on Enlisted, which lists 25 in total. Compare their pricing and features on each tool page.
- Are these OneLogin alternatives free?
- All 12 are open source, so the code is free to use under its licence, and all of them can be self-hosted on your own server or computer. 1 also offers a paid or managed cloud version if you'd rather not host it yourself.
- How is this list of OneLogin alternatives ranked?
- By a score built from GitHub stars, star growth over the last 30 days and how recently the code changed. 12 of these projects shipped code in the last 30 days. Data is refreshed daily, and nobody can pay to move up.
 TrackMedia
 TrackRev