frp is an Apache-2.0 reverse proxy written in Go that exposes servers behind a NAT or firewall to the internet over TCP, UDP, HTTP and HTTPS.
- GitHub stars
- 111k
- Last commit
- 3 days ago
- Latest release
- v0.72.0
- Licence
- Apache-2.0
- Self-hosted
- Yes
frp is a reverse proxy for reaching a local server that sits behind a NAT or firewall from the public internet. It supports TCP and UDP as well as HTTP and HTTPS, so requests can be forwarded to internal services by domain name. It also has a P2P connect mode.
The README's table of contents shows how wide the feature set is. It covers a server dashboard and a client admin UI, Prometheus monitoring, token and OIDC authentication, encryption and compression, TLS, bandwidth limits per proxy, TCP stream multiplexing, KCP and QUIC protocol support, load balancing and health checks.
Examples in the README include reaching a machine over SSH inside a LAN, sharing one port between several SSH services, serving internal web apps on custom domains, forwarding DNS queries and Unix domain sockets, and exposing a simple HTTP file server. Version 1 is in maintenance mode while the author works on an incompatible version 2.
Key features
- Exposes local servers behind NAT or firewalls
- Supports TCP, UDP, HTTP and HTTPS
- Peer-to-peer connect mode
- Token and OIDC authentication for clients
- KCP and QUIC protocol support
- Server dashboard, client admin UI and Prometheus monitoring
- Per-proxy bandwidth limits and port range mapping
- SSH tunnel gateway and virtual network features

NetBird builds a secure WireGuard-based overlay network for devices and users, with SSO, MFA and granular access controls.
- GitHub stars
- 31k
- Last commit
- yesterday
- Latest release
- v0.82.1
- Self-hosted
- Yes
- Hosted version
- Available
netbird.io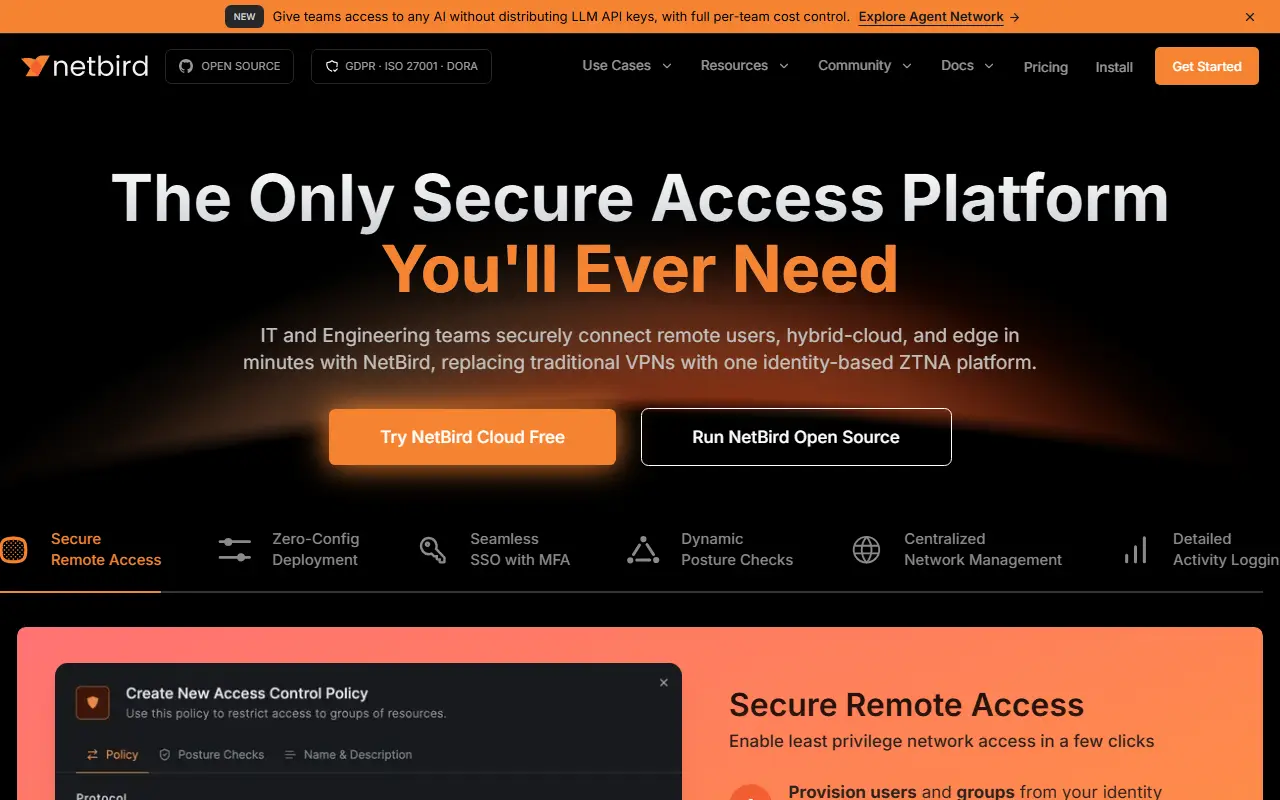
NetBird joins a configuration-free peer-to-peer private network with a central access control system on one platform. It creates a WireGuard-based overlay that connects machines over encrypted tunnels automatically, which avoids opening ports, writing complex firewall rules or running VPN gateways. It is written in Go and can be used for an organization or a home network. The repository metadata lists the license as Other.
Connectivity features include kernel WireGuard, peer-to-peer connections with relay fallback, routes to external networks, exit nodes, and private DNS with custom zones. For management and security there is an admin web UI, automatic peer discovery, SSO and MFA, identity provider integrations, groups and rules for access control, activity logging, traffic events and device posture checks. A public API, setup keys, a Terraform provider and a self-hosting quickstart script support automation. Clients cover Linux, macOS, Windows, Android and Android TV, and an agent network beta targets AI agents.
Key features
- WireGuard-based peer-to-peer overlay network
- Relay fallback when direct connections fail
- SSO, MFA and identity provider integrations
- Access control through groups and rules
- Private DNS, exit nodes and network routes
- Public API and Terraform provider
Pricing: The cloud Free plan covers up to 5 users. Team costs €6 and Business €12 per user per month, with a free trial; Enterprise is custom, and NetBird can also be self-hosted.
Headscale is a BSD-3-Clause, self-hosted implementation of the Tailscale control server, written in Go for homelabs and small organisations.
- GitHub stars
- 46k
- Last commit
- yesterday
- Latest release
- v0.29.7
- Licence
- BSD-3-Clause
- Self-hosted
- Yes
Headscale is an open source, self-hosted implementation of the Tailscale control server. Tailscale is a VPN built on WireGuard that links machines into an overlay network using NAT traversal. The control server exchanges WireGuard public keys, assigns client IP addresses, sets boundaries between users, and exposes the routes your nodes advertise.
The design goal is a self-hosted alternative for self-hosters and hobbyists to use in projects and labs. The scope is deliberately narrow: a single Tailscale network (tailnet), suitable for personal use or a small open-source organisation. Features and client operating system support are documented on the project's documentation site.
It is not associated with Tailscale Inc, although one active maintainer works there. The README advises matching the GitHub tag to the release you run so example configuration fits, and it provides a NixOS module plus development builds as container images and binaries. It also says reverse proxies and containers are not supported or encouraged.
Key features
- Self-hosted Tailscale control server
- Exchanges WireGuard public keys between nodes
- Assigns client IP addresses and user boundaries
- Exposes advertised routes of nodes
- NixOS module available
- Development builds as images and binaries

An open-source SASE platform on WireGuard combining zero-trust VPN and proxy access, privileged access control and an AI gateway that understands identity.
- GitHub stars
- 24k
- Last commit
- today
- Latest release
- 1.26.0
- Self-hosted
- Yes
- Hosted version
- Available
pangolin.net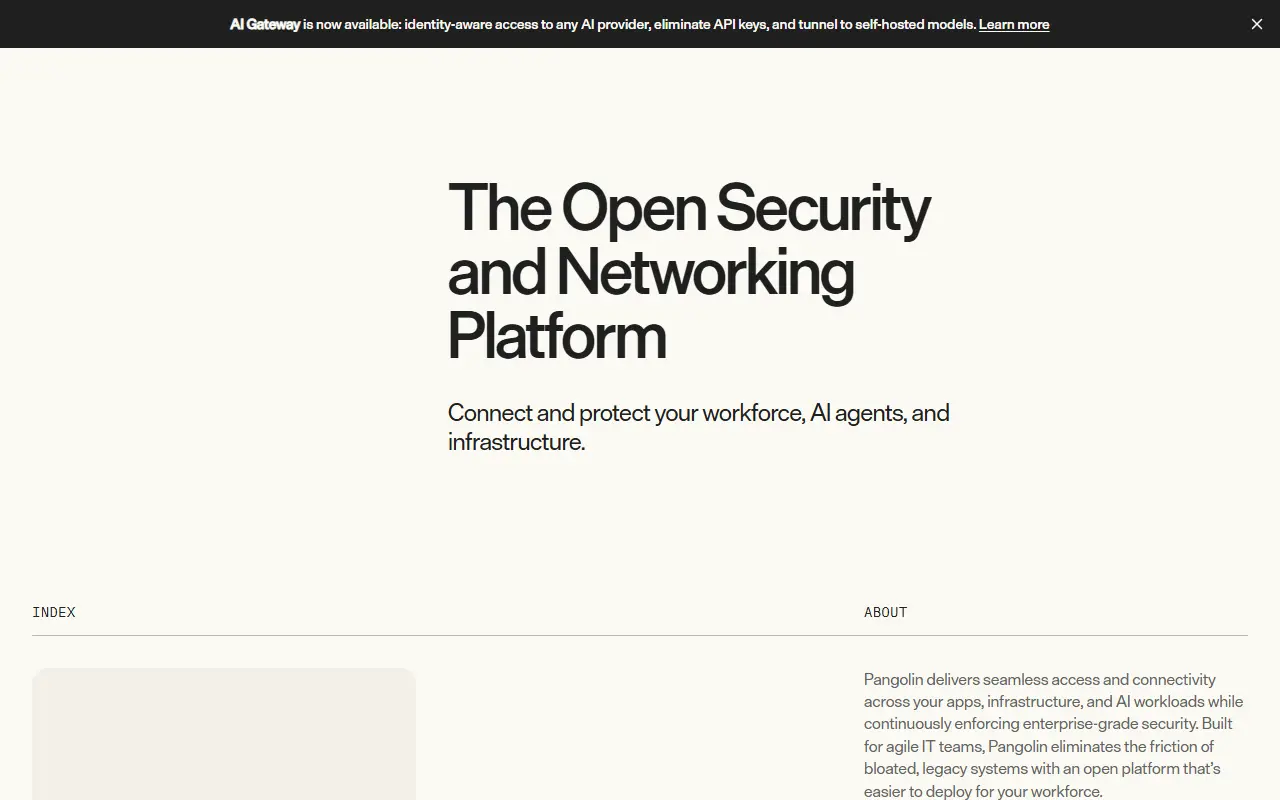
Pangolin is an open-source secure access service edge platform built on WireGuard. It aims to connect and protect users wherever they are by combining networking and security in one system: a zero-trust VPN, a zero-trust reverse proxy, privileged access control and a gateway for AI workloads that is aware of user identity, with one identity and policy model underneath.
The project compares its idea to commercial platforms such as Cloudflare One, Zscaler and Prisma, but argues that it is open, self-hostable and light enough to be easy to deploy. Legacy SASE products, it says, are heavy, closed and cloud-locked. Topics include reverse proxy, single sign-on, OIDC, SSH, tunneling, NAT traversal and remote access. Because the source is open to inspection, you can verify how traffic and access decisions are handled.
You can use Pangolin Cloud at app.pangolin.net or run it yourself. The repository's license is listed as 'Other' on GitHub, because it mixes open-source and enterprise components, so check the terms. It suits homelab users, small companies and IT teams that want zero-trust remote access without a large vendor contract.
Key features
- Zero-trust VPN built on WireGuard
- Zero-trust reverse proxy
- Privileged access management
- Identity-aware AI gateway
- Single identity and policy model
- Cloud or self-hosted deployment
Pricing: Basic is free for up to 5 users. Team costs $4 and Business $9 per user per month with a 10-day free trial; Enterprise is custom. Pangolin can run in the cloud or self-hosted.
#5
WireGuard Easy is a Docker-friendly tool that bundles a WireGuard VPN server with a web UI for managing clients on a Linux host.
- GitHub stars
- 27k
- Last commit
- 4 days ago
- Latest release
- v15.5.0
- Licence
- AGPL-3.0
- Self-hosted
- Yes
wg-easy.github.io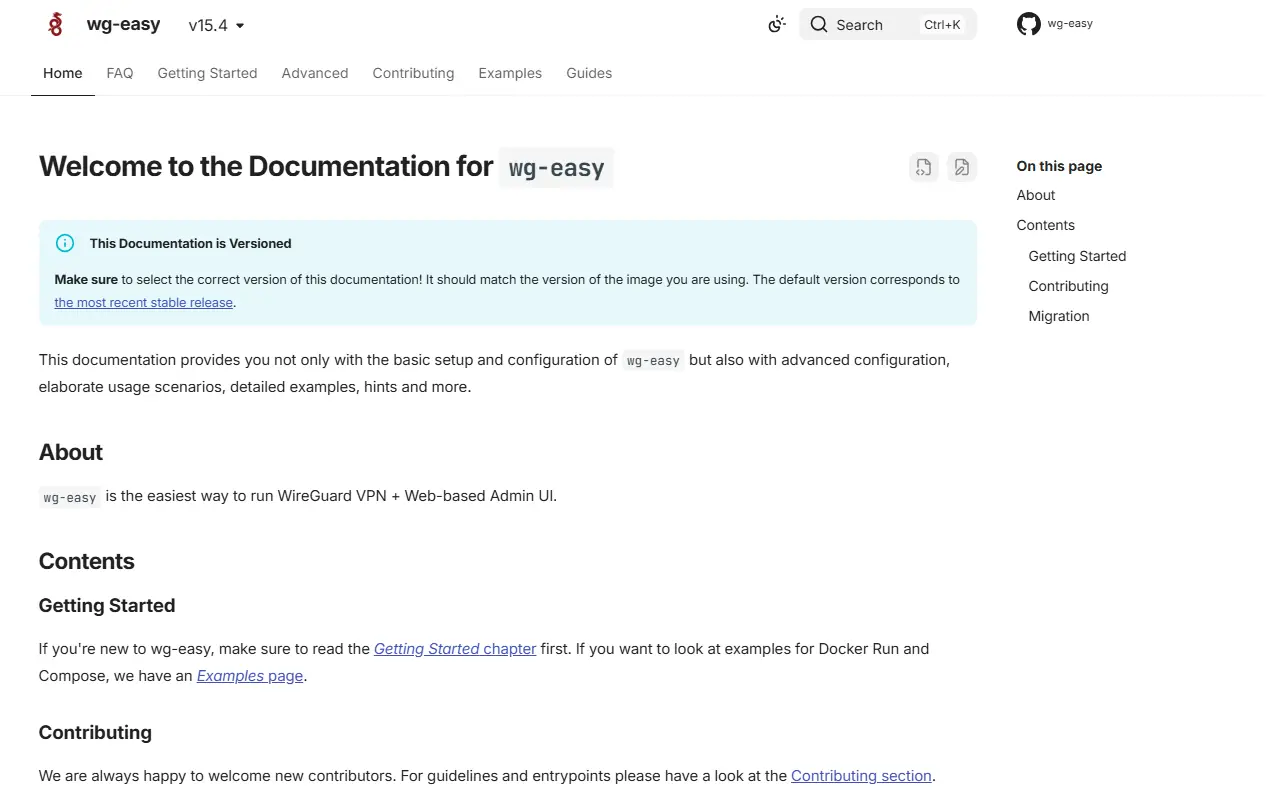
WireGuard Easy (wg-easy) combines a WireGuard VPN server and a web-based admin interface into a single package for Linux hosts. The web UI lets you list, create, edit, delete, enable and disable VPN clients, show a client's QR code, and download its configuration file. It is written in TypeScript and released under the AGPL-3.0 license.
Monitoring and security options include connection statistics, transmit and receive charts for each client, Prometheus metrics, client expiration, one-time links, two-factor authentication, OIDC sign-in with providers such as Google, GitHub, Authelia and Authentik, and per-client firewall filtering that requires iptables. The interface supports light and dark modes, multiple languages, IPv6 and CIDR. Installation uses Docker Compose, docker run or Podman, and the documentation covers reverse proxy setups with Caddy and Traefik as well as a migration guide from older versions.
Key features
- WireGuard server with a web admin UI
- Client QR codes and config downloads
- Per-client traffic charts and connection status
- Client expiration and one-time links
- Two-factor and OIDC sign-in support
- Prometheus metrics and IPv6 support
Pricing: Free and open source under the AGPL-3.0 license.
#6
Nebula is an open-source overlay networking tool that connects computers anywhere with encrypted, certificate-authenticated peer-to-peer links.
- GitHub stars
- 19k
- Last commit
- 3 days ago
- Latest release
- v1.12.0
- Licence
- MIT
- Self-hosted
- Yes
- Hosted version
- Available
Nebula is a mutually authenticated peer-to-peer software-defined network built on the Noise Protocol Framework. Certificates assert each node's IP address, name and membership in user-defined groups, and those groups drive traffic filtering between nodes regardless of cloud provider. It combines encryption, security groups, certificates and tunneling, and uses ECDH key exchange with AES-256-GCM by default.
Discovery nodes called lighthouses let peers find each other and optionally use UDP hole punching to connect from behind most firewalls and NATs. Data can move between nodes in any mix of cloud providers, datacenters and endpoints without a fixed addressing scheme. The README says it can link a handful of machines or tens of thousands.
To set one up you need the nebula binaries and nebula-cert, at least one lighthouse with a routable IP, a certificate authority, signed host certificates and a config file per host. It runs on Linux, macOS, Windows and FreeBSD, and is packaged for Arch, Fedora, Debian, Alpine, Homebrew and Docker; iOS and Android are source-only. Defined Networking offers a managed version.
Key features
- Mutually authenticated peer-to-peer network on Noise Protocol
- Certificates define IP, name and group membership
- Group-based traffic filtering independent of provider
- Lighthouses help peers find each other and punch through NAT
- Scales from a few computers to tens of thousands
- Runs on Linux, macOS, Windows, iOS and Android

OpenVPN is an open-source VPN daemon, developed in C, for creating secure virtual private network connections.
- GitHub stars
- 15k
- Last commit
- yesterday
- Latest release
- v2.7.9
- Self-hosted
- Yes
community.openvpn.net
This entry is the OpenVPN source repository. OpenVPN is an open-source VPN daemon, a program that creates secure virtual private network connections between machines. The code is written in C, and the repository is tagged for security and VPN.
No readme or homepage details were available for this entry, so specifics about features, deployment and licensing are not listed here. The repository lists its license as 'Other', and the project community site is community.openvpn.net, which is the place to look for downloads, documentation and support.
Key features
- Open-source VPN daemon
- Secure virtual private network connections
- Written in C
- Community-supported project
Pricing: Self-hosted Access Server is free for up to 2 connections. Growth is $7 per connection per month on yearly billing with a 14-day trial; Enterprise is custom.
#8
A platform that automates WireGuard networks for mesh VPNs, remote access and site-to-site links, available as open-source self-hosted software or a managed SaaS.
- GitHub stars
- 12k
- Last commit
- yesterday
- Latest release
- v1.7.0
- Self-hosted
- Yes
- Hosted version
- Available
netmaker.io
Netmaker builds on WireGuard to create and manage virtual networks automatically, from a home lab to an enterprise. It markets itself as a zero trust networking platform for connecting devices, clouds and sites, with an admin UI so that networks do not have to be configured by hand with wg-quick files.
Its capabilities include WireGuard networks, mesh VPNs, remote access gateways, site-to-site connectivity, private DNS, access control lists and OAuth sign-in. Clients are available for Linux, Mac and Windows, and the server can be deployed with Docker or on Kubernetes. The topics also mention IPv6 support and overlay networking.
You can deploy the open-source server yourself, for example on an Ubuntu 24.04 cloud VM with a static public IP, using a quick-start script and opening the documented ports, or install the self-hosted Pro version. A managed Netmaker SaaS is also offered for those who want to skip operations. The repository lists the license as Other.
Key features
- Automated WireGuard network management
- Mesh VPNs and site-to-site links
- Remote access gateways
- Admin UI for network administration
- Access control lists and private DNS
- OAuth login support
- Clients for Linux, Mac and Windows
Pricing: The open-source edition is free to self-host. Team starts at $2 and Business at $4 per active connection per month, with a 7-day trial; a self-hosted Professional tier is $99 per month and Enterprise is custom.
#9
Firezone is a zero trust access platform based on WireGuard, released as open source, that replaces traditional VPNs with policy-based access to apps and networks.
- GitHub stars
- 9.2k
- Last commit
- yesterday
- Latest release
- headless-client-1.5.16
- Licence
- Apache-2.0
- Hosted version
- Available
firezone.dev
Firezone is a zero trust access platform that uses WireGuard and is published as open source. It is positioned as a replacement for a traditional VPN, connecting users to internal apps, services and networks through access policies rather than broad network-level rules.
Administrators define policies for resources and can restrict access by conditions such as device location and time of day, with every authorized connection visible by user, resource or policy. Users and groups sync from an identity provider, which simplifies onboarding and offboarding. Lightweight Gateways run as Linux binaries wherever access is needed, and using two or more Gateways gives automatic load balancing and failover. Hole-punching keeps protected resources hidden from the public internet.
Client apps are available for macOS, Windows, Linux, Android, ChromeOS and iOS. The codebase is licensed under Apache-2.0 and written largely in Elixir, with Rust used for networking components. The vendor offers a hosted admin portal, a free way to get started and a separate pricing page.
Key features
- WireGuard-based VPN replacement
- Access policies per resource and group
- Identity provider directory sync
- Conditional access by location and time
- Gateways with load balancing and failover
- Clients for desktop and mobile platforms
Pricing: Free Starter plan for up to 6 users. Team costs $5 per user per month, or $4.16 billed annually; Enterprise is quoted via sales. Source code can be self-hosted without vendor support.
#10
Octelium is a self-hosted zero trust access platform that can act as a VPN, ZTNA system, API and AI gateway, tunnel service or PaaS on Kubernetes.
- GitHub stars
- 4.2k
- Last commit
- today
- Latest release
- v0.50.0
- Licence
- AGPL-3.0
- Self-hosted
- Yes
octelium.com
Octelium is a self-hosted, open-source platform that unifies zero trust secure access under one system. It is flexible enough to act as a zero-config remote access VPN, a Zero Trust Network Access and BeyondCorp-style platform, an alternative to ngrok and Cloudflare Tunnel, an API gateway, an AI and LLM gateway, and an infrastructure for building MCP gateways and AI agent access.
Repository topics list attribute-based access control, policy as code, WireGuard, QUIC, SSO, multi-factor authentication, OpenTelemetry and SSH access. The README includes use cases, a feature overview, a guide to try it in a Codespace, CLI installation and instructions to install your first cluster. It is written in Go and runs on Kubernetes. It is compared to ngrok, Cloudflare Tunnel and Apigee for different roles.
Octelium is licensed under AGPL-3.0 and you operate the cluster yourself. It suits platform and security teams, homelab users and developers who want to replace several access, tunnel and gateway tools with one self-hosted system.
Key features
- Zero-config remote access VPN
- ZTNA and BeyondCorp-style access
- API, AI and MCP gateway capabilities
- Tunnel service as ngrok alternative
- Attribute-based policy as code
- Runs on Kubernetes clusters
Pricing: Free and open source under AGPL-3.0.
5 more Tailscale alternatives
Commercial Tailscale alternatives
Hosted, closed-source products that compete with Tailscale.
Tailscale alternatives: questions
- What is the best open-source alternative to Tailscale?
- frp is the top-ranked open-source alternative to Tailscale on Enlisted: frp is an Apache-2.0 reverse proxy written in Go that exposes servers behind a NAT or firewall to the internet over TCP, UDP, HTTP and HTTPS. Other strong options are NetBird, Headscale, Pangolin and wg-easy.
- What are the best commercial alternatives to Tailscale?
- NordLayer, Cloudflare Zero Trust, Twingate, Teleport and Cloudflare Tunnel are among the hosted, closed-source alternatives to Tailscale listed on Enlisted, which lists 10 in total. Compare their pricing and features on each tool page.
- Are these Tailscale alternatives free?
- All 15 are open source, so the code is free to use under its licence, and all of them can be self-hosted on your own server or computer. 8 also offer a paid or managed cloud version if you'd rather not host it yourself.
- How is this list of Tailscale alternatives ranked?
- By a score built from GitHub stars, star growth over the last 30 days and how recently the code changed. 14 of these projects shipped code in the last 30 days. Data is refreshed daily, and nobody can pay to move up.
 TrackMedia
 TrackRev